
On this page
ToggleAccess reviews are supposed to be your safety net. Instead, they often feel like a quarterly fire drill nobody wants to run.
Spreadsheets fly around. Managers approve access they don’t understand. Security teams chase responses. Compliance teams hold their breath. And at the end of it all, you’re left wondering: did we actually reduce risk or just check a box?
If that sounds familiar, you’re not alone. Most IAM and GRC teams aren’t struggling because they don’t care about access governance. They’re struggling because the process itself is broken.
This article breaks that down: why access reviews feel so painful today and how to redesign them using practical automation without overwhelming your teams with alerts, noise, or false confidence.
What are access reviews?
Access reviews (also called “user access reviews” or “entitlement reviews”) are periodic evaluations of who has access to what within an organization’s systems, applications, and data and whether that access is still appropriate.
The core idea is simple: over time, access rights accumulate. Employees change roles, contractors finish projects, people leave the company, and temporary permissions never get revoked. This “permission creep” creates security risk and compliance gaps. An access review is the formal process of catching and correcting it.
A typical access review involves:
- Scoping — deciding which systems, applications, or user groups to review (often prioritized by risk, e.g., systems with sensitive data or privileged accounts first).
- Reviewing entitlements — managers, system owners, or application owners examine each user’s access and confirm whether it’s still needed for their current role. This checks alignment with the principle of least privilege.
- Remediation — revoking or adjusting access that’s excessive, orphaned (belonging to departed users), or violates segregation of duties.
- Documentation — recording who reviewed what, decisions made, and actions taken, which becomes audit evidence.
They matter heavily for compliance. SOC 2, ISO 27001, HIPAA, PCI DSS, and SOX all expect organizations to demonstrate that access is granted appropriately and reviewed regularly; quarterly reviews are common for privileged access, with semi-annual or annual cadences for lower-risk systems. Auditors will typically ask for completed review records as evidence.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MoreWhy access reviews feel like busywork (but still keep you up at night)
Let’s call it what it is: most access reviews are performative.
They exist to satisfy auditors, not to meaningfully reduce risk. But the irony is, they still create real operational pain.
Here’s what’s typically going wrong:
- Reviews are too broad. Every user, every system, every entitlement gets dumped into one massive certification cycle.
- Context is missing. Reviewers don’t know what access actually does, so they default to “approve.”
- Timing is arbitrary. Quarterly or annual reviews don’t reflect how fast access risk actually changes.
- Ownership is unclear. Managers are assigned reviews without understanding their accountability.
- Tooling is fragmented. Data lives across IAM tools, ticketing systems, spreadsheets, and emails.
The result? Fatigue across every stakeholder.
IAM teams feel buried. Compliance teams worry about audit defensibility. And business users treat reviews like spam.
The real risk hiding behind “approve all.”
When reviewers don’t understand what they’re approving, they approve everything.
That’s not laziness; it’s a design flaw.
Here’s what that leads to:
Issue | What it looks like | Why it matters |
Privilege creep | Users accumulate access over time | Expands attack surface silently |
Orphaned access | Access persists after role change or exit | Violates least privilege |
Toxic combinations | Conflicting entitlements go unnoticed | Increases fraud and compliance risk |
Shadow access | Access granted outside formal systems | Undermines audit trails |
And here’s the uncomfortable truth: most of these risks are already known during reviews, but buried in noise.
Read the “Access control policies for strong data security in 2026” article to learn more!
Alert fatigue is killing your identity governance program
Automation was supposed to fix access reviews.
Instead, many organizations replaced manual chaos with automated chaos.
Too many alerts. Too many campaigns. Too little prioritization.
Here’s how alert fatigue shows up in IAM:
- Every minor change triggers a review task
- Low-risk access is treated the same as high-risk privileges
- Reviewers receive generic notifications with no context
- Escalations pile up without clear ownership
Eventually, users tune out.
And when everything feels urgent, nothing actually is.
What good access reviews actually look like
Let’s reset expectations.
Effective access reviews aren’t about reviewing everything; they’re about reviewing the right things, at the right time, with the right context.
A well-designed program has three key characteristics:
1. risk-based, not schedule-based
Instead of reviewing access every quarter, reviews are triggered by risk signals:
- Role changes
- Privilege escalations
- Unusual access patterns
- Sensitive data exposure
2. contextual, not generic
Reviewers see:
- What the access enables
- When it was last used
- Whether it aligns with the user’s role
- Peer comparisons (who else has similar access)
3. Continuous, not episodic
Access governance becomes an ongoing process, not a quarterly event.
Small, meaningful decisions replace large, overwhelming campaigns.
AI-native GRC transformation for enterprise CISOs
Trusted by Fortune 500 and Global 2000 in 10+ verticals. TrustCloud offers the only Continuous Control Monitoring that tests for any control, or any objective, using millions of data points. Provable cyber risk assurance and productivity and business value acceleration in weeks, not months.
The automation blueprint: how to fix access reviews without breaking your team
Let’s move from theory to execution.
Here’s a practical blueprint IAM and GRC teams can actually implement, without ripping out their entire stack.
Step 1: start with access intelligence, not automation
Before automating anything, fix your visibility.
You need to answer:
- Who has access to what?
- Why do they have it?
- How is it being used?
Focus on:
- Identity-to-entitlement mapping
- Role clarity (even if imperfect)
Usage data (last login, frequency, anomalies)
Without this foundation, automation just scales confusion.
Step 2: Classify access by risk
Not all access deserves the same scrutiny.
Create a simple risk model:
Access type | Risk level | Example |
Sensitive systems | High | Production databases, financial systems |
Privileged roles | High | Admin, root, superuser |
Business-critical apps | Medium | CRM, ERP |
Low-impact tools | Low | Internal portals, collaboration tools |
Then map review frequency and rigor accordingly.
High-risk access → continuous or event-driven reviews
Low-risk access → periodic or automated approvals
Step 3: Trigger reviews based on events, not calendars
Shift from scheduled campaigns to event-driven reviews.
Key triggers:
- New access grants (especially privileged)
- Role or department changes
- Terminations or offboarding gaps
- Policy violations (e.g., segregation of duties conflicts)
Example:
Instead of reviewing all finance system access quarterly, trigger a review when:
- A user gains admin privileges
- A user transfers into finance
- A dormant account becomes active again
This dramatically reduces volume while increasing relevance.
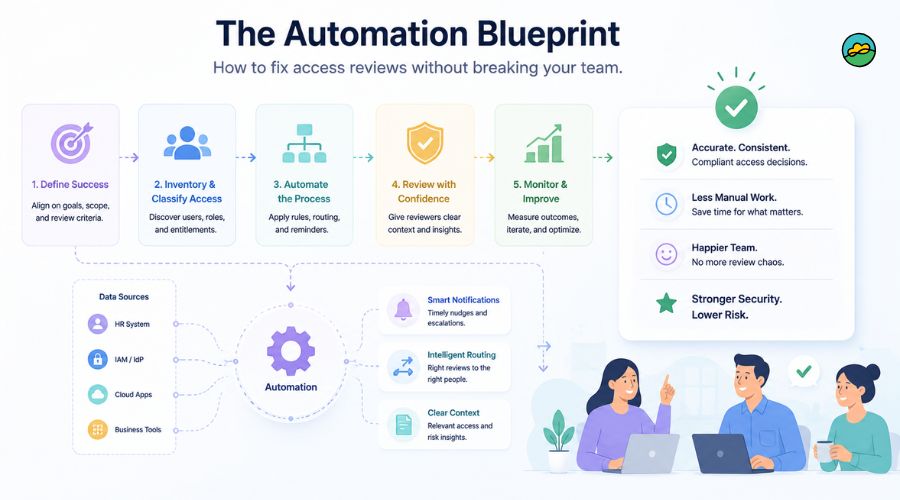
Step 4: Enrich every review with context
This is where most programs fail.
A good review decision requires context. Without it, reviewers default to approval.
Include:
- Access description (what does it actually do?)
- Usage insights (last used, frequency)
- Risk indicators (sensitive system, elevated privileges)
- Peer comparison (who else has similar access?)
- Recommendation (approve, revoke, investigate)
Example:
Instead of:
“User has access to System X – Approve or Revoke?”
Show:
“User has admin access to the production database. Last used: 120 days ago. Only 2 other users have this role. Recommendation: Revoke.”
That changes behavior instantly.
Step 5: Automate the obvious decisions
Not every decision needs a human.
Automate low-risk, high-confidence scenarios:
- Remove unused access after defined inactivity thresholds
- Auto-approve access aligned with role-based policies
- Flag and quarantine orphaned accounts
- Revoke access post-termination automatically
This reduces review workload significantly.
Step 6: Design for reviewer experience (this matters more than you think)
If your reviewers hate the process, your program will fail.
Make it easy:
- Bundle decisions logically (by system, role, or risk level)
- Allow bulk actions with guardrails
- Provide clear deadlines and reminders
- Keep interfaces simple and fast
- Think of it like UX design, not compliance enforcement.
Step 7: Close the loop with audit-ready evidence
Automation isn’t just about efficiency; it’s about defensibility.
Ensure you capture:
- Who reviewed what
- What decision was made
- What context was presented
- When the action occurred
This creates a clean audit trail without manual effort.
Read the “Empower employees with seamless access to policies & procedures to unlock compliance & efficiency” article to learn more!
What this looks like in practice
Let’s compare traditional vs. modern access review approaches:
| Traditional approach | Modern automated approach |
| Quarterly bulk reviews | Continuous, event-driven reviews |
| Spreadsheet-based tracking | Integrated IAM + governance tools |
| Reviewer guesswork | Context-rich decision support |
| High volume, low accuracy | Low volume, high impact |
| Audit-driven mindset | Risk-driven mindset |
Common pitfalls (and how to avoid them)
Even with the right blueprint, teams can fall into familiar traps.
Over-automating too quickly
Jumping straight into automation without clean data leads to bad decisions at scale.
Fix: Start with visibility and classification first.
Ignoring business context
Security teams often design reviews without involving business owners.
Fix: Collaborate with application owners and managers early.
Treating all alerts equally
If everything is flagged, nothing stands out.
Fix: Prioritize based on risk and impact.
Failing to measure effectiveness
If you’re not tracking outcomes, you’re guessing.
Fix:
- Monitor metrics like the following:
- Access revocation rates
- Review completion time
- Percentage of automated decisions
- Reduction in privileged access sprawl
The bigger shift: from compliance exercise to risk control
This is the mindset shift that separates mature IAM programs from struggling ones.
Access reviews shouldn’t exist just to pass audits. They should:
- Reduce unnecessary access
- Detect risky entitlements early
- Align access with real business roles
- Strengthen your overall security posture
When done right, audits become easier, not harder.
A simple example to bring it all together
Imagine a mid-sized enterprise with 5,000 employees.
Old approach:
- Quarterly reviews across 50 systems
- 20,000+ access decisions per cycle
- 80% approvals with little scrutiny
- Weeks of follow-ups and escalations
New approach:
- Event-driven reviews for high-risk access
- Automated cleanup of unused accounts
- Context-rich decisions for managers
- Review volume reduced by 60–70%
- Higher-quality decisions with less effort
Same goal. Completely different experience.
Where to start if your program feels stuck
If you’re overwhelmed, don’t try to fix everything at once.
Start small:
- Pick 1–2 critical systems (e.g., finance, production)
- Define high-risk access categories
Introduce event-based triggers - Add context to review decisions
- Automate one low-risk scenario
Then expand.
Progress beats perfection here.
Access reviews don’t have to be painful, performative, or ignored.
When you shift from volume to value, from schedules to signals, and from manual effort to thoughtful automation, you don’t just make reviews easier.
You make them actually work.
FAQs
What are access reviews, and why do organizations need them?
Access reviews, also known as user access reviews or entitlement reviews, are periodic evaluations of who has access to which systems, applications, and data within an organization, and whether that access remains appropriate. Over time, permissions accumulate as employees change roles, contractors complete projects, and temporary access is never revoked, creating security risks and compliance gaps.
Access reviews formally catch and correct this permission creep, and frameworks like SOC 2, ISO 27001, HIPAA, PCI DSS, and SOX expect organizations to demonstrate regular reviews as audit evidence.
How does alert fatigue undermine identity governance programs?
Alert fatigue occurs when automation generates excessive, unprioritized review tasks that overwhelm reviewers instead of helping them. Every minor change triggers a review, low-risk access receives the same treatment as high-risk privileges, and generic notifications arrive with no context or clear ownership.
As a result, reviewers gradually tune out, and when everything feels urgent, nothing actually is. Many organizations that adopted automation simply replaced manual chaos with automated chaos, which erodes the effectiveness and credibility of the entire identity governance program.
What steps can organizations take to automate access reviews without overwhelming their teams?
Organizations should begin with access intelligence, mapping identities to entitlements and understanding how access is actually used, before automating anything. Next, they should classify access by risk level, trigger reviews based on events such as role changes or privilege escalations rather than fixed calendars, and enrich every review with context like usage data and peer comparisons.
Automating obvious, low-risk decisions, designing a simple reviewer experience, and capturing audit-ready evidence complete the blueprint, significantly reducing review volume while improving decision quality.