

Overview
In the evolving cybersecurity landscape, traditional perimeter-based defenses are no longer sufficient. The increasing sophistication of cyberattacks demands a more nuanced approach, and that is where zero-trust principles come into play. At the heart of this approach is reinforced identity management, which serves as the foundation for ensuring that every user, device, and network component is verified before granting access.
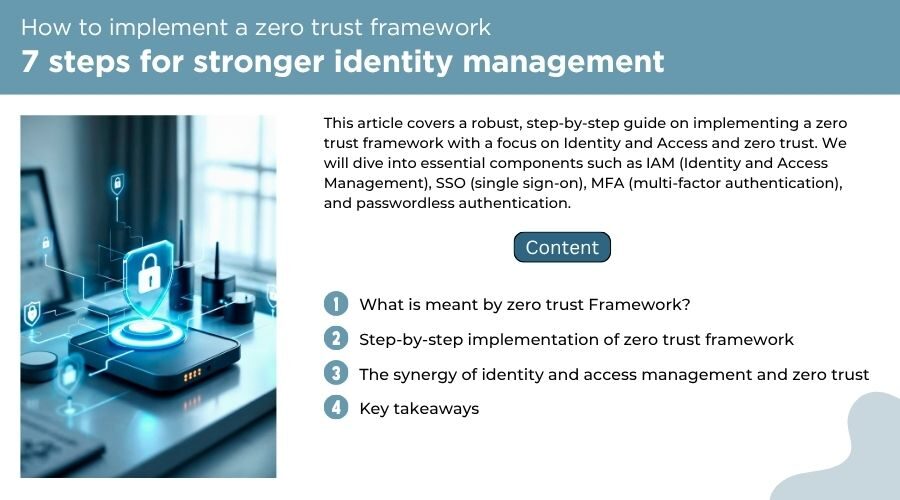
Image source: freepik.com
This article covers a robust, step-by-step guide on implementing a zero-trust framework with a focus on Identity and Access and zero-trust. We will dive into essential components such as IAM (Identity and Access Management), SSO (single sign-on), MFA (multi-factor authentication), and passwordless authentication. Designed with IT security managers and professionals in mind, these seven steps serve as a detailed blueprint for transitioning to a secure environment where identity verification is paramount.
What is meant by zero-trust framework?
The zero-trust framework is a modern cybersecurity model based on the principle of “never trust, always verify.” Unlike traditional security approaches that rely heavily on perimeter defenses—assuming everything inside the network is safe—zero-trust assumes that threats can exist both outside and inside the network. Therefore, no user, device, or application is inherently trusted, regardless of their location or previous access.
At the core of the zero-trust model is continuous verification. Every access request is authenticated, authorized, and validated based on multiple factors such as user identity, device posture, location, time, and the sensitivity of the resource being accessed. This means even employees or systems that are already within the network must prove their trustworthiness each time they request access to data or services.
Another key component is least privilege access, where users are given only the minimum level of access necessary to perform their job. This limits the potential damage of compromised credentials or insider threats. Additionally, micro-segmentation is used to divide the network into smaller zones, reducing the risk of lateral movement if a breach occurs.
The zero-trust framework also emphasizes visibility and analytics, using real-time monitoring and AI-driven tools to detect abnormal behavior and potential threats. It integrates with various technologies such as identity and access management (IAM), multi-factor authentication (MFA), endpoint detection and response (EDR), and secure access service edge (SASE).
In essence, zero-trust is not a single technology but a strategic approach that reshapes how organizations think about and implement security. It is particularly relevant in today’s landscape of remote work, cloud computing, and increasing cyber threats, as it helps protect data and systems regardless of where users and devices are located.
Read the “Transform vulnerability management with smart automation” to learn more!
Step-by-step implementation of zero-trust framework
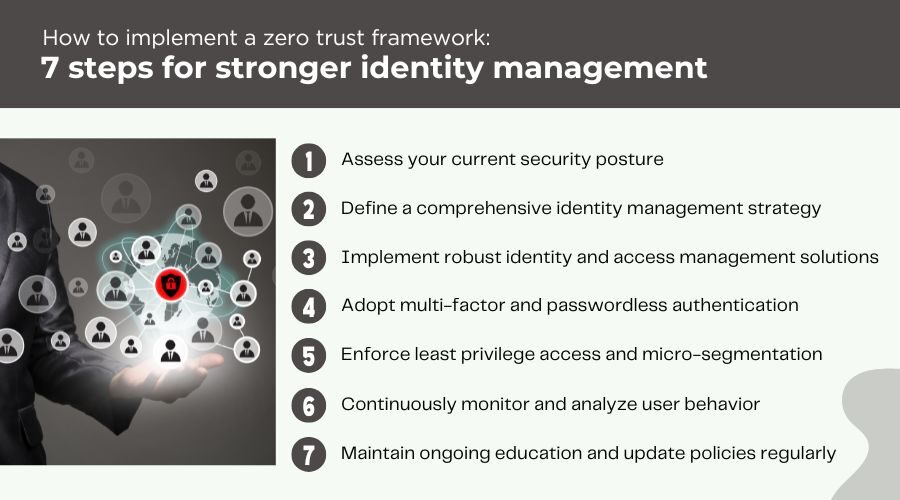
Image source: freepik.com
Step 1: Assess your current security posture
The journey toward a zero-trust framework begins with an honest and comprehensive assessment of your current security environment. Before you can implement the necessary changes, it is critical to understand your existing identity management protocols, network architecture, and key vulnerabilities. This stage involves a deep dive into your IT infrastructure to identify potential risk areas — such as outdated IAM processes, unpatched systems, or weak access controls — where unauthorized users might exploit vulnerabilities.
Begin by conducting a thorough audit that includes both technical assessments and policy reviews. Consider questions such as:
What methods are currently used to authenticate users?
Is there an effective SSO solution in place to streamline user access?
How are MFA solutions integrated into existing systems, and what is the reliance on traditional passwords?
This analysis not only helps in pinpointing existing security gaps but also in defining a clear baseline from which you can measure improvements.
Additionally, include an evaluation of your IT asset inventory. Mapping every device, user, application, and service is essential because a zero-trust framework mandates that nothing – no matter how benign it seems – should be implicitly trusted. With a detailed understanding of your current environment, you are well-prepared to design a strategic roadmap that reinforces “Identity and Access and zero-trust,” setting the stage for robust identity management.
Step 2: Define a comprehensive identity management strategy
A comprehensive identity management strategy is the cornerstone of a zero-trust framework, with Identity and Access and zero-trust at its epicenter. The objective is to ensure that every user or device is authenticated, authorized, and continuously verified before accessing any resource.
At this stage, align your security goals with business objectives. Collaborate with both IT and business stakeholders to define what success looks like. Outline clear objectives that encompass the integration of solutions like IAM, SSO, MFA, and even password less authentication options. Planning involves considering the roles and responsibilities across the organization, mapping out access patterns, and determining which data and applications require heightened security.
Develop a policy framework that dictates how identities are created, managed, and revoked. In a strong zero-trust posture, identity becomes the primary boundary instead of the network perimeter. Consider architectures that support federated identities and adopt standards like SAML, OAuth, and OpenID Connect to facilitate secure identity exchanges. By ensuring that identities are at the forefront of your cybersecurity operations, you place your organization at a significant advantage when facing contemporary cyber threats.
Step 3: Implement robust identity and access management solutions
With your strategy in place, the subsequent step is to practically implement Identity and Access Management (IAM) solutions designed to enforce the principles of zero-trust. This step revolves around selecting, integrating, and configuring tools that verify every access request without exception, maintaining continuous security monitoring.
A modern IAM system should seamlessly incorporate SSO, MFA, and even cutting-edge passwordless authentication to minimize security risks. SSO simplifies the user experience by allowing individuals to authenticate once and gain access to multiple systems, while MFA provides an extra layer of security through multiple verification methods — including SMS, biometrics, or hardware tokens. Password less authentication further enhances security by completely eliminating the vulnerabilities associated with password-based systems.
Furthermore, ensure that your IAM solution supports policy-based access control. This allows you to enforce dynamic policies that consider factors such as the user’s role, device posture, location, and even time of access. Integration with directory services and cloud-based identity providers ensures that both on-premise and remote users adhere to the same security protocols, creating a seamless and secure digital environment.
Step 4: Adopt multi-factor and passwordless authentication
While robust IAM systems are critical, the authentication process itself must be airtight. This is where implementing MFA and password less authentication steps in as a non-negotiable requirement. Relying solely on passwords is increasingly recognized as insufficient due to widespread phishing and credential-stuffing attacks.
MFA enhances security by requiring two or more independent credentials for authentication.
For instance, after entering a password, a user may need to confirm their identity through a one-time code sent via SMS, or use a biometric scan. This extra verification layer significantly reduces the risk of unauthorized access even when passwords are compromised.
On the other hand, password less authentication leverages alternatives such as biometrics or hardware tokens. This not only simplifies the user experience by eliminating the need to manage multiple, complex passwords, but it also minimizes the attack surface.
Integrating both MFA and password less methods into your IAM suite ensures that the authentication process is robust enough to meet today’s security challenges. Choose solutions that are flexible enough to adapt to different user contexts while maintaining compliance with industry standards and regulations.
Step 5: Enforce least privilege access and micro-segmentation
The principle of least privilege – granting users access only to the resources essential for performing their job functions – is a critical component in any zero-trust framework. The goal is to reduce the attack surface by ensuring that trust is segmented to the narrowest possible scope.
To effectively enforce least privilege, update your policies to ensure that no user, process, or device is given broader access than necessary. This not only limits potential damage from compromised accounts but also makes it easier to track abnormal behavior. Coupled with this, apply micro-segmentation techniques to divide your network into smaller, isolated zones. By doing so, even if one segment is breached, attackers will not be able to move laterally across your entire network.
This dual approach – employing both least privilege access and micro-segmentation – ensures that even sophisticated threats are contained within limited boundaries, reducing the overall impact of potential breaches. zero-trust is built around the idea that trust should never be inherited; instead, it must be continuously evaluated, and least privilege access is central to this philosophy.
Step 6: Continuously monitor and analyze user behavior
A zero-trust framework is not a one-time investment but an ongoing commitment to continuously monitor and assess security levels. In modern cybersecurity frameworks, real-time behavioral analytics play a pivotal role in safeguarding critical systems and data.
Implement systems that log and analyze data for every authentication and authorization event across your network. By continuously assessing metrics such as login times, user behavior on applications, and access patterns, you can identify anomalies that indicate malicious activities. Technologies such as Security Information and Event Management (SIEM) systems and User and Entity Behavior Analytics (UEBA) tools can help to correlate events and provide insights that allow for swift remediation.
Moreover, integrate automated responses for when suspicious behavior is detected. For example, if a user suddenly attempts to access sensitive data from an unusual location or outside of typical hours, an automated system can trigger additional authentication or temporarily suspend access until the legitimacy of the request can be confirmed. Continuous monitoring is the lifeblood of zero-trust, ensuring that your defenses remain agile and responsive to an ever-changing threat landscape.
Step 7: Maintain ongoing education and update policies regularly
The final step in implementing a zero-trust framework is to cultivate a culture of continuous improvement and ongoing education. Cybersecurity is an evolving field, and what works today might not be sufficient tomorrow. For IT security managers and professionals, it is crucial to stay informed about emerging threats, industry best practices, and new technologies that can further strengthen identity management.
Regularly update your security policies and protocols based on feedback from security audits, incident reports, and evolving regulatory requirements. Establish a process for periodic training sessions and workshops for both IT personnel and end-users to reinforce the importance of strict identity validation and adherence to security protocols. As new authentication technologies emerge, such as advanced biometric systems or behavioral analytics, continuously evaluate their potential benefits to enhance your existing framework.
In addition, encourage open communication within your organization about cybersecurity challenges and successes. Regular internal reviews and threat simulation exercises can provide critical insights into the effectiveness of your implementation. This proactive approach not only helps in fine-tuning your zero-trust architecture but also cultivates an environment where cybersecurity is everyone’s responsibility.
Read the Unveiling the Truth: Is GMail HIPAA Compliant” article to learn more!
The synergy of identity and access management and zero-trust
The implementation phases outlined in these seven steps are designed to complement each other and collectively bolster your organization’s cybersecurity posture. Central to this integrated approach is the marriage between Identity and Access and zero-trust. With modern threats constantly evolving, preserving the sanctity of identity becomes a mission-critical factor. In a zero-trust model, identity management is the primary line of defense against breaches. This framework mandates that trust is not automatically granted based on network location or device but rather earned through continuous validation.
By heavily investing in robust IAM, SSO, MFA, and password less authentication solutions, you create multiple layers of defense that work in tandem. Each component plays a specific role: IAM serves as the system’s backbone, SSO enhances user efficiency, MFA provides redundancy in authentication, and passwordless options reduce the risks associated with traditional password systems. Together, these components create a resilient and agile framework capable of adapting to new threats.
The result is a robust security posture that minimizes the risks of data breaches, unauthorized access, and potential lateral movement by adversaries.
Furthermore, the combined approach of continuous monitoring and regular policy updates ensures that your security protocols evolve in tandem with the threat landscape. This dynamic approach to cybersecurity is essential in an era where attackers can exploit even the smallest vulnerabilities.
Key takeaways
Implementing a zero-trust framework requires a holistic and disciplined approach that places identity at its very core. By following these seven steps – assessing your current security posture, defining a comprehensive identity management strategy, implementing robust IAM solutions, adopting MFA and passwordless authentication, enforcing least privilege access and micro-segmentation, continuously monitoring user behavior, and maintaining ongoing education – organizations can significantly enhance their cybersecurity defenses.
In an age where every digital interaction must be scrutinized, the integration of Identity and Access and zero-trust is not just a buzzword; it is a necessary paradigm shift for mitigating risks and ensuring long-term resilience. For IT security managers and professionals, the move to a zero-trust environment is challenging but essential. Through meticulous planning, consistent monitoring, and a commitment to innovation in identity management, you can create a secure foundation that stands up to the evolving threats of today and tomorrow.
Embrace the zero-trust philosophy and continuously refine your identity management strategies, because in cybersecurity, adaptive defenses are the best deterrents against an ever-persistent adversary.
Ready to save time and money on audits, pass security reviews faster, and manage enterprise-wide risk? Let’s talk!