

Overview
For IT managers at small and medium enterprises (SMEs), the landscape of cybersecurity is ever-changing and increasingly complex. Compliance audits are now integral to ensuring that an organization’s information systems meet both regulatory and industry standards. This article provides a framework to help you successfully prepare for your first cybersecurity compliance audit.
With clear, actionable advice, IT managers can navigate the complexities of compliance, strengthen their security posture, and ensure long-term resilience against cyber threats. Below, we outline seven essential steps to help you prepare for your cybersecurity compliance audit.
What is the importance of cybersecurity compliance for SMEs?
Cybersecurity compliance is not merely about checking a box to satisfy regulatory bodies; it is a critical component of your overall information security strategy. For SMEs, the consequences of non-compliance can be severe—ranging from hefty fines to reputational damage and even operational disruptions.
Given that SMEs frequently have fewer resources than larger enterprises, establishing robust cybersecurity measures early on can mean the difference between swiftly averting a crisis and enduring a prolonged incident.
Moreover, compliance audits provide an external view of your organization’s security controls, helping identify vulnerabilities and areas needing improvement. Adopting proactive measures to pass an audit not only ensures that you meet legal requirements but also reinforces customer trust and establishes a culture of security within your company. The journey toward compliance is one that demands meticulous planning, ongoing education, and a sincere commitment to upholding industry best practices.
Read the “Robust vulnerability management practices: Unlocking cybersecurity excellence” article to learn more!
Preparing for your first cybersecurity compliance audit in 7 steps
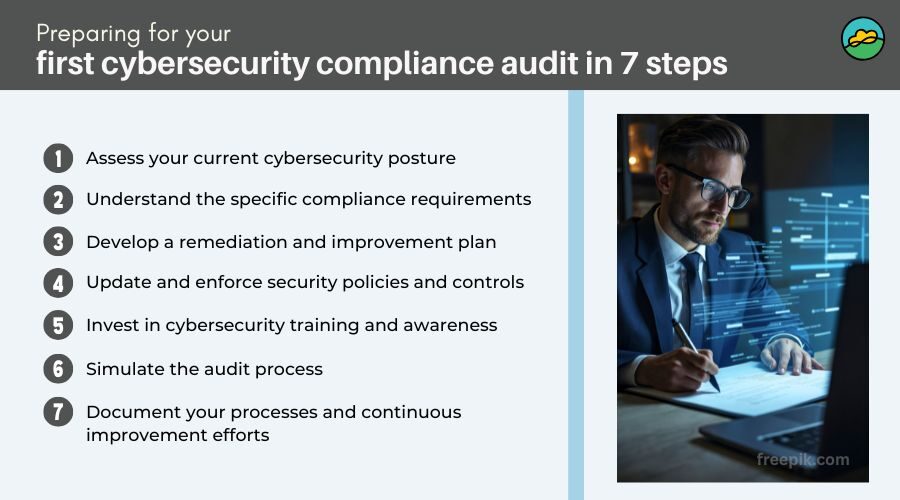
Step 1: Assess your current cybersecurity posture
The first step in preparing for your cybersecurity compliance audit is to evaluate your current security infrastructure and policies. This involves an in-depth assessment of your systems, data protection methods, and risk management procedures. Understanding where you stand is crucial in determining gaps in security and compliance.
Begin by conducting a comprehensive security audit of your network, endpoints, and data repositories. Consider engaging both internal teams and external cybersecurity consultants to obtain an objective overview. Use established frameworks and assessment tools to help identify any weaknesses. Key areas to focus on include
- Network security measures (firewalls, intrusion detection systems, and access controls)
- Data encryption practices for data at rest and in transit
- Patch management and software updates
- User access and privilege controls
- Incident response procedures
This initial assessment should provide you with a roadmap for prioritizing remediation initiatives and highlight areas requiring immediate attention before the audit.
Step 2: Understand the specific compliance requirements
Each industry and region can have its own set of cybersecurity compliance mandates. For an SME, understanding which regulations are applicable to your operations is paramount. Common standards include the General Data Protection Regulation (GDPR), Health Insurance Portability and Accountability Act (HIPAA), Payment Card Industry Data Security Standard (PCI DSS), and other industry-specific guidelines.
To begin, gather information from regulatory agencies and industry groups to identify all relevant compliance criteria. Document these requirements and map them to your current cybersecurity posture as identified in the initial assessment. This alignment helps you pinpoint areas where your security practices may fall short of standards, allowing you to prioritize modifications accordingly.
In addition to formal requirements, consider industry best practices that might enhance your security defenses. Engage legal counsel or compliance experts when needed to ensure a comprehensive understanding of applicable regulations.
Step 3: Develop a remediation and improvement plan
Once vulnerabilities and compliance gaps are identified, creating a detailed remediation plan becomes the next critical step. This plan should outline specific action items, prioritize tasks based on risk, and assign responsibilities to team members.
Begin by categorizing the risk associated with each gap—whether it is high, medium, or low—and focus initially on high-risk areas that could lead to compliance failures or severe security breaches. The development of this plan should include:
- Clearly defined remediation steps for each identified vulnerability
- Timelines for implementing changes and achieving compliance
- Assigned resources and defined responsibilities for IT teams and relevant stakeholders
- Establishing metrics and key performance indicators (KPIs) to measure progress
- Setting up periodic review points to assess the effectiveness of the remediation efforts
This systematic approach helps ensure that all identified issues are addressed before the auditing process and supports ongoing efforts to strengthen your overall security posture.
Step 4: Update and enforce security policies and controls
For compliance audits, robust policies and clearly enforced security controls play a pivotal role. This step involves reviewing and updating your company’s cybersecurity policies, ensuring they align with the latest compliance standards and best practices.
Review existing security policies such as access control, data privacy, password management, incident response, and remote access guidelines. Update these documents to reflect any changes introduced by new regulations or improvements from your remediation plan. In parallel, you should ensure that the technical controls (such as firewalls, antivirus solutions, encryption protocols, and intrusion detection systems) are adequately configured and maintained.
Effective policy updates are only as good as their implementation. Ensure robust training programs are in place so that all employees are aware of and follow these guidelines. Additionally, implement regular internal audits to check that policies are being followed and that any discrepancies are promptly corrected.
Step 5: Invest in cybersecurity training and awareness
It is widely recognized that employees are often the weakest link in an organization’s cybersecurity defenses. For SMEs, where resources might be limited, a focus on cybersecurity awareness is an essential cost-effective measure.
Develop and implement a comprehensive training program that educates employees about cybersecurity risks, safe online practices, and the specific policies your organization has adopted. Topics should include:
- Recognizing phishing attempts and social engineering attacks
- Proper handling of sensitive data
- Reporting suspicious activities and potential security incidents
- Understanding the consequences of non-compliance and security breaches
Regular training sessions, combined with periodic simulations such as phishing tests, can dramatically reduce the likelihood of human error leading to a breach. Empower employees to take cybersecurity seriously by creating a culture of continuous learning and vigilance. Such initiatives also demonstrate to auditors that your organization is proactive in building a secure environment.
Step 6: Simulate the audit process
Before the actual cybersecurity audit, conducting an internal simulation is invaluable. A mock audit helps to uncover additional areas of improvement and prepares your team for the rigorous scrutiny that will accompany the formal audit.
Arrange an internal review or hire an external consultant who specializes in compliance audits. This simulation should include:
- Testing the efficiency of your cybersecurity controls
- Verifying that documentation is complete and accurate
- Assessing the response protocols in the event of a security breach
- Reviewing the record-keeping practices to ensure all compliance-related activities are properly documented
Through a simulated audit, you can identify unforeseen issues or process gaps before the actual audit. This initiative not only strengthens your security defenses but also minimizes any potential disruptions during the formal assessment.
Step 7: Document your processes and continuous improvement efforts
Comprehensive documentation is the cornerstone of any successful cybersecurity compliance effort. Auditors rely on thorough records to verify that your organization adheres to the required standards. Ensure that all processes, policies, and remediation activities are meticulously documented.
Documentation should cover:
- Security policies and procedures, including any updates or changes
- Results from risk assessments and vulnerability scans
- Details of remediation efforts, including timelines and responsible parties
- Records of internal audits and training sessions
- Incident response logs and post-incident reviews
Maintaining comprehensive records not only smooths the audit process but also provides a continuous improvement trail. Use these documents to periodically review and update your security measures in line with emerging threats and evolving compliance standards.
Read the “Cybersecurity risks: a comprehensive guide for GRC professionals in 2025” article to learn more!

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn More