TrustCloud launches Application Assurance: AI-native continuous control monitoring for enterprises. Read more →

Unlock success: ISO 27001 vs SOC 2 – the ultimate security guide

Unlock success ISO 27001 vs SOC 2 – the ultimate security guide

Overview

ISO 27001 Certification and SOC 2 Attestation are both critical frameworks for ensuring information security, yet they serve different purposes and are tailored to distinct audiences. ISO 27001 is an internationally recognized standard that specifies the requirements for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS).

It is applicable to any organization, regardless of its size or industry. The certification process involves a comprehensive audit by an accredited external body to verify that the organization adheres to the stringent controls and policies outlined in the ISO 27001 standard. Achieving ISO 27001 certification demonstrates a robust commitment to information security management and can significantly enhance an organization’s credibility on a global scale.

In contrast, SOC 2 (Service Organization Control 2) Attestation is specifically designed for service providers that store customer data in the cloud. Developed by the American Institute of CPAs (AICPA), SOC 2 focuses on five “Trust Service Criteria”: security, availability, processing integrity, confidentiality, and privacy. Unlike ISO 27001, SOC 2 reports are not standardized certifications but attestations provided by independent auditors based on the organization’s adherence to these criteria.

SOC 2 attestation reports come in two types: Type I assesses the suitability of the design of controls at a specific point in time, while Type II evaluates the operating effectiveness of these controls over an extended period. While both ISO 27001 Certification and SOC 2 Attestation aim to ensure high standards of information security, their scopes and methodologies differ. ISO 27001 offers a holistic framework applicable across various industries, focusing on continuous improvement and comprehensive risk management.

On the other hand, SOC 2 is more narrowly focused on service providers handling customer data, providing detailed insights into specific control criteria relevant to cloud services. Understanding these differences is crucial for organizations aiming to align their security practices with industry standards while meeting stakeholder expectations effectively.

It is a common situation where you want to improve your data security but can’t decide between ISO 27001 certification and SOC 2 attestation. They both provide companies with strategic frameworks and standards to measure their security controls and systems. But what’s the difference, then?

ISO 27001, also known as ISO/IEC 27001, is a set of standards and requirements for an information security management system (ISMS). These standards represent best practices for information security management, enabling organizations that apply them to ensure security across a number of assets.

ISO 27001 focuses on ensuring three key aspects of data protection:

  1. Availability: Information is accessible to authorized users.
  2. Confidentiality: Only authorized users have access to the data.
  3. Integrity: Only authorized users can edit the information.

The SOC 2, or Service Organization Control 2, outlines organizational controls for five main service principles created by the American Institute of Certified Public Accountants (AICPA): security, availability, processing integrity, confidentiality, and privacy of customer data.

There are also two SOC 2 audits: Type 1 and Type 2.
SOC 2 Type 1: It evaluates an organization’s security program at a single point in time, providing a snapshot view of your current security posture.

SOC 2 Type 2:  It evaluates an organization’s security program over a longer period of time, usually six to 12 months. This audit is a valuable report because it provides a more comprehensive look at your security landscape.
The result of either SOC 2 audit is an attestation report confirming an organization meets SOC 2 standards.

Note: SOC 2 is not a certification; it is an attestation.

Understanding ISO 27001 certification

ISO 27001 is an internationally recognized standard developed by the International Organization for Standardization (ISO). It provides a systematic approach to managing and protecting the confidentiality, integrity, and availability of an organization’s information assets.

Key components of ISO 27001 certification

  1. Risk Assessment
    A comprehensive risk assessment is conducted to identify potential threats and vulnerabilities to the organization’s information assets.
  2. Information Security Management System (ISMS)
    An ISMS is established, implemented, and continually improved to manage and mitigate identified risks.
  3. Security Controls
    A set of security controls, based on the ISO 27002 code of practice, is implemented to address specific risks and ensure the confidentiality, integrity, and availability of information.
  4. Continuous Improvement
    The ISMS undergoes regular internal audits, management reviews, and corrective actions to ensure its effectiveness and alignment with changing business requirements.

Read our Heightened Regulatory Scrutiny: How to Meet Compliance Demands article to learn more!

TrustCloud
TrustCloud

Looking for automated, always-on IT control assurance?

TrustCloud keeps your compliance audit-ready so you never miss a beat.

Learn More

Understanding SOC 2 attestation

SOC 2 (Service Organization Control 2) is a widely recognized auditing standard developed by the American Institute of Certified Public Accountants (AICPA). It focuses on evaluating the design and operational effectiveness of an organization’s controls related to the security, availability, processing integrity, confidentiality, and privacy of customer data.

Key components of SOC 2 attestation

  1. Trust Services Criteria
    SOC 2 audits assess an organization’s controls against the AICPA’s Trust Services Criteria, which include security, availability, processing integrity, confidentiality, and privacy.
  2. Description of Services and Controls
    The organization provides a detailed description of its services, systems, and the controls implemented to meet the Trust Services Criteria.
  3. Independent Audit
    A qualified third-party auditor evaluates the design and operating effectiveness of the organization’s controls against the Trust Services Criteria.
  4. Audit Report
    The auditor issues a report detailing the scope, objectives, and findings of the audit, including any identified control deficiencies and the auditor’s opinion.

How does one choose between ISO 27001 and SOC 2?

Choosing a compliance standard depends on your requirements, resources, and goals.

When should I choose ISO 27001?

ISO 27001 is a good choice if you need to create an ISMS or have international clients. Because ISO 27001 is a universal standard around the globe, certification is recognized by all industries and regions.
ISO 27001 is also good for companies that want to implement a more rigorous assessment standard. While it requires more effort and investment, ISO 27001 certification can hold more weight for stakeholders and enhance the organization’s security credibility.

When should I choose SOC 2?

SOC 2 audits are great for organizations that already have an ISMS in place and just want to spot-check their current standards and policies. They are especially useful for organizations that want a customizable audit to target their assessments and surface key insights about their security systems and policies.
Consider using SOC 2 audits when you need a lighter-weight, cheaper assessment or if your business solely operates in North America.

When to choose both

ISO 27001 is a good certification to achieve in order to establish a fully compliant ISMS. This will lay the foundation for a robust security management system. From there, you can conduct regular SOC 2 audits to continuously improve standards and identify weak points that need addressing. Consider using both audits for a well-rounded security program that is compliant across borders.

ISO 27001 certification vs. SOC 2 attestation: what’s the difference?

SOC 2 and ISO 27001 both provide companies with strategic frameworks and standards to measure their security controls and systems against. But what’s the difference between SOC 2 vs. ISO 27001?

Let’s look at it by reviewing four key compliance aspects.

  1. Scope
    Both SOC 2 and ISO 27001 have security controls that involve processes, policies and technologies to safeguard sensitive information. A study suggests that the two frameworks share 96% of the same security controls. The difference is which of those security controls you implement.
    ISO 27001 focuses on the development and maintenance of an information security management system (ISMS). An ISMS provides a systematic approach for managing an organization’s information security.
    To achieve compliance, you must conduct a risk assessment, identify and implement security controls and regularly review their effectiveness.
    SOC 2, by contrast, is a lot more flexible. It comprises five Trust Services Criteria (TSC): Security, Availability, Processing Integrity, Confidentiality, and Privacy, but only the first of those is mandatory. Organizations can implement internal controls related to the other principles if they want, but it’s not necessary to achieve certification.
  2. Market applicability
    Both frameworks are recognized globally, but SOC 2 is more closely associated with North America. If you’re based in that region, you’ll find that both SOC 2 and ISO 27001 are common. Outside of North America, ISO 27001 is much more popular.
  3. Certification process
    You must complete an external audit to certify for either framework. The only difference in this process is who conducts the audit. A recognized ISO 27001-accredited certification body must complete ISO 27001 certification. In contrast, a SOC 2 attestation report can only be performed by a licensed CPA (Certified Public Accountant). There’s also a slight difference in what certification looks like. Organizations that pass the ISO 27001 audit receive a certificate of compliance, whereas SOC 2 compliance is documented with a formal attestation. SOC 2 is not a certification but an attestation.
  4. Project timeline
    The certification process is similar for ISO 27001 and SOC 2, with three stages you must complete.
    1. Conduct a gap analysis to determine which areas of the framework you’re already compliant with and where you need to make improvements. As part of this process, you should also define your security objectives and which areas of your organization will be covered.
    2. Identify which security controls are appropriate for your organization and take the necessary steps to implement them. This includes documenting your practices and establishing a method to review and improve your processes.
    3. The final step is the audit. Organizations often audit themselves before seeking accreditation so they can fix any mistakes they find.
      Once you’re confident in your compliance practices, you can contact a certification body and arrange an ISO 27001 or SOC 2 audit. The length of time this will take depends on the amount of work needed to meet the standards. It should take about two or three months to implement SOC 2 and three to six months to implement ISO 27001.

Read the “ISO 27001 vs. 27002 EXPLAINED by Top Security Experts” article to learn more!

What do ISO 27001 and SOC 2 have in common?

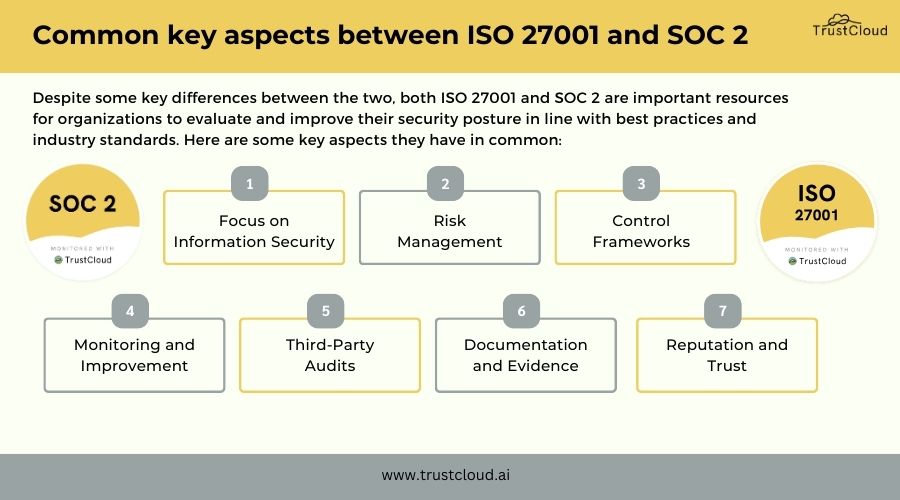
Despite some key differences between the two, both ISO 27001 and SOC 2 are important resources for organizations to evaluate and improve their security posture in line with best practices and industry standards. Completing certifications in one or both can reassure clients and investors that your systems are well-managed and your data is secure.

ISO 27001 and SOC 2 are widely recognized frameworks for ensuring information security within organizations. Despite their different origins and scopes, ISO 27001 being an international standard and SOC 2 being a U.S.-centric auditing procedure, they share several key aspects. Both frameworks emphasize robust risk management, the implementation of comprehensive security controls, and the importance of continuous monitoring and improvement.

They also require rigorous documentation and third-party audits to verify compliance. Achieving certification or attestation under these frameworks not only strengthens an organization’s security posture but also enhances its credibility and trustworthiness in handling sensitive data.
SOC 2 attestation

Here are some key aspects they have in common:

  1. Focus on Information Security
    Both ISO 27001 and SOC 2 are centered around ensuring that an organization’s information systems and data are secure. They provide guidelines and controls to help organizations protect against data breaches, unauthorized access, and other security threats.
  2. Risk Management
    Both frameworks emphasize the importance of risk management. Organizations are required to identify, assess, and mitigate risks to their information systems. This involves implementing controls to manage identified risks and regularly reviewing and updating those controls.
  3. Control Frameworks
    ISO 27001 and SOC 2 both require the implementation of a comprehensive set of controls to protect information. While ISO 27001 is more prescriptive with its Annex A controls, SOC 2 focuses on Trust Service Criteria (TSC) like security, availability, processing integrity, confidentiality, and privacy. Both frameworks allow organizations to tailor controls based on their specific needs.
  4. Continuous Monitoring and Improvement
    Both standards emphasize the need for ongoing monitoring and continuous improvement of information security practices. Organizations are expected to regularly review their security controls, audit their effectiveness, and make necessary adjustments to address new threats or vulnerabilities.
  5. Third-Party Audits
    To achieve compliance with ISO 27001 or SOC 2, organizations must undergo an independent audit. These audits assess whether the organization’s security controls and practices meet the requirements of the respective frameworks. Successful completion of the audit results in certification (for ISO 27001) or an attestation report (for SOC 2).
  6. Documentation and Evidence
    Both ISO 27001 and SOC 2 require comprehensive documentation of policies, procedures, and security controls. Organizations must also maintain evidence that these controls are being effectively implemented and adhered to, which is crucial for passing audits.
  7. Reputation and Trust
    Achieving compliance with either ISO 27001 or SOC 2 demonstrates a commitment to information security, which can enhance an organization’s reputation and build trust with customers, partners, and other stakeholders. Both certifications are often seen as a competitive advantage in industries where data security is critical.

Simplifying ISO 27001 and SOC 2 compliance

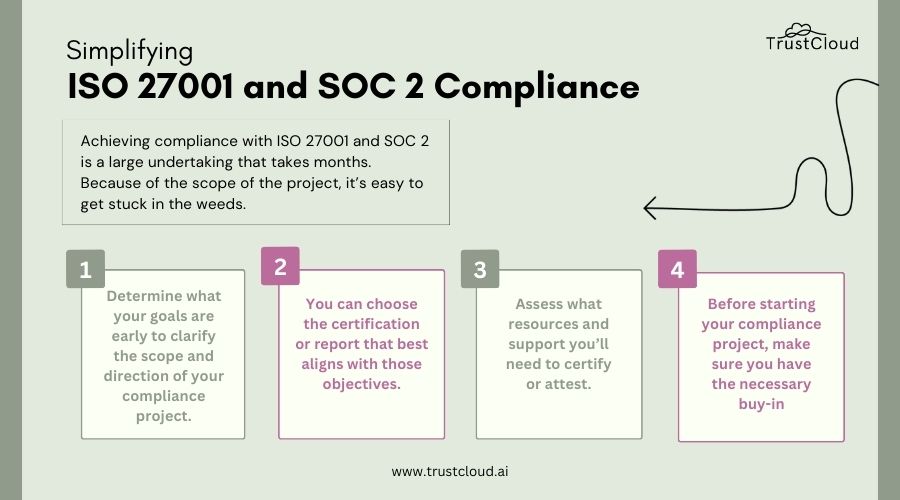
Achieving compliance with ISO 27001 and SOC 2 is a large undertaking that takes months. Because of the scope of the project, it’s easy to get stuck in the weeds.
ISO 27001 Certification vs. SOC 2 Attestation

Here are a few tips for streamlining the process so you can get the best results quicker:

  1. ‍Identify your goals early on
    What are you trying to achieve in your security organization? Do you have an information security management system in place? Different clients or industries may require specific standards and certifications. Determine what your goals are early to clarify the scope and direction of your compliance project.
  2. ‍Choose the right certification or report
    Once you have your goals in mind, you can choose the certification or report that best aligns with those objectives. For instance, if you don’t have an ISMS, ISO 27001 can help you create a compliant framework to build one. Or, if you’re considering an SOC 2 report, consider whether you want a Type 1 or Type 2 report based on the goals, scope, and timeline involved.
  3. Estimate the required resources
    Assess what resources and support you’ll need to get the job done. Both ISO 27001 and SOC 2 reports take months to complete. Do you have the staff, skills, technology, and leadership support you need? Identifying these resources ahead of time will make it easier to plan the project and prevent roadblocks along the way.
  4. ‍Get buy-in
    Securing buy-in from leadership and stakeholders is essential. Before starting your compliance project, make sure you have the necessary buy-in so you get the resources and support you need to complete it. Having the right support backing your project will streamline the entire process.

How do I obtain ISO 27001 and SOC 2 certifications?

ISO 27001 certification

To get ISO 27001 certification, an accredited registrar must audit your organization. In the U.S., auditors are typically affiliated with the ANSI National Accreditation Board.
The audit is divided into two stages:

  1. Stage 1: Documentation Assessment: This is an informal review of the current ISMS and existing documentation. During this stage, the auditor will assess whether the documentation meets ISO 27001 requirements and point out any gaps or areas to improve the management system.
  2. Stage 2: Certification Audit: This is the formal review. Once you’ve made any necessary changes that arose during Stage 1, the auditor will review your compliance with the ISO 27001 standard.

The certification process usually takes 6 to 12 months, depending on the size and complexity of your organization. Companies that get ISO 27001 certification demonstrate to consumers, clients, and investors that the organization has implemented best practices for protecting and securing its data.

SOC 2 Attestation

To demonstrate compliance with SOC 2 standards, you’ll need to complete an audit. In preparation for a SOC 2 audit, first decide on which type of audit you’ll be conducting: Type 1 or Type 2. Then, determine the scope of the audit, including which Trust Services Principles will be included, and document your policies.

Once your policies are in place, hire an external auditor through a licensed CPA firm to complete the review. The auditor will complete the following steps:

  1. Review the audit scope
  2. Develop a project plan
  3. Test security controls
  4. Document the results
  5. Deliver the report

This report will detail the evaluation of your security controls and issue an opinion on whether the organization adequately meets SOC 2 standards. This is called an attestation report (not to be confused with official certification). The report attests to the organization’s compliance and provides evidence for leaders and stakeholders of the organization’s adherence to best security practices.

Common ground between ISO 27001 and SOC 2

Both ISO 27001 and SOC 2 share a common mission: to safeguard information assets through structured, risk-based, and auditable practices. While their origins differ, their objectives align in ensuring data security, resilience, and trust.

Common key aspects between ISO 27001 and SOC 2

By aligning with either or both frameworks, companies demonstrate their commitment to responsible information management and global best practices in cybersecurity.

  1. Focus on Information Security
    Both ISO 27001 and SOC 2 place data security at the core. They outline structured guidelines and controls to defend against data breaches, unauthorized access, and misuse. Through these frameworks, organizations can establish a consistent security posture that minimizes exposure to internal and external threats.
  2. Risk Management
    Both frameworks emphasize a risk-based approach. Organizations must identify, evaluate, and mitigate potential vulnerabilities in their systems. Regular reviews of control effectiveness ensure that security measures evolve alongside emerging threats, helping businesses maintain resilience in a constantly changing cyber landscape.
  3. Control Frameworks
    ISO 27001 and SOC 2 both require robust control implementation. While ISO 27001 prescribes Annex A controls, SOC 2 is built on Trust Service Criteria like security, confidentiality, and availability. Both allow flexibility, enabling organizations to adopt tailored controls aligned with their business objectives and risk environment.
  4. Continuous Monitoring and Improvement
    Ongoing improvement is a shared principle of both frameworks. Businesses must continuously monitor controls, conduct internal audits, and adapt their strategies to address new vulnerabilities. This approach promotes a security culture where compliance is maintained dynamically rather than reactively.
  5. Third-Party Audits
    Independent audits validate compliance for both ISO 27001 and SOC 2. External auditors assess whether implemented controls meet framework requirements. Achieving ISO 27001 certification or SOC 2 attestation signals that an organization’s security practices have been thoroughly examined and verified by experts.
  6. Documentation and Evidence
    Detailed documentation underpins both frameworks. Organizations must maintain up-to-date records of policies, risk assessments, and control activities. This documentation provides tangible evidence of compliance, ensuring transparency during audits and supporting accountability across teams.
  7. Reputation and Trust
    Earning ISO 27001 or SOC 2 compliance reinforces an organization’s credibility and reliability. It assures clients and partners that data is managed responsibly. In highly regulated industries, such certifications can serve as competitive differentiators, helping businesses attract customers who value strong data protection practices.

ISO 27001 and SOC 2 share a unified purpose: building a trustworthy and secure digital ecosystem. Both encourage a proactive, risk-aware culture where security is embedded in every business decision. Organizations that embrace these frameworks not only achieve compliance but also establish themselves as leaders in data protection, transparency, and customer trust.

Simplifying ISO 27001 and SOC 2 compliance

Achieving compliance with ISO 27001 and SOC 2 is a large undertaking that takes months. Because of the scope of the project, it’s easy to get stuck in the weeds.

Simplifying ISO 27001 and SOC 2 Compliance

Here are a few tips for streamlining the process so you can get the best results quicker:

  1. ‍Identify your goals early on
    What are you trying to achieve in your security organization? Do you have an information security management system in place? Different clients or industries may require specific standards and certifications. Determine what your goals are early to clarify the scope and direction of your compliance project.
  2. ‍Choose the right certification or report
    Once you have your goals in mind, you can choose the certification or report that best aligns with those objectives. For instance, if you don’t have an ISMS, ISO 27001 can help you create a compliant framework to build one. Or, if you’re considering an SOC 2 report, consider whether you want a Type 1 or Type 2 report based on the goals, scope, and timeline involved.
  3. Estimate the required resources
    Assess what resources and support you’ll need to get the job done. Both ISO 27001 and SOC 2 reports take months to complete. Do you have the staff, skills, technology, and leadership support you need? Identifying these resources ahead of time will make it easier to plan the project and prevent roadblocks along the way.
  4. ‍Get buy-in
    Securing buy-in from leadership and stakeholders is essential. Before starting your compliance project, make sure you have the necessary buy-in so you get the resources and support you need to complete it. Having the right support backing your project will streamline the entire process.

Ready to breeze through your ISO 27001 audit?

A successful ISO 27001 audit shows customers and prospects that you’re serious about protecting their data. TrustCloud helps you achieve ISO 27001 certification faster, with less stress on each subsequent audit.


Schedule a Demo

How do I obtain ISO 27001 and SOC 2 certifications?

ISO 27001 certification

To get ISO 27001 certification, an accredited registrar must audit your organization. In the U.S., auditors are typically affiliated with the ANSI National Accreditation Board.
The audit is divided into two stages:

  1. Stage 1: Documentation Assessment: This is an informal review of the current ISMS and existing documentation. During this stage, the auditor will assess whether the documentation meets ISO 27001 requirements and point out any gaps or areas to improve the management system.
  2. Stage 2: Certification Audit: This is the formal review. Once you’ve made any necessary changes that arose during Stage 1, the auditor will review your compliance with the ISO 27001 standard.

The certification process usually takes 6 to 12 months, depending on the size and complexity of your organization. Companies that get ISO 27001 certification demonstrate to consumers, clients, and investors that the organization has implemented best practices for protecting and securing its data.

SOC 2 Attestation

To demonstrate compliance with SOC 2 standards, you’ll need to complete an audit. In preparation for a SOC 2 audit, first decide on which type of audit you’ll be conducting: Type 1 or Type 2. Then, determine the scope of the audit, including which Trust Services Principles will be included, and document your policies.
Once your policies are in place, hire an external auditor through a licensed CPA firm to complete the review. The auditor will complete the following steps:

  1. Review the audit scope
  2. Develop a project plan
  3. Test security controls
  4. Document the results
  5. Deliver the report

This report will detail the evaluation of your security controls and issue an opinion on whether the organization adequately meets SOC 2 standards. This is called an attestation report (not to be confused with official certification). The report attests to the organization’s compliance and provides evidence for leaders and stakeholders of the organization’s adherence to best security practices.

FAQs

Can ISO 27001 and SOC 2 work together?

Absolutely. ISO 27001 and SOC 2 have overlapping standards with complementary requirements. ISO 27001 can help organizations build out robust ISMS, while SOC 2 can fill in the gaps and ensure ongoing improvement and flexible assessments targeted at your unique security framework.

No. ISO 27001 is a universal set of standards with comprehensive requirements for an ISMS. SOC 2 is a lighter-weight audit, customizable to the needs and goals of the organization being assessed, and is primarily used in North America.

Having only ISO 27001 certification can put you at a competitive disadvantage when working with prospective partners and vendors that require SOC 2. By complying with both, you can expand your business reach while improving your security posture.

No. SOC 2 and ISO 27001 have significant overlap, but the two standards are distinct and serve different goals.

No, ISO 27001 compliance is not mandatory. However, it does ensure robust security management and can help your organization maintain regulatory compliance in other areas.

Yes. ISO 27001 helps organizations design and implement information security management systems that ensure stronger cybersecurity compliance.

Related articles

Prepare to pass your SOC 2 audit

Learn how TrustCloud helps you achieve SOC 2 attestation faster, with less stress on each subsequent audit.

SOC 2 Overview and Guides

A comprehensive introduction to the SOC 2 compliance readiness process, essential for SaaS vendors in the United States.

Have you checked out TrustTalks?

Your go-to podcast series by TrustCloud exploring the evolving landscape of security and GRC.
OR

TrustCommunity

Instant support with our AI chatbot

Please login with your TrustCloud credentials to continue