
On this page
ToggleZero-trust used to sound like a buzzword you’d only hear in vendor decks and security keynotes. Today, it’s the reality check for every team that’s tired of treating the corporate network like a magical safe zone. If users are logging in from everywhere, on every kind of device, and your most critical apps live in the cloud, then identity has quietly become your new perimeter. And that’s exactly where the “MFA vs. SSO” debate shows up: do you double down on stronger authentication or make access simpler and more centralized?
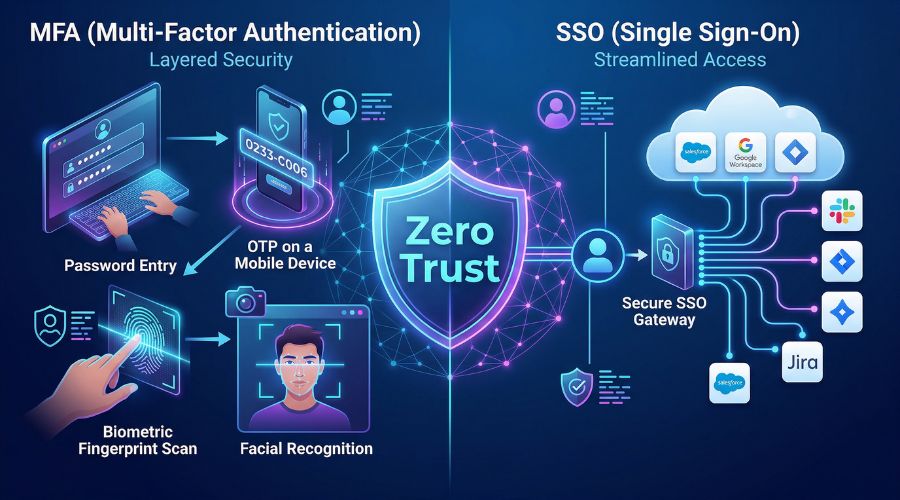
On the surface, multi-factor authentication (MFA) and single sign-on (SSO) look like very different answers to the same problem. MFA piles on extra proof to make sure the person logging in really is who they claim to be. SSO tries to simplify the chaos by giving people one secure doorway to all their apps. One feels like friction, the other like relief. However, when viewed through a zero trust lens, it becomes clear that they are not competitors; rather, they are two integral components of the same identity narrative.
This article breaks down what MFA and SSO actually do, where each one shines, and how they fit into a modern zero-trust strategy. Instead of treating them as a binary choice, we’ll look at practical scenarios: when to prioritize MFA for quick risk reduction, when SSO becomes critical for control and visibility, and how the combination of both lets you “never trust, always verify” without making your users miserable.
Most teams don’t actually need to choose between MFA and SSO for zero-trust; they need to decide which one comes first, where each fits, and how tightly they work together.
What is a zero-trust strategy?
A zero-trust strategy is a modern cybersecurity approach built on the principle of “never trust, always verify,” meaning every user, device, and application must continuously prove they are legitimate before accessing any resource. It assumes that threats can come from both inside and outside the network, so no connection or request is automatically trusted based on location, network, or past approvals. Instead, access is granted using strict identity verification, device health checks, contextual signals (like user role, location, and behavior), and the least-privilege principle to limit what each entity can do.
By segmenting networks and tightly controlling access paths, zero trust minimizes the damage an attacker can cause if they compromise an account or system. Overall, this strategy helps organizations strengthen security in cloud, hybrid, and remote-work environments where traditional perimeter-based defenses are no longer sufficient.
Why this MFA vs. SSO debate matters for zero-trust
The success of zero-trust hinges on a fundamental principle: never trust, always verify.
In that world, MFA and SSO are key tools for protecting your new identity perimeter. MFA raises the bar for attackers by adding extra verification steps beyond a password.
SSO centralizes sign-in and enforces consistent policies across apps, while dramatically reducing password fatigue.
Zero trust expects you to use strong, continuous identity checks, not one-and-done logins.
Think of MFA as the seatbelt and SSO as the steering wheel: one keeps you safe in a crash, and the other helps you stay in control every day. You need both to actually drive your zero trust strategy forward.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MoreGetting clear on what MFA really does (and doesn’t do)
Multi-factor authentication is simple: it requires users to prove “something they know, something they have, or something they are” before granting access.
Common factors include:
- Password or PIN (knowledge)
- OTP app, SMS code, hardware token, security key (possession)
- Biometric like fingerprint or face ID (inheritance)
Why MFA is a zero-trust essential
MFA matters for zero trust because it makes stolen passwords far less useful.
If an attacker phishes a user’s credentials, they still need to bypass that second factor to get in.
A few concrete benefits:
- It blocks the vast majority of basic account takeover attempts and credential stuffing.
- It supports “assume breach” thinking: even if credentials leak, access is not automatically granted.
- It feeds your identity system with stronger assurance signals about who is actually logging in.
For high-risk systems, admin consoles, finance platforms, and customer data, MFA is non-negotiable in a modern environment.
Where MFA can fall short on its own
MFA isn’t magic, and zero trust recognizes its limitations.
MFA can be weakened by:
- MFA fatigue attacks are where users get spammed with prompts and eventually approve.
- SIM swapping or OTP interception when weaker factors are used (like SMS).
- The rollout design is poor because MFA is enabled only for a few crown jewels and not for everyday tools.
- Zero-trust guidance increasingly emphasizes phishing-resistant MFA (like FIDO2 security keys or platform authenticators) for sensitive environments.
So MFA is necessary, but on its own, it doesn’t organize your identity landscape or user experience. That’s where SSO comes in.
What SSO really brings to a zero trust architecture
Single sign-on lets users authenticate once and then access multiple applications without logging into each one separately.
Done well, SSO does much more than convenience:
- It puts an identity provider (IdP) like Microsoft Entra ID in front of every access request.
- It centralizes your access policies in one control plane instead of scattering them across dozens of apps.
- It reduces password sprawl, so users aren’t reusing weak passwords everywhere.
In a zero trust model, this centralization is powerful.
Your IdP becomes the gate through which all access must pass so you can consistently apply conditional access, device checks, risk scoring, and MFA prompts.
Why SSO is sometimes seen as “anti–zero trust”
If you view zero trust as “no long-lived sessions, constant prompts, no trust relationships,” SSO can seem like the opposite: one trusted session, many apps.
That criticism is fair when SSO is deployed like this: Static sessions that last all day.
- Static sessions that last all day.
- No rechecks when the risk changes.
- There is no conditional access or step-up MFA for sensitive actions.
But in a modern zero-trust implementation, SSO doesn’t mean “log in once and forget”; it means “centralize login so you can continuously evaluate trust.”
What SSO actually enables for zero-trust
When SSO is integrated into your identity-first strategy, you can:
- Apply dynamic policies based on user, device, location, and behavior.
- Enforce least privilege access through role-based access control (RBAC).
- Trigger step-up MFA for high-risk sessions or sensitive actions.
- Gain a single audit trail of user access to apps and data.
That combination, SSO for central control plus MFA for strong verification, is exactly what most zero trust reference architectures recommend as the starting point.
MFA vs. SSO: How they really compare for zero trust
Here’s how MFA and SSO stack up when you look at them through a zero trust lens instead of in isolation.
Identity capabilities compared
| Aspect | MFA’s role in zero trust | SSO’s role in zero trust |
| Primary purpose | Strengthen identity verification at sign-in. | Centralize authentication and policy enforcement. |
| Main benefit | Reduces impact of stolen passwords. | Reduces password sprawl, improves UX and governance. |
| Risk coverage | Credential theft, account takeover. | Shadow IT, inconsistent policies, weak app-level controls. |
| Zero trust alignment | Supports “never trust credentials alone.” | Enables continuous evaluation and centralized control. |
| Operational impact | Adds friction if overused or poorly designed. | Cuts login fatigue, reduces IT support tickets. |
| Where it’s strongest | High-risk accounts, privileged access, external users. | Medium- to large-sized orgs with many SaaS apps and remote work. |
| Where it struggles alone | Not helpful if users bypass or approve blindly. | Dangerous if used without MFA or risk checks. |
You don’t choose one for zero trust; you decide how to use both without exhausting your users or your security team.
Read the “Stay ahead with powerful insights on cybersecurity risks in 2026” article to learn more!
How SSO and MFA work together in a zero-trust IAM stack
In a mature zero trust identity architecture, SSO and MFA are part of one flow, not competing tools.
A typical pattern looks like this:
- A user goes to an application.
- The app redirects to your IdP for SSO.
- The IdP evaluates the request: user, device, location, risk.
- If the risk is low and a recent, strong session exists, access may continue without prompting.
- If risk is elevated or the app is sensitive, the IdP enforces MFA (step-up).
- Authorization is then applied using RBAC and policy rules.
This SSO + MFA model supports zero trust principles:
- Continuous verification of each request.
- Least privilege access based on roles and context.
- Assume a breach by not trusting a password or a network location alone.
Many modern guides explicitly advise starting your zero trust journey with identity: centralize SSO, enforce MFA, and then layer in device trust, segmentation, and monitoring.
Which should you prioritize first for your zero trust strategy?
The real question isn’t “MFA vs. SSO”; it’s “Given our current maturity, which move, MFA everywhere or SSO consolidation, reduces risk fastest without breaking the business?”
Here are some practical patterns based on where you are today.
If you’re early in your journey and still rely mostly on passwords
Signs you’re here:
- Users log in separately to each SaaS tool.
- Many apps have local accounts.
- MFA is inconsistent or limited to a few systems.
Zero trust–aligned move:
- Roll out broad, user-friendly MFA on your most critical systems first, then expand.
- In parallel, start consolidating into a central IdP for your top SaaS apps to prepare for SSO.
Why: MFA gives you an immediate uplift against credential attacks, while identity consolidation sets you up for SSO and better policy control.
If you already have basic MFA but fragmented identity
Signs you’re here:
- VPN, email, and a few apps have MFA.
- Users still juggle multiple passwords across tools.
You have limited visibility into app access and logs.
- Zero trust–aligned move:
- Invest in SSO to bring more apps behind your IdP.
- Enforce conditional access and step-up MFA from that central layer.
Why: You’ve raised the bar with MFA, but attackers can still exploit inconsistencies and shadow identity stores. SSO under a strong IdP closes those gaps.
If you already have SSO but limited MFA
Signs you’re here:
- Users enjoy seamless SSO into many apps.
- MFA is applied only for VPN or when off-network.
- You’re worried that if an account is compromised, the attacker gets “keys to the kingdom.”
Zero trust–aligned move:
- Make strong MFA mandatory at SSO login and for privileged actions.
- Move toward phishing-resistant factors for admins and high-risk roles.
Why: SSO without MFA makes your IdP a single point of failure. Adding robust MFA aligns that convenience with zero trust expectations.
Designing MFA and SSO so they don’t burn people out
Zero trust can easily fail in practice if users feel punished by security controls. Human-friendly design is a core part of making MFA and SSO sustainable.
Make MFA feel natural, not exhausting
A few practical tactics:
- Favor low-friction, strong factors like push notifications or platform authenticators instead of only SMS codes.
- Use risk-based policies so low-risk, compliant devices don’t get challenged constantly, while unusual locations or devices always do.
- Implement clear, simple messaging in prompts so users understand what they are approving.
For high-risk roles or sensitive apps, you can layer stronger factors, like security keys, without imposing them on every user.
Use SSO to give time back to your users
SSO is an easy place to win hearts and minds.
Done well, SSO should:
- Remove the need to remember dozens of passwords.
- Reduce login prompts throughout the day while still honoring risk and policy.
- Provide a single, consistent sign-in experience across web, mobile, and desktop apps.
The more usable SSO feels, the easier it is to get buy-in for stricter MFA and conditional access controls layered on top.
A simple blueprint to align MFA and SSO with zero-trust
If you need a practical, phased approach, this high-level blueprint reflects current best practices.
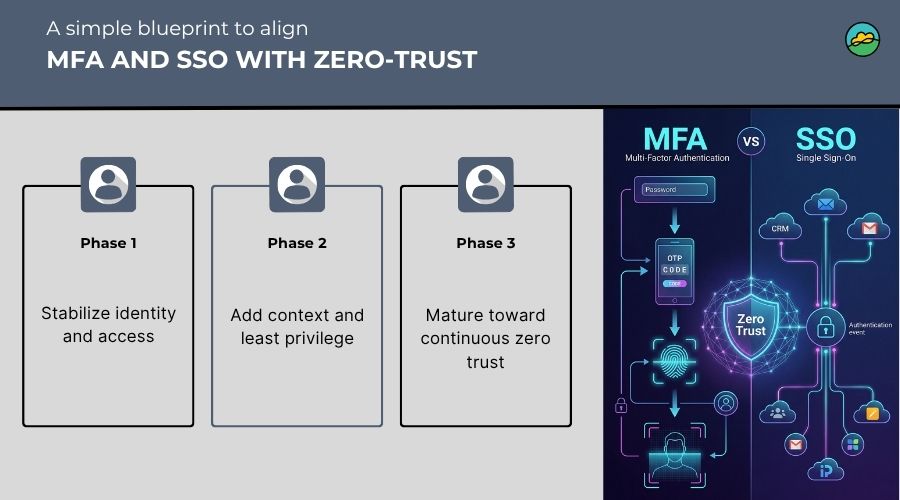
Phase 1: Stabilize identity and access
- Pick a primary IdP and route as many apps as possible through it for SSO.
- Enable MFA for all users, at least for remote and cloud access.
- Identify your most sensitive apps and enforce stricter MFA, including for on-prem access.
Goal: Stop credential-based attacks from being trivial and get your access decisions into one place.
Phase 2: Add context and least privilege
- Implement conditional access policies that look at device posture, location, and risk signals.
- Introduce step-up MFA for sensitive actions and admin operations, not just initial logins.
- Align access with roles and just-in-time elevation to support least privilege.
Goal: move from static “MFA at login” to dynamic, risk-aware decisions across the session lifecycle.
Phase 3: Mature toward continuous zero trust
- Strengthen MFA with phishing-resistant methods for high-value targets and workloads.
- Expand SSO coverage to long-tail apps and legacy systems where feasible.
- Integrate identity logs into your detection and response workflows for continuous monitoring.
Goal: treat identity as a living signal, constantly evaluated, correlated, and used to respond quickly when something looks off.
So, which identity solution best supports your zero trust strategy?
If you’re forced to pick one to start with in a low-maturity environment, MFA usually delivers the fastest, most visible risk reduction against the attacks you’re most likely to face.
But as your zero trust program matures, SSO becomes just as important because it gives you a central brain for access decisions, to actually apply that “never trust, always verify” principle consistently.
The most resilient organizations don’t treat MFA and SSO as an either/or choice:
- They treat MFA as a default expectation for any meaningful access.
- They treat SSO as the standard path for reaching apps and data.
- They design policies so that security and usability reinforce each other instead of fighting for attention.
If your goal is a practical, human-centered zero trust strategy, not just a slide deck, then the “best” identity solution is the one where MFA and SSO work together, guided by clear policies, strong identity governance, and a realistic understanding of how your people actually work.
Summing it up
If you zoom out from the tooling and acronyms, zero trust is really about one thing: stop handing out blanket trust and start earning it, one request at a time. MFA and SSO just happen to be two of the most visible places where your people feel that shift. MFA makes sure a leaked password isn’t enough to walk through the front door; SSO makes sure there actually is a front door, instead of a maze of half-forgotten logins and shadow accounts.
On their own, each has blind spots. MFA without SSO can turn into a patchwork of prompts that frustrate users and still leave gaps you can’t see. SSO without MFA can quietly become a “single point of failure” if one account is compromised. Together, though, they give you something much better: a single, consistent way to control access, plus a stronger way to prove who’s on the other side of the screen.
For most organisations, the smartest move isn’t to pick a winner in “MFA vs. SSO,” but to be honest about where you are today and choose the next step that reduces the most risk without breaking how people work. That might mean turning on MFA everywhere first, or it might mean pulling more apps behind SSO so you can finally see and shape access in one place. Over time, as you tighten policies, add context, and mature your identity stack, the question changes from “Which one should we choose?” to “How do we use both to keep verifying without ever getting in our own way?”
FAQs
What is the main difference between MFA and SSO in a zero-trust strategy?
The main difference between multi-factor authentication (MFA) and single sign-on (SSO) in a zero-trust strategy lies in their primary goals: MFA focuses on strengthening security, while SSO focuses on simplifying and centralizing access. MFA requires users to present two or more independent verification factors, such as a password, a one-time code, or a biometric check, before granting access, which significantly reduces the risk of account takeover if passwords are stolen or phished.
SSO, on the other hand, allows users to authenticate once through an identity provider and then access multiple applications without repeatedly logging in, which cuts down on login fatigue and encourages better password hygiene because users are managing fewer credentials. In a zero-trust model, the most effective approach is to pair SSO with MFA so that you get both strong identity verification and a streamlined user experience, instead of treating them as competing solutions.
Is MFA or SSO more important for supporting a zero-trust architecture?
Neither MFA nor SSO alone is “more important” for zero trust; they play complementary roles, and together they align closely with the principles of “never trust, always verify” and least-privilege access. MFA is critical because it ensures that every access request is backed by strong identity verification, making it much harder for attackers to use stolen passwords to move laterally across systems. This is essential in zero trust, where every request is treated as potentially hostile, even from inside the network.
SSO becomes important when you scale this model across many apps, users, and environments; it centralizes authentication, reduces the number of separate logins, and gives security teams a single control point to enforce consistent policies, logging, and conditional access. A zero-trust architecture is far more effective when SSO is used as the centralized access broker and MFA is enforced at critical decision points, such as high-risk logins, sensitive apps, and step-up authentication scenarios.
Should organizations use MFA and SSO together, and what are the benefits of combining them?
Yes, most organizations should use MFA and SSO together because the combination offers a strong balance of security, usability, and centralized control that aligns well with zero-trust principles. When you integrate MFA into your SSO platform, users authenticate once with strong, multi-factor checks and then gain access to approved applications through secure tokens, rather than repeatedly entering passwords. This reduces login fatigue and helpdesk tickets related to passwords while still enforcing robust identity verification at the front door. From a security perspective, SSO centralizes authentication events, making it easier to monitor access patterns, apply adaptive or conditional access policies, and quickly revoke access across many apps if an account is compromised.
At the same time, MFA adds an extra layer so that even if SSO credentials are stolen, attackers still face a strong barrier to entry. In a mature zero-trust implementation, this combination allows you to continuously verify identities, minimize password risks, and deliver a smoother user experience that encourages adoption rather than resistance.