

On this page
ToggleSecurity ratings were supposed to simplify third-party risk management.
That was the promise.
A single score could supposedly tell organizations whether a vendor was secure, risky, compliant, or vulnerable. Procurement teams could make faster decisions. Security teams could monitor thousands of vendors at scale. Executives could gain instant visibility into supply chain risk.
What are security ratings in third-party risk management?
Security ratings (also called “cybersecurity ratings” or “security scores”) are data-driven, objective measurements of an organization’s cybersecurity posture, assessed continuously from the outside in, without requiring access to the organization’s internal systems.
Think of them as a credit score for cybersecurity. Just as a credit score summarizes financial trustworthiness using observable data, a security rating summarizes how secure an organization’s external-facing environment appears based on signals that are publicly observable on the internet.
For organizations drowning in vendor sprawl, the idea sounded almost perfect.
And to be fair, security ratings platforms do solve a real problem. Modern businesses rely on an enormous network of third parties, cloud providers, software vendors, contractors, data processors, managed service providers, and supply chain partners. Monitoring all of them manually is practically impossible.
Security ratings emerged as a way to bring automation and scalability into that process.
But over time, many organizations discovered a hard truth: security ratings are far from perfect.
In fact, when used incorrectly, they can create a dangerous false sense of confidence.
Some companies treat ratings as definitive measures of security maturity. Others reject them entirely after dealing with inaccurate findings or misleading risk signals. The reality sits somewhere in the middle.
Security ratings are neither useless nor fully reliable.
They are directional indicators, helpful when interpreted carefully and risky when treated as absolute truth.
The organizations getting the most value from security ratings today are not the ones blindly trusting the scores. They are the ones using ratings as one input within a much broader risk strategy.
Because the biggest risk with security ratings is not that they exist.
It’s assuming they tell the full story.

Ready to move beyond spreadsheets and static assessments?
See how TrustCloud helps you automate, scale, and modernize third-party risk management.
Learn MoreWhy security ratings became so popular in the first place
The rise of security ratings makes complete sense when you look at the scale of modern third-party risk.
Most organizations now work with hundreds or even thousands of external vendors. Some large enterprises rely on tens of thousands of suppliers across software, infrastructure, logistics, finance, legal services, and cloud ecosystems.
Every vendor introduces potential exposure.
A weak security posture at one supplier can create downstream consequences across the entire business. And recent years have shown exactly how devastating supply chain incidents can become.
Security teams needed a way to monitor vendor risk continuously without manually auditing every organization.
That’s where security ratings platforms stepped in.
Using externally observable signals, such as exposed services, SSL configurations, patching behavior, DNS records, leaked credentials, and network hygiene, these platforms generate risk scores intended to estimate an organization’s cybersecurity posture.
The appeal was obvious:
- Faster vendor assessments
- Continuous monitoring
- Scalable visibility
- Simplified reporting
- Easier prioritization
Instead of relying solely on questionnaires or annual assessments, organizations could now track changes dynamically.
For many teams, especially those with limited resources, security ratings became an attractive shortcut.
But shortcuts in cybersecurity rarely come without tradeoffs.
A security score cannot capture the full reality of risk
One of the biggest misconceptions about security ratings is the belief that a score accurately reflects overall cybersecurity maturity.
It does not.
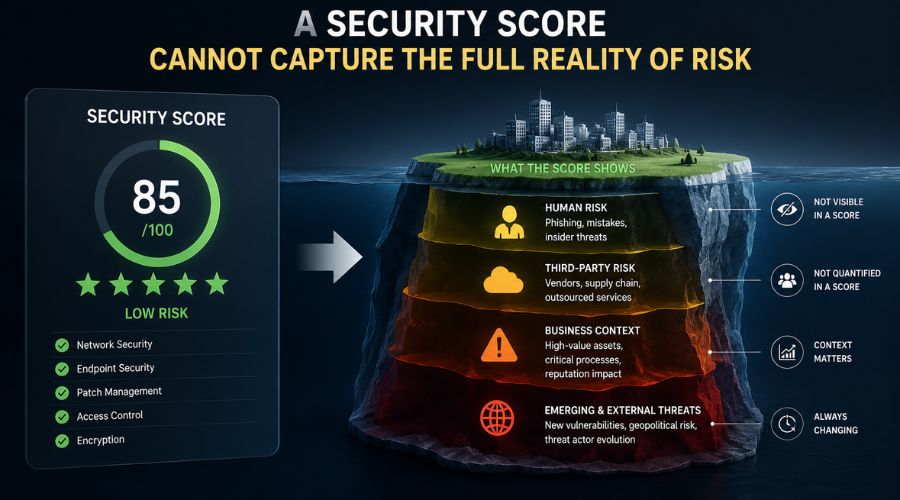
Security ratings platforms only see what is externally observable. That means they are inherently limited in scope.
A company might receive a strong rating while still struggling with:
- Weak internal access controls
- Poor employee security training
- Insider threats
- Unpatched internal systems
- Inadequate incident response processes
- Weak governance practices
- Poor security culture
At the same time, an organization with a lower score may actually maintain mature internal security operations but have minor external configuration issues triggering rating penalties.
This creates a disconnect between perceived risk and actual risk.
Security posture is far more nuanced than any single number can represent.
Cybersecurity maturity depends on people, processes, architecture, governance, resilience, detection capabilities, recovery planning, and organizational behavior, much of which remains invisible to external scanners.
A score can highlight potential indicators.
It cannot fully measure operational resilience.
False positives are frustrating, but false confidence is worse
One of the most common complaints about security ratings is inaccurate findings.
Security teams often discover outdated vulnerabilities, incorrect asset attribution, or misidentified infrastructure affecting their scores. Vendors may spend weeks disputing issues that were never actually relevant to their environment.
This creates understandable frustration.
But ironically, false positives are not the biggest danger.
False confidence is.
A vendor with an excellent security rating can still experience a major breach. A high score does not guarantee strong internal controls, secure development practices, or effective incident response.
Some organizations fall into the trap of treating ratings as vendor approval systems:
- High score equals low risk
- Low score equals high risk
That oversimplification creates blind spots.
Threat actors do not care about rating categories.
Attackers target real-world weaknesses that often exist beyond what ratings platforms can measure.
The danger emerges when organizations stop asking deeper questions because a vendor appears “green” on a dashboard.
That is when security ratings become risky.
Read the “Ultimate third-party risk management playbook: Shield your business in the digital era” article to learn more!
Vendors are learning how to optimize for ratings instead of resilience
Another growing issue is the rise of “security score optimization.”
As ratings become more influential in procurement and partnership decisions, vendors naturally start managing toward the score itself.
That sounds reasonable on the surface. But it can create unintended consequences.
Organizations may prioritize fixing externally visible issues that improve ratings while neglecting deeper operational weaknesses that are harder to measure.
In other words, companies can begin optimizing for appearance rather than resilience.
This is not unique to cybersecurity. Any scoring system eventually influences behavior.
The problem is that attackers are not evaluating companies using vendor scorecards. They are searching for exploitable weaknesses wherever they exist.
A vendor may improve its external rating while still maintaining:
- Weak identity governance
- Poor detection capabilities
- Inadequate segmentation
- Fragile backup systems
- Immature incident response processes
The score improves.
The actual resilience may not.
This creates a dangerous illusion of progress.
Agentic, Data-Driven Third-Party Cyber Assessments
Continuously assess vendor risk by analyzing outside-in security signals and security posture artifacts, so your team can identify gaps and complete risk assessments with greater confidence at a fraction of the effort.
Context matters far more than the number itself
One of the biggest mistakes organizations make is comparing security ratings without considering business context.
Not all vendors carry the same level of risk.
A payroll provider handling sensitive employee data should not be evaluated the same way as a low-risk marketing contractor. Likewise, a cloud infrastructure provider supporting critical operations requires far deeper scrutiny than a vendor with limited system access.
The same security rating can represent very different levels of actual exposure depending on:
- Data sensitivity
- System access
- Business criticality
- Regulatory obligations
- Operational dependencies
- Network connectivity
- Geographic exposure
Yet many organizations reduce vendor risk management into simplified scoring thresholds.
That approach misses the complexity of real-world relationships.
Security ratings become more useful when organizations evaluate them alongside broader contextual intelligence.
The score itself matters far less than understanding:
- Why the score changed
- Which assets are affected
- How the issues relate to business operations
- Whether compensating controls exist
- How quickly the vendor responds to problems
Without context, ratings can easily become misleading.
Cybersecurity maturity cannot be measured from the outside alone
Imagine trying to judge the safety of a hospital by walking around the parking lot.
You might observe a few useful indicators:
- Are the doors secured?
- Is the building maintained?
- Are emergency systems visible?
- Does the environment appear organized?
- But you still would not know:
- How skilled the medical staff is
- Whether surgical procedures are safe
- How emergency protocols work
- Whether patient data is protected
- How incidents are handled internally
That is essentially the limitation of security ratings.
They observe external signals.
Those signals can absolutely reveal meaningful risk indicators. Poor patching hygiene, exposed databases, weak configurations, and leaked credentials often correlate with broader security weaknesses.
But they still represent only a partial view.
The deeper aspects of cybersecurity maturity remain internal:
- Governance structures
- Security culture
- Leadership engagement
- Detection engineering
- Recovery capabilities
- Crisis management readiness
- Employee awareness
- Access governance
These elements are incredibly important during real-world incidents, yet largely invisible to ratings platforms.
That is why organizations should treat ratings as signals, not verdicts.
Read the “Who is a third-party vendor, a subprocessor, and a third-party supplier?” article to learn more!
The smartest organizations use ratings as conversation starters
The most mature security teams rarely use ratings as standalone decision-making tools.
Instead, they use them as investigative triggers.
A declining score may prompt deeper discussions with a vendor. A sudden configuration issue may initiate additional validation. An unusual exposure pattern may lead to enhanced monitoring or follow-up assessments.
In other words, ratings become starting points rather than final answers.
This approach creates a healthier risk management process.
Rather than blindly trusting or completely dismissing ratings, organizations combine them with:
- Security questionnaires
- Evidence reviews
- Compliance attestations
- Penetration testing results
- Audit findings
- Incident history
- Threat intelligence
- Vendor responsiveness
- Internal business context
The goal is not to eliminate uncertainty completely.
That is impossible in cybersecurity.
The goal is building a more complete and balanced understanding of risk.
Ratings can still provide enormous operational value
Despite their flaws, security ratings still offer meaningful benefits when used properly.
One major advantage is scalability.
Most organizations simply do not have the resources to perform deep security reviews on every vendor continuously. Ratings help prioritize attention toward vendors showing signs of elevated exposure or deteriorating hygiene.
They also improve visibility.
Many companies lack basic awareness of externally exposed assets, forgotten domains, misconfigured services, or leaked credentials across their vendor ecosystem. Ratings platforms can surface issues that might otherwise remain unnoticed.
Continuous monitoring is another valuable capability.
Traditional third-party assessments often happen annually, which leaves long visibility gaps between reviews. Security ratings provide ongoing observation that can help identify changes more quickly.
For procurement and executive reporting, ratings also offer simplified ways to communicate risk trends at scale.
The key is recognizing what ratings can and cannot do.
They can support prioritization.
They can support visibility.
They can support monitoring.
But they should never replace deeper due diligence or risk analysis.
Read the “Zero trust is not a product: The architecture mistake most security teams make” article to learn more!
Security ratings become dangerous when leadership oversimplifies them
The pressure for simplified metrics is understandable.
Executives and boards want concise ways to measure cybersecurity exposure across complex vendor ecosystems. A numeric score feels easy to understand and easy to report.
But oversimplification creates risk.
When leadership treats security ratings as definitive indicators of vendor safety, organizations may unintentionally reduce cybersecurity into a compliance exercise.
That mindset can distort priorities.
Security teams may focus excessively on score improvement rather than resilience improvement.
Vendors may become reluctant to disclose incidents or operational weaknesses if they fear rating penalties. Procurement teams may reject vendors based solely on ratings without understanding the underlying context.
Over time, this can weaken the quality of risk conversations.
Cybersecurity is not a credit score.
It is a constantly evolving operational challenge shaped by people, technology, processes, and unpredictable threat behavior.
Reducing that complexity into a single number creates an illusion of certainty that simply does not exist.
Supply chain attacks are exposing the limits of ratings
Recent supply chain incidents have highlighted the limitations of external security scoring models.
Several organizations that suffered major breaches or downstream compromise maintained relatively strong external ratings before the incidents occurred.
Why?
Because many serious attack paths originate through weaknesses that external scanning cannot fully observe:
- Compromised credentials
- Insider threats
- Social engineering
- Weak access governance
- Software development vulnerabilities
- Identity provider compromise
- Third-party trust relationships
Security ratings may capture indicators related to exposure, but they often cannot predict how attackers will exploit complex human and operational weaknesses inside organizations.
This does not make ratings useless.
It simply reinforces the importance of layered risk assessment strategies.
Organizations need multiple sources of intelligence working together.
How to use security ratings without getting burned
The safest and smartest way to use security ratings is to treat them as one layer within a broader vendor risk framework.
That means:
- Never relying solely on the score
- Prioritizing context over rankings
- Validating findings carefully
- Combining ratings with internal assessments
- Monitoring trends instead of isolated snapshots
- Using ratings to guide conversations, not replace them
It also means understanding that cybersecurity risk is dynamic.
A vendor’s posture can change rapidly. New vulnerabilities emerge constantly. Business relationships evolve. Threat actors adapt quickly.
Static assumptions create dangerous blind spots.
Organizations should also focus heavily on vendor transparency and responsiveness.
A vendor willing to engage openly about findings, explain mitigations, and improve security posture collaboratively often presents lower long-term risk than one with a superficially strong score but poor communication practices.
Trust, maturity, and operational behavior matter enormously.
Read the “Boost trust with 10 powerful strategies to remediate third-party vendor risks” article to learn more!
The future of third-party risk needs more nuance, not less
As digital ecosystems continue expanding, organizations will rely even more heavily on automated risk monitoring.
Security ratings will likely remain an important part of that future.
But the industry is gradually recognizing that meaningful third-party risk management requires far more nuance than simple numeric rankings.
The organizations building mature programs today are shifting toward:
- Contextual risk intelligence
- Continuous validation
- Integrated business impact analysis
- Threat-informed assessments
- Collaborative vendor engagement
- Operational resilience measurement
In that model, security ratings still have value.
They simply stop pretending to be complete representations of cybersecurity reality.
And that shift matters.
Because the real goal of vendor risk management is not producing attractive dashboards.
It is understanding where meaningful exposure exists before incidents occur.
Security ratings are useful, just not in the way many companies think
Security ratings are not broken because they have limitations.
Every measurement system has limitations.
The real problem emerges when organizations misunderstand what the ratings actually represent.
A security score is not proof of safety.
It is not proof of resilience.
And it is certainly not proof that a vendor will avoid future incidents.
What ratings can provide is directional insight, an additional layer of visibility that helps organizations identify patterns, prioritize attention, and ask smarter questions.
That is still incredibly valuable.
But only when organizations resist the temptation to oversimplify cybersecurity into a single number.
Because in the real world, risk is rarely that simple.
And the companies that understand that nuance will be far less likely to get burned.
FAQs
Why are security ratings considered flawed by many organizations?
Security ratings are considered flawed because they only provide a limited external view of an organization’s cybersecurity posture. Most rating platforms rely on publicly observable signals such as exposed services, patching behavior, DNS records, SSL configurations, and leaked credentials. While these indicators can reveal useful information, they do not capture the full reality of an organization’s internal security operations.
For example, a company may have a strong external security rating while still struggling with weak access controls, poor employee awareness training, immature incident response processes, or insider threat risks. On the other hand, an organization with a lower score may actually maintain strong internal security practices but receive penalties for relatively minor configuration issues.
Another major issue is false positives. Vendors often report inaccurate findings, outdated vulnerabilities, or infrastructure incorrectly associated with their environments. This can create frustration and confusion during vendor assessments.
The biggest concern, however, is false confidence. Some organizations mistakenly treat security ratings as definitive proof of security maturity instead of using them as one piece of a larger risk assessment process. Cybersecurity is far too complex to be fully represented by a single number, which is why mature organizations use security ratings carefully and in context.
How should organizations use security ratings effectively?
Organizations should use security ratings as supporting tools rather than standalone decision-making systems. The most effective approach is to treat ratings as directional indicators that help identify potential areas of concern, not as final judgments about a vendor’s overall security posture.
A strong security rating should not automatically mean a vendor is low risk, and a weaker score should not immediately disqualify a business partner. Instead, organizations should investigate why a score changed, what findings contributed to it, and whether those issues actually create meaningful business exposure.
Security ratings work best when combined with broader risk management activities such as security questionnaires, audit reviews, penetration testing, compliance certifications, threat intelligence, and direct conversations with vendors. They are especially valuable for continuous monitoring because they can help organizations detect changes in external security hygiene more quickly than annual assessments alone.
Context is also critical. Different vendors create different levels of risk depending on their access to systems, data sensitivity, and operational importance. Mature security programs understand that vendor risk cannot be reduced to simple rankings or color-coded dashboards. The goal is to build a complete understanding of exposure by combining multiple sources of intelligence together.
Can a vendor with a high security rating still experience a breach?
Yes, absolutely. A high security rating does not guarantee that a vendor is protected from cyberattacks or immune to breaches. Security ratings mainly evaluate externally visible indicators, but many serious cyber incidents originate from internal weaknesses that external scanning tools cannot fully detect.
For example, attackers may exploit compromised employee credentials, social engineering attacks, insider threats, weak identity governance, software development flaws, or poorly managed access permissions. These types of operational and human-related risks are often invisible to security ratings platforms.
A vendor may also optimize specifically for improving its external score without investing equally in deeper security resilience. This means an organization could appear secure on paper while still lacking strong incident response capabilities, detection systems, backup strategies, or internal governance processes.
Recent supply chain attacks have demonstrated that even companies with relatively strong security ratings can still become victims of major breaches. This is why organizations should never rely solely on ratings when evaluating vendor risk. Security ratings are useful for monitoring trends and identifying potential concerns, but they should always be supported by deeper assessments, ongoing collaboration, and continuous risk evaluation practices.