
On this page
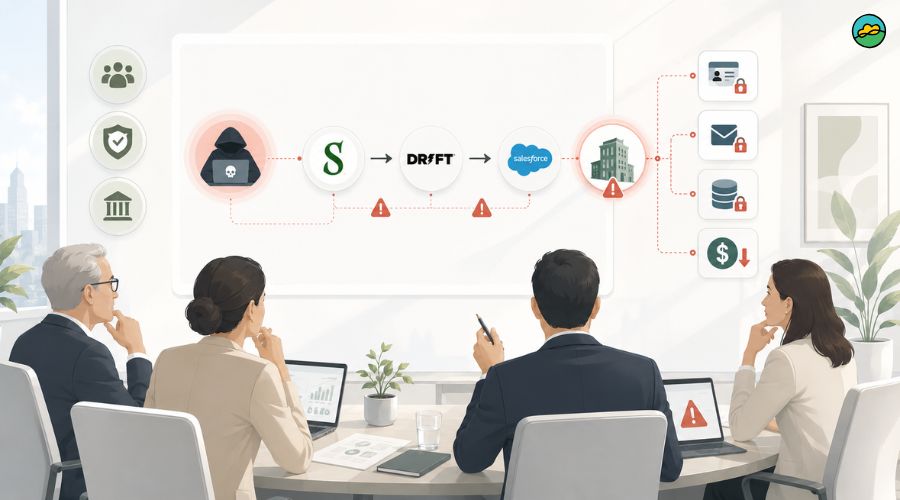
ToggleThird-party risk is no longer a procurement issue tucked away in a spreadsheet. The Salesloft-Drift-Salesforce breach is a blunt reminder that one connected app, one trusted integration, or one weak approval path can become a business-wide problem before the security team even has time to react.
What makes this case so uncomfortable is not just the breach itself but what it represents: the modern enterprise runs on connections. CRM platforms, sales automation tools, support systems, cloud apps, identity providers, and marketing platforms all talk to each other. That convenience proves beneficial until someone exploits trust.
Why this breach matters
The Salesloft-Drift-Salesforce incident is more than a vendor story. It is a board story, because it exposes how deeply organizations depend on external software to move revenue, manage customer data, and keep daily work flowing. When a trusted integration is compromised, the impact can spread faster than the response.
That is what makes third-party risk so dangerous. The exposure is not limited to the vendor that was directly attacked. It can extend to customer records, authentication pathways, connected platforms, downstream workflows, and business teams that never thought of themselves as “in scope” for cyber risk.
The bigger lesson behind the breach
The real lesson is that trust has become an attack surface. Organizations approve software because it saves time, improves sales productivity, or connects systems that business teams need to function. But every approved integration also creates a new dependency, and every dependency can become a doorway.
That is why third-party risk has moved from a technical concern to a governance problem. The more organizations rely on SaaS tools and connected workflows, the more they need leadership to understand that vendor oversight is not optional housekeeping. It is part of how the company protects revenue, customer trust, and operational continuity.

Ready to move beyond spreadsheets and static assessments?
See how TrustCloud helps you automate, scale, and modernize third-party risk management.
Learn MoreHow these breaches usually unfold
Third-party incidents often start in a way that looks minor. A token gets exposed, a user grants permissions too broadly, a connected app behaves unexpectedly, or an integration is trusted more than it should be. On its own, the weakness may not look dramatic. It becomes a significant breach vector when combined with other access points.
Security leaders find it uncomfortable that modern SaaS ecosystems prioritize speed over caution. Teams want frictionless connections between tools, and business users rarely see the hidden risk behind a one-click integration. Attackers know this, which is why they increasingly target the relationships between systems instead of the systems alone.
Why the board should care
Boards often hear third-party risk described in abstract terms: supply chain exposure, vendor governance gaps, and contractual blind spots. Those are true, but they are too soft to drive urgency. The better framing is this: third-party failure can interrupt revenue, create legal exposure, damage customer confidence, and force emergency response across multiple business units at once.
That is board-level risk because it affects value, not just controls. If a critical SaaS vendor is compromised, the company may face incident response costs, legal review, customer notifications, regulatory scrutiny, and operational disruption all at once. That is not an IT inconvenience. That is a business event.
What makes the Salesloft-Drift-Salesforce case so instructive
This breach is a warning sign because it sits at the intersection of sales operations, customer data, and cloud trust. Sales and CRM tools are especially sensitive because they contain business intelligence, customer records, communication histories, and operational workflows that power the front end of the business.
When an attacker reaches into that environment, the damage is not just technical. It can affect pipeline visibility, customer communications, account ownership, and internal confidence in the systems that drive revenue. In other words, a breach in the sales stack is not a side issue. It can impact the business directly.
Cyber risk assurance for enterprise CISOs
Trusted by Fortune 500 and Global 2000 in 10+ verticals. Replace manual risk assessments by translating 1st- and 3rd-party security signals into strategic risk management.
The hidden danger of connected apps
Connected apps are one of the most underestimated sources of third-party risk. Business users often approve them quickly, add them, and leave them in place long after the original need has changed. Over time, they accumulate permissions, retain access, and become part of the company’s normal operating rhythm.
That creates a dangerous illusion: if a tool is familiar, people assume it is safe. But familiarity is not security. A connected app may have broad access to customer records, metadata, emails, or administrative functions without anyone reviewing its continued justification. Once that happens, the app becomes part of the attack surface whether anyone intended it or not.
Why traditional vendor management is not enough
Many organizations still treat vendor risk as a questionnaire exercise. They send a form, collect answers, score the vendor, and move on. That approach may work for low-risk suppliers, but it fails badly in environments where vendors have direct access to sensitive data or critical workflows.
The Salesloft-Drift-Salesforce breach shows why. Security teams need to know not only whether a vendor has policies, but also how it connects to production systems, what permissions it has, how tokens are issued, how access is monitored, and how quickly access can be revoked. A signed form cannot answer those questions.
The real control gaps this kind of event exposes
Over-permissioned access
A lot of third-party risk starts with access that is broader than necessary. Vendors get admin privileges, long-lived tokens, or access to more data than their use case requires. Once that access is in place, it often remains unchanged because no one is responsible for periodic review.
Weak visibility
Organizations may know which vendors are under contract, but not which vendors are actively connected to production systems. That gap matters because the security team can only protect what it can see. Shadow integrations and business-managed apps can quietly widen exposure.
Slow revocation
When something goes wrong, speed matters. If access cannot be disabled quickly, the damage can continue after the breach is discovered. Strong third-party governance includes a clear offboarding process, emergency kill-switches, and tested access revocation steps.
Fragmented ownership
Third-party risk often falls between teams. Procurement owns the contract, IT owns the integration, security owns the control review, legal owns the clause review, and the business owns the use case. If someone owns the full path, they own the risk.
What good third-party governance looks like
Good third-party governance starts with an honest inventory. You need to know which vendors connect to sensitive systems, what type of access they have, which data they can reach, and which business processes depend on them. Without that map, every response is guesswork.
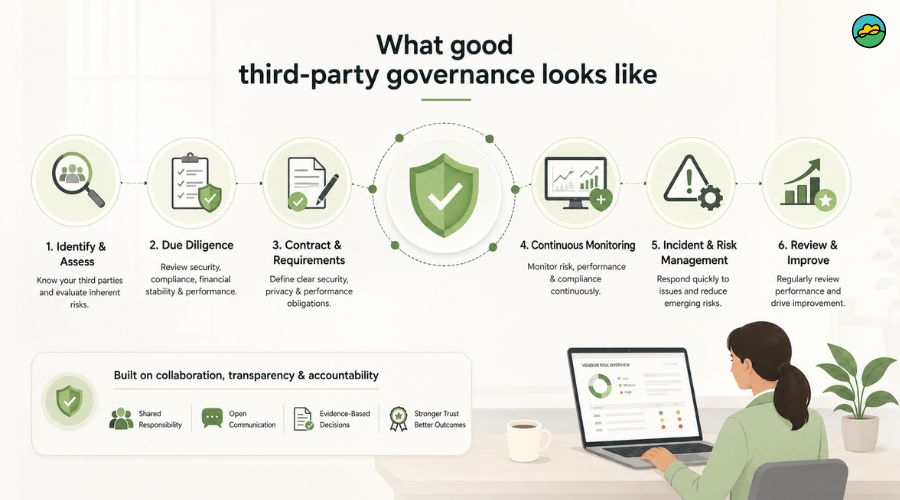
Then comes classification. Not every vendor needs the same level of scrutiny. A low-risk productivity app is not the same as a CRM integration with read-write access to customer data. The vendor tiering model should reflect actual access, not just annual spend or contract value.
Thereafter, organizations need continuous monitoring. Third-party risk is not static, because permissions change, employee behavior changes, integrations change, and vendors change their controls. A tool that received approval last year may now face significantly greater exposure.
The CISO’s uncomfortable truth
The uncomfortable truth is that many security teams do not control the most dangerous third-party connections. Business teams do. Sales, marketing, customer success, finance, and operations often adopt tools faster than security can review them due to their focus on speed and productivity.
That means the CISO cannot solve this problem with policy alone. The security program has to work inside the business, not above it. That includes building friction where needed, making approval easier for safe tools, and showing business leaders that effective governance does not slow growth; it protects it.
What boards should ask right now
Boards do not need a technical deep dive. They need the right questions. Which vendors have direct access to customer or operational data? Which integrations can be written to core systems? Which connected apps have been reviewed in the last 90 days? Please specify which vendor offboarding steps have been tested.
Those questions are simple, but they force clarity. If the answer is vague, the company probably does not have a mature third-party risk program. If the answer is precise, it means the organization understands where its real exposure lives.
A practical view of third-party risk maturity
| Maturity level | What it looks like | What can go wrong |
| Basic | Vendor questionnaires, contract review, annual reassessment | Hidden integrations, stale permissions, weak monitoring |
| Developing | Risk tiers, security reviews, access approvals, periodic audits | Gaps between procurement and security, slow response to changes |
| Mature | Inventory of all connected apps, continuous monitoring, tested revocation, board reporting | Fewer surprises, faster containment, clearer accountability |
The table is a useful reminder that maturity is not about having more forms. It is about knowing what is connected, why it is connected, and how quickly the organization can shut it off if trust breaks.
Read the “Ultimate third-party risk management playbook: Shield your business in the digital era” article to learn more!
The business consequences people underestimate
Breaches involving trusted third parties can be particularly damaging, as they erode confidence in systems designed to foster business growth. Sales teams may lose trust in CRM data. Operations teams may slow down approvals. Legal teams may need to review notification obligations. Executives may have to explain why a trusted tool became a liability.
The loss of confidence can persist even after resolving the technical issue. In many organizations, the hardest part of recovery is not restoring the system. It is restoring trust in the process that allowed the system in the first place.
Why this is really a governance story
At a deeper level, the Salesloft-Drift-Salesforce breach is a story about decision-making. Who approved the connection? Who reviewed the permissions? Who owned the ongoing risk? Who had the authority to revoke access? If those answers are unclear, the problem is not only technical. It is organizational.
Effective governance makes those answers obvious. Poor governance leaves them scattered across ticketing systems, email threads, and tribal knowledge. That is why third-party risk has become a leadership issue. It reveals whether the company can govern the technology it depends on.
What security teams should do next
Security teams should start by mapping every external app and service connected to critical systems, especially CRM, finance, support, identity, and data platforms. Then they should review access levels, token lifetimes, admin privileges, and data movement paths.
Next, they should tighten approval controls for new integrations and require periodic revalidation for existing ones. If an app has not been used, should it still have access? If a vendor no longer needs write permissions, why keep them?
Finally, they should run revoke-and-contain drills. If a vendor or connected app is compromised, the organization should know exactly how to cut access, notify stakeholders, preserve evidence, and assess downstream impact. That rehearsal is the difference between a controlled incident and a scrambling crisis.
Read the “Third-party risk management: How to go from reactive to proactive” article to learn more!
What this breach teaches us about the future
The future of cyber risk is increasingly relational. Attackers are not only looking for weak passwords or unpatched servers. They are looking for trust relationships, API connections, delegated permissions, and business-approved shortcuts.
That means the companies most at risk are often sophisticated. They are often the most connected. The more a business depends on cloud apps and partner integrations, the more it must treat third-party governance as a core control, not a side process.
Summing it up
Third-party risk is a board-level crisis because it can turn everyday business convenience into enterprise-wide exposure. The Salesloft-Drift-Salesforce breach serves as a warning that connected systems require connected governance.
CISOs must be aware of their vendors, integrations, permissions, and the speed at which they can terminate trust when it fails. For boards, the message is even simpler: if you do not understand your third-party exposure, you do not fully understand your risk.
FAQs
Why is third-party risk considered a board-level issue rather than just an IT concern?
Third-party risk has moved beyond the security team because a single compromised vendor or integration can affect business value, not just technical controls. When a trusted SaaS tool is breached, the organization may face incident response costs, legal review, customer notifications, regulatory scrutiny, and operational disruption simultaneously, a business event, not an IT inconvenience. Modern enterprises run on connections between CRM platforms, sales automation tools, identity providers, and cloud apps, so a failure in one integration can interrupt revenue, damage customer confidence, and force emergency response across multiple business units at once.
Boards need to understand third-party exposure because if leadership does not understand where the company’s vendor dependencies live, it does not fully understand the company’s risk. Vendor oversight is now part of how an organization protects revenue, customer trust, and operational continuity.
Why is traditional vendor management, like questionnaires and annual reviews, not enough to manage third-party risk?
Traditional vendor management typically works as a questionnaire exercise: send a form, collect answers, score the vendor, and move on. That approach may be adequate for low-risk suppliers, but it fails badly when vendors have direct access to sensitive data or critical workflows.
A signed questionnaire cannot tell you how a vendor actually connects to production systems, what permissions it holds, how tokens are issued, how access is monitored, or how quickly access can be revoked if something goes wrong. Third-party risk is also not static, permissions change, integrations evolve, and vendors update their own controls, so a tool approved last year may carry significantly more exposure today. Effective programs replace static forms with an honest inventory of connected apps, risk tiering based on actual access levels rather than contract value, and continuous monitoring of how those connections behave over time.
What steps should security teams take right now to strengthen third-party governance?
Security teams should begin by mapping every external app and service connected to critical systems, especially CRM, finance, support, identity, and data platforms. From there, review access levels, token lifetimes, admin privileges, and data movement paths to identify over-permissioned connections. Next, tighten approval controls for new integrations and require periodic revalidation of existing ones, if an app has not been used recently, or a vendor no longer needs write permissions, that access should be removed.
Teams should also address common control gaps such as weak visibility into shadow integrations, slow revocation processes, and fragmented ownership across procurement, IT, security, and legal. Finally, run revoke-and-contain drills so the organization knows exactly how to cut access, notify stakeholders, preserve evidence, and assess downstream impact if a vendor is compromised. That rehearsal is the difference between a controlled incident and a scrambling crisis.