

On this page
ToggleOverview
Every time a payment card ticks through your business, whether in store, online or on the move, the security of that transaction hinges on more than just encryption and firewalls. It is backed by the rigorous framework of the Payment Card Industry Data Security Standard (PCI DSS), and ultimately sealed with the formal declaration known as the Attestation of Compliance (AoC).
For organizations processing, storing or transmitting cardholder data, the AoC isn’t a simple formality, it’s a critical milestone. It signals to partners, acquirers and regulators that your systems, controls and documentation meet the exacting demands of PCI DSS. In a world where breaches and fines dominate headlines, mastering this process means more than compliance, it means trust, resilience and business continuity.
This article provides a comprehensive guide to understanding and achieving Payment Card Industry Data Security Standard (PCI DSS) compliance, focusing on the Attestation of Compliance (AOC) process. It details the requirements of PCI DSS, including network security, access controls, and vulnerability management. The article further outlines the steps involved in the AOC process, from self-assessment questionnaires to penetration testing and documentation. Strategies for overcoming common challenges and best practices for maintaining compliance are also discussed, along with helpful resources.
What is PCI DSS?
The Payment Card Industry Data Security Standard (PCI DSS) is a globally recognized framework designed to protect cardholder data and ensure secure payment transactions. It was established by the Payment Card Industry Security Standards Council (PCI SSC), a group formed by major credit card brands like Visa, MasterCard, American Express, Discover, and JCB to create a unified set of security standards for any organization that stores, processes, or transmits payment card information.
PCI DSS outlines 12 core requirements that focus on areas such as building secure networks, encrypting data, maintaining access controls, and regularly monitoring systems for vulnerabilities. These requirements apply to all entities that handle cardholder data, regardless of their size or transaction volume.
PCI DSS is about establishing a security-first culture that minimizes the risk of data breaches and reinforces customer trust. Compliance with PCI DSS helps businesses demonstrate accountability, reduce exposure to financial and reputational damage, and maintain strong relationships with payment providers and customers.
What are the requirements of PCI DSS?
The Payment Card Industry Data Security Standard (PCI DSS) outlines 12 comprehensive requirements designed to safeguard payment card data from theft, misuse, or unauthorized access. These standards form the foundation for secure payment environments and apply to all organizations that store, process, or transmit cardholder information.
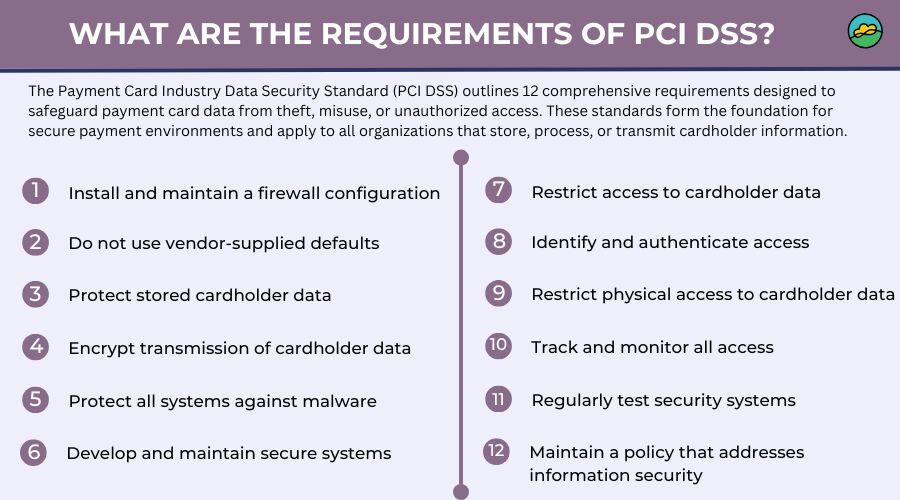
By meeting these requirements, businesses can significantly reduce security risks, demonstrate compliance, and build trust with customers and partners. Each requirement plays a crucial role in ensuring the integrity, confidentiality, and availability of sensitive payment data throughout its lifecycle.
- Install and maintain a firewall configuration to protect cardholder data
Firewalls serve as the first line of defense between trusted internal systems and untrusted external networks. Organizations must configure firewalls properly to block unauthorized traffic, restrict public access, and secure connections to payment systems. Regular reviews and updates of firewall rules help maintain protection against evolving cyber threats and network vulnerabilities. - Do not use vendor-supplied defaults for system passwords and security parameters
Default credentials and settings are widely known and easily exploited by attackers. Businesses should replace all vendor-supplied passwords, remove unnecessary accounts, and disable default configurations. Establishing secure password policies and enforcing strong authentication ensures that only authorized users can access sensitive systems and data. - Protect stored cardholder data
Any stored cardholder data must be rendered unreadable using encryption, truncation, masking, or hashing. Sensitive authentication data such as CVVs or PIN blocks, should never be stored post-authorization. Regularly review data retention policies to ensure information is kept only as long as necessary, minimizing exposure to breaches and unauthorized access. - Encrypt transmission of cardholder data across open, public networks
When transmitting payment information over public networks, encryption is essential to prevent data interception. Use strong encryption protocols (like TLS) to secure communications between systems, customers, and third-party vendors. Avoid unencrypted channels such as email or FTP for sensitive transactions to maintain data confidentiality. - Protect all systems against malware and regularly update antivirus software
Malware can infiltrate systems through downloads, phishing, or infected devices. To mitigate these risks, deploy reputable antivirus software and ensure it’s updated regularly. Conduct system scans frequently, monitor for suspicious activities, and enforce controls that prevent users from disabling or tampering with antivirus tools. - Develop and maintain secure systems and applications
Security should be built into every stage of the software lifecycle. Apply patches and updates promptly to address known vulnerabilities. Conduct code reviews and penetration testing for applications that handle payment data. Maintaining secure coding practices helps protect systems from common attacks such as SQL injection or cross-site scripting. - Restrict access to cardholder data by business need-to-know
Access should only be granted to employees whose roles require handling cardholder data. Implement role-based access controls, review permissions regularly, and remove access immediately for employees who change roles or leave the company. This limits the potential damage from insider threats and accidental exposure. - Identify and authenticate access to system components
Every user with computer access should have a unique ID to ensure accountability. Implement multi-factor authentication for all users accessing sensitive systems, especially remotely. Track login attempts, enforce password complexity, and lock accounts after repeated failed attempts to strengthen system access security. - Restrict physical access to cardholder data
Data security extends beyond digital protection. Limit physical access to systems and facilities that store cardholder information using locks, surveillance, and access logs. Visitors should be escorted and recorded. Proper physical safeguards prevent unauthorized personnel from viewing, copying, or removing sensitive data. - Track and monitor all access to network resources and cardholder data
Logging and monitoring are vital for detecting unauthorized activities. Maintain detailed logs of all system access, including user IDs, timestamps, and actions taken. Use intrusion detection or prevention systems to identify anomalies, and retain logs for review during audits or investigations. - Regularly test security systems and processes
Frequent testing ensures your defenses remain effective. Conduct vulnerability scans, penetration testing, and intrusion detection reviews regularly. Test firewalls, wireless access points, and applications for weaknesses. Document results and remediate findings promptly to maintain continuous compliance and robust protection. - Maintain a policy that addresses information security for all personnel
A strong security policy sets clear expectations for all employees. It should define roles, responsibilities, acceptable use, and data handling procedures. Conduct regular training and awareness programs to keep staff informed about new threats and their role in protecting payment card data.
The 12 PCI DSS requirements form a complete roadmap for organizations to build and maintain a secure payment ecosystem. Compliance is a continuous commitment to safeguarding customer trust. By implementing these controls consistently, organizations can reduce the risk of data breaches, maintain regulatory confidence, and ensure safe, seamless payment experiences for all stakeholders.
PCI DSS – Overview and Guides
Understanding the Payment Card Industry Data Security Standard (PCI DSS)
The Payment Card Industry Data Security Standard (PCI DSS) is a set of security requirements designed to protect cardholder data and reduce the risk of data breaches. It applies to any organization that processes, stores, or transmits credit card information. Understanding the requirements of PCI DSS is essential for successfully navigating the Attestation of Compliance (AOC) process.
To achieve compliance with PCI DSS, businesses must implement a range of security measures, including network firewalls, encryption, access controls, and regular vulnerability assessments. Compliance with these requirements helps to ensure the security of cardholder data and build trust with customers.
Key pillars of PCI DSS: What you need to know before attestation
Understanding the core requirements of PCI DSS is essential for businesses aiming to complete their Attestation of Compliance (AOC) with confidence. These requirements represent fundamental practices for protecting payment card data and reducing risk exposure.
PCI DSS outlines 12 essential security requirements, grouped into six overarching goals. These include securing your systems through firewalls and strong passwords, protecting stored and transmitted cardholder data, and maintaining a vulnerability management program. Organizations must also implement robust access controls, routinely monitor network activity, and develop a clear security policy.
Each requirement builds on the others to form a comprehensive, layered defense strategy. For example, Requirement 3 focuses on safeguarding stored cardholder data using encryption and masking, while Requirement 10 ensures that all access to this data is tracked and logged for accountability. Together, these practices ensure that sensitive information is not only hard to access but also monitored in real time.
For companies working toward PCI DSS compliance, these requirements act as a roadmap. Meeting them is necessary not only for regulatory purposes but also for gaining customer trust and maintaining a secure operating environment.
Before submitting your AOC, ensure your organization has fully aligned with each of the 12 requirements. Proper documentation, internal audits, and evidence of security controls will strengthen your submission and reduce the likelihood of delays or failures during the attestation process.
Read the “PCI compliance simplified: Choose between PCI SAQ and PCI DSS with confidence” article to learn more!
Importance of achieving PCI DSS compliance
Achieving PCI DSS compliance goes far beyond meeting a checklist; it’s about building a foundation of trust and resilience. Compliance demonstrates that your organization takes data protection seriously and has implemented strong controls to safeguard sensitive payment information.
In an era of rising cyber threats and data breaches, PCI DSS compliance not only prevents financial loss but also protects your brand reputation. Moreover, it positions your business as a reliable and security-conscious partner, opening doors to new collaborations, clients, and growth opportunities in competitive markets.
- Strengthens data protection
PCI DSS compliance ensures your organization follows strict security standards that protect cardholder data. This includes encryption, access controls, and regular system monitoring. These practices significantly reduce the risk of unauthorized access or data theft, helping maintain the confidentiality and integrity of payment information at every stage of processing. - Reduces financial and legal risks
Non-compliance can lead to severe penalties, legal consequences, and costly data breach recoveries. Achieving PCI DSS compliance helps your organization avoid fines and potential lawsuits. It also demonstrates proactive risk management, ensuring you meet both regulatory and contractual obligations tied to payment security. - Builds customer trust and confidence
When customers see that you are PCI DSS compliant, they know their payment information is handled securely. This trust translates into customer loyalty and higher retention rates. Demonstrating your commitment to compliance reassures clients that their personal and financial data is safe from misuse or breaches. - Enhances reputation and brand credibility
Compliance acts as a visible commitment to security excellence. Organizations that consistently meet PCI DSS standards earn a reputation for professionalism and reliability. This reputation can distinguish your brand in a crowded marketplace, helping attract partners, clients, and stakeholders who value transparency and risk-conscious operations. - Improves operational efficiency
The process of achieving PCI DSS compliance often leads to stronger internal governance and better data management. Implementing structured security controls, regular audits, and documentation practices enhances overall efficiency. These improvements streamline workflows, reduce redundancies, and create a culture of accountability within your organization. - Unlocks new business opportunities
Many enterprises, especially in banking and e-commerce, mandate PCI DSS compliance for vendors and partners. Meeting these standards gives your organization access to broader markets and high-value clients. Compliance showcases your readiness to handle sensitive data responsibly, giving you a competitive edge in partnership evaluations.
Achieving PCI DSS compliance is a strategic investment in long-term success. It protects your organization against data breaches, strengthens customer relationships, and enhances your market credibility. More than a security framework, PCI DSS is a business enabler, one that promotes trust, operational excellence, and sustainable growth in the digital economy.
The components of the attestation of compliance process
The Attestation of Compliance (AOC) process involves several components that businesses must fulfill to demonstrate their compliance with PCI DSS.
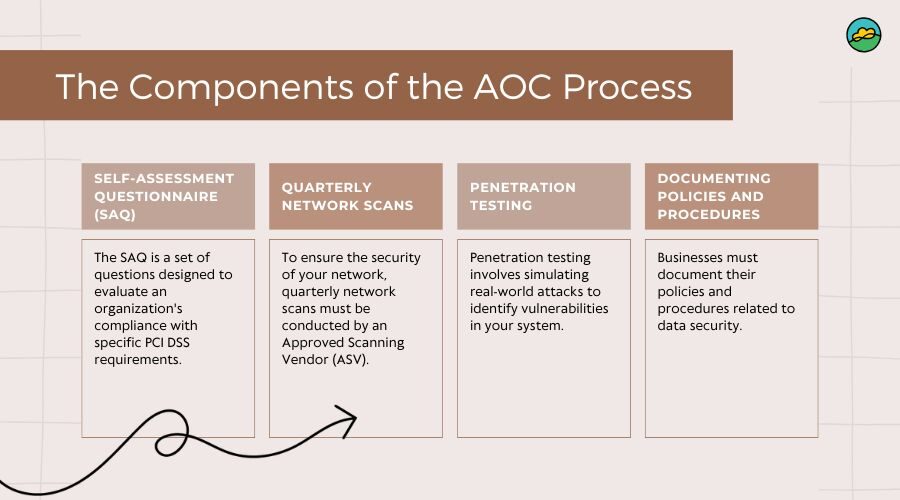
These components include:
- Self-Assessment Questionnaire (SAQ)
The SAQ is a set of questions designed to evaluate an organization’s compliance with specific PCI DSS requirements. There are different versions of the SAQ, each tailored to different types of businesses and their level of cardholder data exposure. - Quarterly Network Scans
To ensure the security of your network, quarterly network scans must be conducted by an Approved Scanning Vendor (ASV). These scans identify any vulnerabilities that could potentially be exploited by attackers. - Penetration Testing
Penetration testing involves simulating real-world attacks to identify vulnerabilities in your system. This testing helps uncover any weaknesses that could be exploited by hackers and provides valuable insights into the effectiveness of your security measures. - Documenting Policies and Procedures
Businesses must document their policies and procedures related to data security. These documents outline the steps and protocols to follow to ensure compliance with PCI DSS and maintain data security.
Preparing for the AOC process
Before beginning the Attestation of Compliance (AOC) process, organizations must ensure they’re fully prepared to demonstrate their adherence to PCI DSS requirements. Preparation is key to avoiding delays, errors, or compliance gaps that could lead to failed assessments or reputational damage. By establishing clear responsibilities, assessing readiness, and creating a structured plan, your organization can approach the AOC process with confidence and efficiency. The following steps outline how to lay a solid foundation for successful PCI DSS attestation.
- Determine applicability
Start by understanding whether your organization falls within the PCI DSS scope. Identify the type of cardholder data you process, store, or transmit, and map out all related systems and networks. This step ensures clarity on your compliance obligations and helps you focus on the controls most relevant to your environment. - Assign responsibility
Designate a compliance lead or team to manage the AOC process from start to finish. This person should have deep knowledge of PCI DSS requirements and coordinate efforts across IT, security, operations, and management teams. Centralized oversight ensures accountability, consistency, and clear communication throughout the attestation journey. - Educate employees
Employees are your first line of defense in maintaining compliance. Conduct regular training sessions to educate them on PCI DSS standards, proper data handling practices, and incident response procedures. Empowering staff with knowledge reduces the likelihood of accidental data exposure and fosters a culture of shared responsibility for security. - Conduct a gap analysis
Perform a thorough gap analysis to compare your current security posture with PCI DSS requirements. Identify noncompliant areas, outdated processes, or missing controls. Document findings and prioritize them based on risk. This assessment provides a clear roadmap for improvement and helps you allocate resources efficiently before the audit phase. - Develop an action plan
Based on the gap analysis, create a detailed action plan outlining specific tasks, responsible owners, deadlines, and resource allocations. Define measurable objectives and track progress regularly. A structured plan ensures that remediation efforts stay on schedule, allowing your organization to demonstrate continuous improvement and readiness for assessment. - Engage external experts
Consider bringing in external PCI DSS consultants or Qualified Security Assessors (QSAs) to guide your efforts. Their experience can help interpret complex requirements, validate your controls, and prepare documentation for submission. External experts can also conduct mock audits, ensuring your organization meets compliance expectations before the formal attestation process begins.
Thorough preparation is the cornerstone of a smooth AOC process. By defining responsibilities, assessing gaps, and leveraging expert support, your organization can approach the attestation with clarity and confidence. This proactive groundwork not only simplifies compliance but also reinforces your long-term commitment to safeguarding payment data and maintaining customer trust.
Read the “PCI DSS attestation of compliance: Complete guide to achieve certification” article to learn more!
Steps to complete the AOC process
Completing the Attestation of Compliance (AOC) process is a critical milestone for any organization handling cardholder data. It not only validates your adherence to PCI DSS standards but also demonstrates your organization’s ongoing dedication to protecting customer payment information. The process requires structured effort, from self-assessment to vulnerability testing and documentation.
Each step builds upon the other to create a robust framework for compliance. Below are the key stages involved in successfully completing the AOC process.
- SAQ completion
Begin by completing the appropriate Self-Assessment Questionnaire (SAQ) based on your organization’s role and data handling practices. The SAQ helps evaluate your compliance level with PCI DSS controls, such as access restrictions, encryption, and monitoring. Accurate and honest responses are essential to reflect your organization’s true security posture and avoid future compliance discrepancies. - Network scans
Engage an Approved Scanning Vendor (ASV) to conduct quarterly network scans. These scans are designed to detect vulnerabilities in your systems, firewalls, and applications that could expose cardholder data. Addressing identified issues quickly ensures your organization maintains a secure environment and meets PCI DSS’s ongoing vulnerability management requirements. - Penetration testing
Conduct penetration testing to evaluate the effectiveness of your existing security measures. This simulated attack approach reveals potential weaknesses that automated scans might overlook. Both internal and external tests are recommended to assess end-to-end defenses. Remediate all identified vulnerabilities promptly to reinforce your systems against real-world cyber threats. - Documentation
Maintain thorough documentation of all policies, procedures, and controls related to PCI DSS compliance. This includes incident response plans, encryption policies, and access management protocols. Documentation serves as proof of consistent compliance efforts and provides auditors with clear visibility into how your organization secures cardholder data. Update it regularly to reflect any process changes. - Attestation
Once all assessments, scans, and remediations are complete, prepare and submit your Attestation of Compliance (AOC) to your acquiring bank or payment processor. This formal document certifies that your organization meets all applicable PCI DSS requirements. Submitting an accurate and complete AOC reinforces your credibility and demonstrates your proactive stance on protecting sensitive payment data.
By following these structured steps, self-assessment, scanning, testing, documentation, and attestation, your organization can confidently navigate the AOC process. Beyond compliance, this process fosters stronger data protection, minimizes risk, and enhances customer trust. Successfully completing your AOC not only satisfies regulatory obligations but also positions your organization as a responsible and trustworthy partner in the digital payments ecosystem.
PCI DSS – Overview and Guides
Common challenges and how to overcome them
Navigating the Attestation of Compliance (AOC) process can present various challenges for businesses. Here are some common challenges and strategies to overcome them:
- Lack of Awareness
Many businesses are not fully aware of the importance of PCI DSS compliance or the specific requirements involved. Invest in employee education and training to ensure a clear understanding of compliance obligations. - Resource Constraints
Smaller businesses may face resource constraints when implementing the necessary security measures and completing the AOC process. Prioritize actions based on risk and consider outsourcing certain tasks to experts to optimize resource allocation. - Complexity
The AOC process can be complex, especially for organizations with multiple systems and locations. Engage external experts to help navigate the complexities and ensure thorough compliance. - Keeping Up with Updates
PCI DSS requirements are regularly updated to address emerging threats and vulnerabilities. Stay informed about the latest updates and allocate resources to implement necessary changes promptly.
By proactively addressing these challenges, you can streamline your AOC process and ensure ongoing compliance with PCI DSS.
Read the “The Future of SLAs: Are We Measuring What Matters?” article to learn more!
Best practices for maintaining PCI DSS compliance
Achieving compliance with the Payment Card Industry Data Security Standard (PCI DSS) is not a one-time effort. It requires ongoing commitment and vigilance to maintain data security. Here are some best practices to help you maintain PCI DSS compliance:
- Regularly Monitor and Test
Continuously monitor your network for any suspicious activities or vulnerabilities. Perform regular vulnerability assessments, network scans, and penetration testing to identify and address potential weaknesses promptly. - Keep Software Up-to-Date
Ensure that all software and systems within your organization are up-to-date with the latest security patches and updates. Regularly review and update your security configurations to align with industry best practices. - Educate and Train Employees
Provide regular training and education to employees regarding data security best practices. Make them aware of the latest threats and ensure they understand their role in maintaining compliance. - Implement Access Controls
Implement strong access controls to limit access to cardholder data only to authorized personnel. Regularly review and update user access privileges to minimize the risk of unauthorized access. - Encrypt Cardholder Data
Implement encryption for all cardholder data, both at rest and in transit. Encryption helps protect sensitive information, even if it falls into the wrong hands. - Maintain Documentation
Regularly review and update your policies and procedures related to data security. Keep detailed documentation of security measures implemented, incidents, and remediation efforts.
By following these best practices, you can establish a robust data security framework and maintain PCI DSS compliance over the long term.
Read the article Heightened Regulatory Scrutiny: How to Meet Compliance Demands to learn more!
Resources and tools
Navigating the Attestation of Compliance (AOC) process can be complex, but there are several resources and tools available to assist businesses in achieving and maintaining compliance with PCI DSS. Here are some valuable resources you can leverage:
- PCI Security Standards Council
The PCI Security Standards Council website provides a wealth of information and resources related to PCI DSS compliance. It offers guidance documents, self-assessment questionnaires, and training materials to help organizations navigate the AOC process. - Approved Scanning Vendors (ASVs)
Engaging an ASV to conduct quarterly network scans is a requirement for PCI DSS compliance. ASVs are qualified vendors approved by the PCI Security Standards Council to perform network vulnerability scans. Their expertise can help identify and address vulnerabilities in your network. - Qualified Security Assessors (QSAs)
If your organization requires a more comprehensive assessment of its compliance with PCI DSS, engaging a Qualified Security Assessor (QSA) can be beneficial. QSAs are individuals or organizations certified by the PCI Security Standards Council to assess compliance with PCI DSS. - Security Information and Event Management (SIEM) Systems
SIEM systems can help organizations monitor and manage security events and incidents. These systems provide real-time alerts, log analysis, and threat intelligence to help identify and respond to potential security breaches.
By leveraging these resources and tools, you can streamline your AOC process and ensure comprehensive compliance with PCI DSS.
The importance of ongoing compliance efforts
In an increasingly interconnected world, data security should be a top priority for businesses. Navigating the Attestation of Compliance (AOC) process is crucial to ensuring compliance with industry regulations and protecting sensitive information.
By understanding the Payment Card Industry Data Security Standard (PCI DSS), preparing diligently, and following best practices, businesses can successfully complete the AOC process and maintain ongoing compliance. Remember to leverage available resources and engage external experts when needed to optimize your compliance efforts.
By prioritizing data security and maintaining PCI DSS compliance, organizations can establish trust with customers and business partners, protect their reputation, and safeguard sensitive data from potential breaches. Stay vigilant, adapt to emerging threats, and remain committed to ongoing compliance efforts for a secure and resilient business environment.
Trust assurance, being an important factor in the rapidly changing compliance-aware digital era, always insists on building and maintaining trust among your stakeholders.
Ready to save time and money on audits, pass security reviews faster, and manage enterprise-wide risk?
FAQs
What is PCI DSS and why is it important?
The Payment Card Industry Data Security Standard (PCI DSS) is a set of security requirements designed to protect cardholder data and reduce the risk of data breaches. It applies to any organization that processes, stores, or transmits credit card information. Achieving PCI DSS compliance is crucial not only for meeting regulatory requirements but also for protecting your business from data breaches, financial losses, and reputational damage. Compliance demonstrates your commitment to data security and builds trust with customers and partners, potentially opening new business opportunities.
What is the Attestation of Compliance (AOC) and how does it relate to PCI DSS?
The Attestation of Compliance (AOC) is the process by which an organization demonstrates its adherence to the PCI DSS. It involves a thorough evaluation of an organization’s IT infrastructure, policies, and procedures to ensure they meet the standards defined in PCI DSS.
Completing the AOC involves a series of steps, including assessments, scans, and documentation, ultimately leading to a formal attestation that confirms compliance. The AOC process is a means to verify and validate an organization’s security posture in handling cardholder data.
What are the key components of the AOC process?
The AOC process includes several key components:
- Self-Assessment Questionnaire (SAQ): A set of questions designed to evaluate an organization’s compliance with specific PCI DSS requirements. Different versions of the SAQ are tailored to varying business types and levels of cardholder data exposure.
- Quarterly Network Scans: Conducted by an Approved Scanning Vendor (ASV) to identify network vulnerabilities.
- Penetration Testing: Simulating real-world attacks to uncover system vulnerabilities and test the effectiveness of security measures.
- Documenting Policies and Procedures: Outlining the steps and protocols to ensure compliance with PCI DSS and maintain data security.
What steps should an organization take to prepare for the AOC process?
Thorough preparation is essential for a smooth AOC process. Key steps include:
- Determining Applicability: Understand if your organization falls under the scope of PCI DSS based on the type of cardholder data you handle.
- Assigning Responsibility: Designating a team or individual to manage the AOC process.
- Educating Employees: Ensuring all staff understand compliance obligations and best practices.
- Conducting a Gap Analysis: Identifying where your organization falls short of PCI DSS requirements.
- Developing an Action Plan: Creating a detailed plan with realistic timelines for remediation.
- Engaging External Experts: Consider utilizing consultants or auditors for expert guidance.
What are some of the common challenges encountered during the AOC process, and how can they be addressed?
Organizations often face challenges such as
- Lack of Awareness: Address this through employee training and education on PCI DSS requirements.
- Resource Constraints: Prioritize actions based on risk and outsource specific tasks to experts if needed.
- Complexity: Engage external experts for help in navigating complex compliance procedures.
- Keeping Up with Updates: Stay informed about PCI DSS updates and allocate resources to promptly implement any necessary changes.