
Essential NIST password guidelines for stronger security
On this page
ToggleOverview
When cyber threats are increasingly sophisticated, traditional password practices are no longer sufficient to safeguard sensitive information. The National Institute of Standards and Technology (NIST) has recognized this shift and, introduced updated password guidelines to bolster cybersecurity measures.
These guidelines emphasize the adoption of passwordless authentication methods, the implementation of adaptive authentication policies, and the integration of continuous monitoring systems. By aligning with these updated standards, organizations can enhance their security posture, reduce the risk of unauthorized access, and foster a more resilient digital environment. Understanding and implementing these guidelines is crucial for staying secure in an ever-evolving threat landscape.
This article primarily details the 2026 updates to NIST password guidelines, emphasizing passwordless authentication, adaptive policies, continuous monitoring, and password manager integration to enhance cybersecurity. It highlights the importance of strong password practices and offers various tools and resources for implementing these guidelines with TrustCloud helping organizations achieve compliance and improve their overall security posture.
What are NIST password guidelines?
The importance of robust password practices cannot be overstated. As technology advances, so do the threats posed by malicious actors seeking to exploit vulnerabilities. Enter the NIST Password Guidelines, a comprehensive set of recommendations aimed at fortifying password security and safeguarding sensitive information. These guidelines, issued by the National Institute of Standards and Technology (NIST), serve as a beacon for organizations and individuals alike, illuminating the path towards enhanced data protection.
Why are password guidelines important?
Passwords are often the first line of defense against unauthorized access to critical systems and sensitive data. Weak or easily guessable passwords can render even the most sophisticated security measures ineffective, leaving organizations vulnerable to devastating breaches. By adhering to well-established password guidelines, you can significantly reduce the risk of compromise and fortify your digital defenses.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MoreEvolution of NIST password guidelines
The NIST Password Guidelines have undergone a remarkable transformation over the years, adapting to the ever-changing cybersecurity landscape. From the initial recommendations in 2003 to the groundbreaking updates in 2017, these guidelines have consistently challenged conventional wisdom and pushed the boundaries of password security best practices.
The evolution of NIST password guidelines is absolutely fascinating! Over the years, the National Institute of Standards and Technology (NIST) has revolutionized how we think about password security. Initially, their guidelines suggested complex passwords with a mix of uppercase and lowercase letters, numbers, and special characters. However, this often led to user frustration and predictable patterns.

Recognizing the need for improvement, NIST updated its guidelines in 2017, focusing on longer passphrases that are easier to remember but harder to crack. They also recommended against frequent mandatory password changes and discouraged the use of security questions due to their vulnerability. These changes have significantly enhanced both the user experience and security measures. The constant evolution of NIST guidelines shows their commitment to adapting to new threats and improving cybersecurity for everyone!
Read the “Heightened Regulatory Scrutiny: How to Meet Compliance Demands” article to learn more!
The importance of CSF certification for staying secure while implementing NIST password guidelines
As organizations adopt the 2026 NIST password guidelines, achieving CSF certification ensures they implement these guidelines securely and effectively. The certification validates compliance with the broader NIST Cybersecurity Framework (CSF) and integrates password policies into a robust cybersecurity strategy.

Here’s why CSF certification is crucial for staying secure while implementing these updates:
- Ensures compliance with updated password standards
CSF certification ensures organizations fully implement these changes while adhering to other critical security controls. The 2026 NIST guidelines emphasize modern, secure password practices, including:- Eliminating mandatory password changes unless there’s evidence of compromise.
- Using passphrases instead of overly complex passwords.
- Prohibiting knowledge-based authentication methods is prone to compromise.
- Validates risk-based authentication approaches
CSF certification validates the integration of these adaptive mechanisms into the organization’s authentication systems, enhancing overall security. The guidelines encourage risk-based authentication, where security measures adjust based on context, such as:- Detecting unusual login activity.
- Adding layers of verification for high-risk scenarios.
- Promotes strong credential protection
Credential compromise remains a top attack vector. CSF certification ensures organizations adopt robust measures, such as:- Screening passwords against lists of commonly used or compromised credentials.
- Encrypting passwords using secure hashing algorithms like bcrypt or Argon2.
- Implementing multi-factor authentication (MFA) to reduce reliance on passwords alone.
- Facilitates secure implementation of usability enhancements
The 2025 guidelines emphasize balancing security with usability. By improving user experience, organizations reduce weak password practices while maintaining strong security postures. CSF certification ensures organizations:- Simplify password policies without compromising security, making it easier for users to comply.
- Provide clear guidance on creating secure yet memorable passphrases.
- Aligns password policies with organizational security goals
CSF certification ensures password management is integrated into a broader cybersecurity framework, including:- Zero-trust architecture to secure access at every level.
- Incident response plans to mitigate credential-based attacks like phishing or brute force attempts.
- Demonstrates commitment to stakeholders
CSF certification signals to customers, partners, and regulators that the organization:- Prioritizes secure authentication practices.
- Complies with leading standards like the NIST password guidelines.
- Supports continuous improvement and threat adaptation
CSF certification requires regular audits and assessments, ensuring organizations:- Continuously improve password policies to address emerging threats.
- Stay up to date with future updates to the NIST guidelines.
- Reduces risks from credential-based attacks
Implementing the guidelines under CSF certification strengthens defenses against threats like:- Credential-stuffing attacks.
- Phishing attempts to harvest login credentials.
By integrating advanced detection and response mechanisms, organizations ensure password-related vulnerabilities are addressed comprehensively.
CSF certification is essential for staying secure while implementing the 2025 NIST password guidelines. It validates compliance, enhances risk-based authentication, and integrates password policies into a resilient cybersecurity framework. By aligning security practices with usability and adapting to emerging threats, organizations can ensure both robust defenses and user satisfaction. Achieving CSF certification not only strengthens password security but also reinforces trust, compliance, and resilience in the face of evolving cyber risks.
Demonstrate responsibility and trust around AI
Develop, deploy, and manage your AI systems with ISO 42001 and NIST AI RMF to show your customers and prospects that as your technology advances, your GRC keeps pace.
Key updates in the NIST password guidelines
The forthcoming NIST Password Guidelines promise to be a game-changer, introducing innovative approaches and addressing emerging threats. Here are some of the key updates you can expect:
- Password less Authentication
Recognizing the inherent vulnerabilities of traditional password-based authentication, the guidelines will place a strong emphasis on passwordless technologies. These include biometrics, hardware security keys, and other advanced authentication methods, offering a more secure and user-friendly alternative. - Adaptive Password Policies
Rather than a one-size-fits-all approach, the guidelines will advocate for adaptive password policies tailored to the specific risk profiles of organizations. This will allow for more nuanced and effective security measures based on the sensitivity of the data being protected. - Continuous Monitoring and Evaluation
The guidelines will stress the importance of continuously monitoring and evaluating password security practices. This proactive approach will enable organizations to stay ahead of emerging threats and adapt their strategies accordingly. - Password Manager Integration
Acknowledging the challenges of managing complex passwords, the guidelines will encourage the use of reputable password managers. By integrating these tools into organizational policies, users can benefit from secure password generation, storage, and retrieval.
The updates in the NIST Password Guidelines are driven by a deep understanding of the evolving threat landscape and the limitations of traditional password practices. As cyber attacks become more sophisticated and targeted, it is crucial to adopt a multi-layered approach to security, combining robust authentication methods with continuous monitoring and adaptive policies.
Implementing the NIST password guidelines in your organization
Adopting the NIST Password Guidelines 2026 within your organization is a critical step towards enhancing cybersecurity posture. However, the implementation process requires careful planning and execution. Here are some key considerations:
- Conduct a Comprehensive Risk Assessment
Begin by thoroughly assessing the risks and vulnerabilities specific to your organization. This will inform the appropriate level of security measures and help prioritize the implementation of the guidelines. - Develop a Phased Implementation Plan
Implementing the guidelines is not a one-size-fits-all process. Develop a phased approach that considers the complexity of your systems, the sensitivity of the data being protected, and the resources available. - Engage Stakeholders and Provide Training
Effective implementation requires buy-in from all stakeholders, including executives, IT professionals, and end-users. Provide comprehensive training and awareness programs to ensure a smooth transition and foster a culture of security awareness. - Continuously Monitor and Adjust
Cybersecurity is an ever-evolving field, and threats are constantly emerging. Continuously monitor the effectiveness of your password security practices and be prepared to adjust and adapt as necessary.
NIST CSF overview and guides
This NIST CSF guide explains the framework’s components, implementation steps, best practices, common challenges, and maturity model.
Common misconceptions about password security
Despite the widespread awareness of the importance of password security, several misconceptions continue to persist.
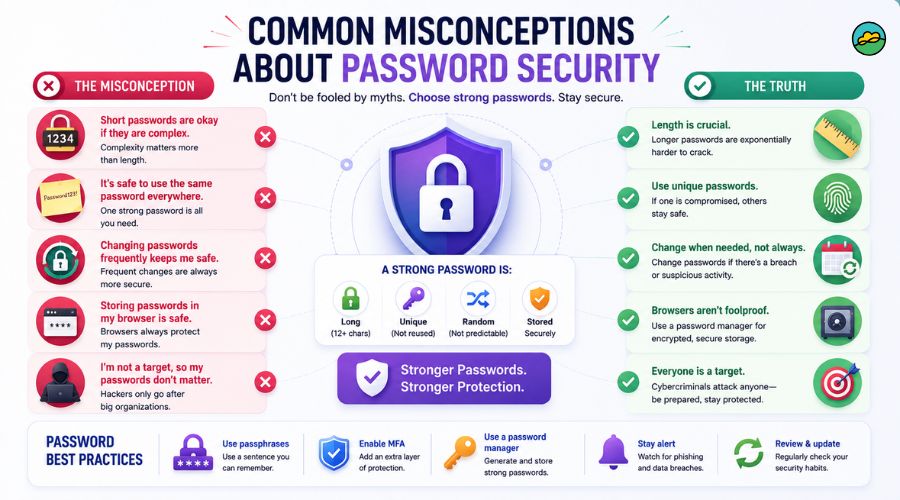
Addressing these misconceptions is crucial for effective implementation of the NIST Password Guidelines 2026:
- Longer Passwords Are Always Better
While longer passwords are generally more secure, the guidelines emphasize the importance of password complexity and unpredictability over sheer length. A well-crafted passphrase can be more effective than a long, but predictable, password. - Password Expiration Policies Enhance Security
Traditional password expiration policies, which require users to change their passwords at regular intervals, have been found to be largely ineffective and can even encourage insecure practices. The guidelines recommend moving away from arbitrary expiration policies and focusing on other security measures. - Passwords Should Be Frequently Changed
Unless there is a specific reason to believe a password has been compromised, frequent password changes can lead to user frustration and potentially weaker passwords. The guidelines advise against mandatory periodic password changes in favor of more targeted approaches.
Best practices for password management
Implementing the NIST Password Guidelines 2026 is not just about adhering to a set of rules; it’s about cultivating a culture of password security within your organization. Policies alone rarely change behavior; lasting protection comes when secure habits are woven into daily workflows, supported by the right tools, and reinforced by leadership.
The guidelines mark a shift away from outdated practices like forced complexity and frequent resets toward approaches grounded in how people actually behave. Organizations that embrace this shift reduce breach risk while easing friction for users. The following best practices will help you translate the guidelines into everyday reality.
- Encourage the use of passphrases
Passphrases, longer, memorable combinations of words, are often more secure than traditional complex passwords while being far easier for users to recall. A phrase like four random words can offer greater entropy than a short string of symbols and numbers. Encourage employees to favor length over complexity, and set generous maximum length limits so passphrases are never artificially truncated by your systems. - Implement multi-factor authentication (MFA)
MFA adds an extra layer of security by requiring users to provide additional forms of authentication beyond just a password, such as an authenticator app, hardware token, or biometric check. Even if credentials are stolen or phished, attackers cannot proceed without the second factor. Prioritize phishing-resistant methods where possible, and roll MFA out first on email, VPN, and administrative accounts. - Screen passwords against known-breach lists
NIST recommends checking new passwords against lists of commonly used, expected, or previously compromised credentials. Blocking these weak choices at creation prevents attackers from succeeding with credential-stuffing and dictionary attacks. Integrate automated screening into your identity systems so users receive immediate, helpful feedback, and rescreen existing passwords periodically as new breach data becomes available to close emerging exposure gaps. - Eliminate arbitrary password expiration
Forcing users to change passwords on a fixed schedule encourages predictable, incremental variations that weaken security rather than strengthen it. Under the 2026 guidance, passwords should be changed only when there is evidence of compromise. This approach reduces user fatigue, cuts helpdesk reset tickets, and focuses attention where it matters: rapid, mandatory resets the moment a credential is suspected stolen. - Regularly audit and monitor password practices
Conduct regular audits and continuous monitoring to identify potential vulnerabilities and verify compliance with the guidelines. Review authentication logs for anomalies, test password storage mechanisms, and confirm hashing standards are current. This proactive approach helps you stay ahead of emerging threats, demonstrates due diligence to auditors, and surfaces policy drift before it becomes an exploitable weakness in your environment. - Foster a culture of security awareness
Educate and train employees on the importance of password security and the real-world consequences of poor practices, from account takeover to organizational breach. Use engaging, role-based training rather than annual checkbox exercises, and provide approved password managers to make secure behavior effortless. Encourage a culture of accountability where reporting a suspected compromise is praised, never punished.
Strong password management is ultimately a continuous commitment, not a one-time project. By combining passphrases, MFA, breach screening, sensible expiration policies, vigilant monitoring, and an informed workforce, organizations can align with the NIST Password Guidelines 2026 while genuinely reducing risk. Start with the practices that close your biggest gaps, measure progress, and refine as threats evolve. When security becomes second nature to every employee, passwords transform from your weakest link into a dependable first line of defense.
Why password security now depends on more than passwords
Modern cyberattacks have evolved far beyond simple password guessing, making it increasingly important for organizations to adopt a layered approach to authentication. While the latest NIST password guidelines emphasize longer passphrases, screening against compromised passwords, and eliminating unnecessary password changes, they also recognize that passwords alone cannot fully protect user accounts.
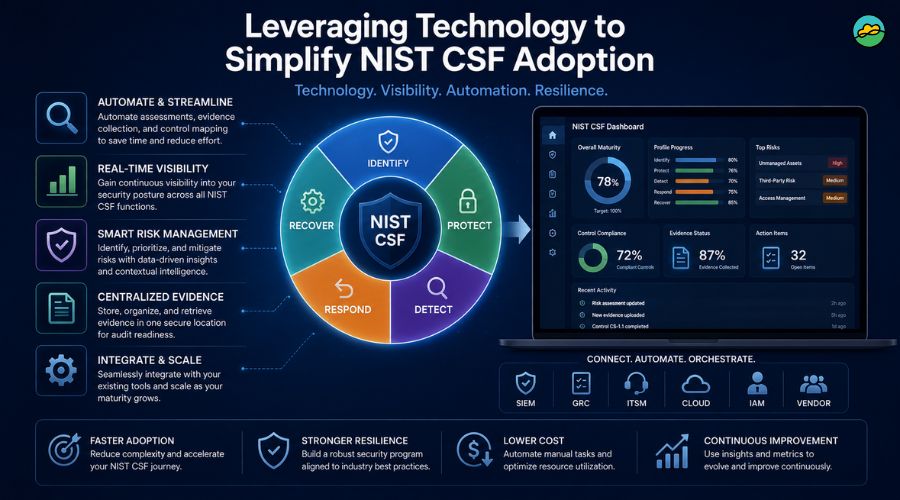
Attackers frequently use phishing campaigns, credential stuffing attacks, and social engineering tactics to bypass traditional password defenses. As a result, organizations are increasingly combining strong password practices with multifactor authentication (MFA), password managers, and identity verification technologies. These additional safeguards help reduce the likelihood of unauthorized access even if credentials are compromised.
By treating passwords as one component of a broader identity security strategy, businesses can better protect sensitive information, reduce account takeover risks, and improve overall cybersecurity resilience. This shift reflects a growing understanding that effective authentication requires multiple layers of protection working together.
The adoption of phishing-resistant authentication methods is expected to play an even greater role in the future of password security. Technologies such as passkeys, biometric authentication, and hardware security keys are gaining traction because they reduce reliance on traditional passwords while improving user experience. These methods align with NIST’s broader goal of strengthening authentication without creating unnecessary friction for users. Organizations that embrace modern identity and access management practices can improve security while minimizing the risks associated with password reuse, weak credentials, and human error.
Additionally, integrating authentication controls with centralized monitoring and access governance solutions enables security teams to detect suspicious login activity and respond more quickly to potential threats. As cybercriminals continue to refine their attack techniques, businesses that combine NIST password guidelines with modern authentication technologies will be better positioned to protect users, maintain compliance, and support long-term security objectives in an increasingly complex digital environment.
Read our NIST password guidelines 2026: 15 rules to follow article to learn more!
Tools and resources for password security
Implementing the NIST Password Guidelines 2026 can be a daunting task, but fortunately, there are numerous tools and resources available to assist you in this process:
- Password Managers
Reputable password managers such as LastPass, 1Password, and KeePass can help users generate, store, and retrieve strong, unique passwords securely. - Password Strength Checkers
Online tools like zxcvbn and Password Strength Checker can evaluate the strength of your passwords and provide recommendations for improvement. - NIST Resources
NIST itself offers a wealth of resources, including detailed guidelines, best practice documents, and educational materials, to support organizations in implementing their recommendations. - Cybersecurity Frameworks
Established cybersecurity frameworks, such as the NIST Cybersecurity Framework and the ISO/IEC 27001 standard, can provide guidance on integrating password security best practices into your overall security strategy.
The future of password security
While passwords have been a staple of authentication for decades, the future of password security is likely to evolve rapidly. As technology advances, new authentication methods and paradigms will emerge, offering more secure and user-friendly alternatives. The NIST Password Guidelines 2026 are a stepping stone towards this future, paving the way for a more robust and holistic approach to cybersecurity.
Potential future developments in password security include:
- Biometric authentication
The use of biometric identifiers, such as fingerprints, facial recognition, and iris scans, could become more prevalent, offering a more secure and convenient alternative to traditional passwords. - Continuous Authentication
Instead of a one-time authentication process, continuous authentication methods could monitor user behavior and activity patterns, providing ongoing verification and reducing the risk of unauthorized access. - Quantum-Resistant Cryptography
As quantum computing technology advances, new cryptographic algorithms and protocols will be needed to protect against quantum-based attacks. The future of password security will likely incorporate quantum-resistant cryptography to ensure the integrity of sensitive data. - Decentralized Identity Management
Decentralized identity management systems, built on blockchain technology or other distributed ledgers, could provide a more secure and privacy-preserving approach to identity verification and authentication.
Turning NIST rules into everyday habits your team can keep
NIST’s latest password guidance only works if people can actually live with it day to day. That means translating the standards into simple, repeatable habits: use a password manager, choose long passphrases you can remember without writing them down, and stop reusing passwords across tools and personal accounts. For most teams, the biggest win is normalizing “one strong, unique login per service plus MFA,” instead of chasing obscure character rules. When you explain that this approach is both more secure and less frustrating, adoption stops feeling like another IT mandate and starts to feel like basic self‑defense.
The back end matters just as much as end‑user behavior. Following NIST guidance means screening new passwords against known‑breach lists, enforcing minimum length, and storing credentials using strong hashing and salting, not plain text or weak legacy algorithms. Security teams should also review how password policies interact with account lockout rules, rate limiting, and MFA, so legitimate users are not punished more than attackers. By quietly upgrading the plumbing while simplifying what you ask of users, you get the best of both worlds: fewer compromised accounts and fewer support tickets about confusing password requirements
Summing it up
The NIST Password Guidelines 2026 represent a significant step forward in the ongoing quest for robust password security. By embracing these guidelines and fostering a culture of security awareness, you can better protect your organization against the ever-evolving threats posed by malicious actors.
Remember, password security is not a one-time effort but an ongoing journey. Stay vigilant, continuously monitor and adapt your practices, and embrace the latest advancements in authentication technologies. With a proactive and comprehensive approach, you can unlock the future of cybersecurity and safeguard your digital assets for years to come.
Elevate your organization’s password security practices with our comprehensive NIST Password Guidelines 2026 implementation services. Our team of cybersecurity experts will guide you through the entire process, from risk assessment to policy development and training. Don’t wait until it’s too late; protect your sensitive data today. Contact us for a free consultation and take the first step towards unlocking the future of password security.
FAQs
What are the key changes introduced in the NIST Password Guidelines 2026?
The NIST Password Guidelines 2026 emphasize a move away from traditional password-centric security towards more advanced methods. Key updates include a strong focus on passwordless authentication technologies (like biometrics and hardware keys), adaptive password policies that tailor security measures to the specific risk profiles of organizations, continuous monitoring and evaluation of password security practices, and the integration of reputable password managers into organizational security policies.
Why are password guidelines important for organizations?
Password guidelines are crucial because passwords often serve as the first line of defense against unauthorized access. Weak passwords can render even the most sophisticated security measures ineffective. Adhering to robust guidelines reduces the risk of data breaches, protects sensitive information, and helps organizations strengthen their overall digital defenses.
How has the NIST approach to passwords changed over time?
Initially, NIST guidelines favored complex passwords with a mix of uppercase and lowercase letters, numbers, and special characters. However, this approach often led to user frustration and predictable patterns. The 2017 updates shifted to longer passphrases that are easier to remember but more difficult to crack. They also discouraged frequent mandatory password changes and the use of security questions due to their inherent vulnerabilities. The 2025 update continues this trend, moving towards more sophisticated authentication methods.