

On this page
ToggleOverview
This article explains California’s Consumer Privacy Act (CCPA), detailing the five core consumer rights: the right to know, delete, opt-out of sales, non-discrimination, and to know about data sharing. It provides practical implementation steps for businesses to achieve CCPA compliance, including establishing verification processes, transparent data practices, and user-friendly opt-out mechanisms.
It addresses challenges like adapting to regulatory changes and integrating global privacy standards. It also promotes a platform, TrustCloud, which offers resources and training related to GRC (governance, risk, and compliance), including CCPA compliance.
What are onsumer rights under CCPA?
The California Consumer Privacy Act (CCPA), enacted in 2020, stands as pivotal legislation designed to empower individuals with greater control over their personal data. At the core of CCPA are various consumer rights that afford Californians the ability to know, access, and control how their personal information is collected and processed by businesses.
In this comprehensive guide, we delve into the intricacies of consumer rights under the CCPA, providing a detailed understanding of each right and offering practical insights for businesses to implement effective compliance measures.
Read our Heightened Regulatory Scrutiny: How to Meet Compliance Demands article to learn more.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MoreUnderstanding the core consumer rights
Understanding core consumer rights is essential for protecting individuals in the marketplace. These rights, often outlined by governments and consumer protection agencies, include the right to safety, ensuring that products and services are free from harm; the right to be informed, granting consumers access to accurate product information; the right to choose, allowing for fair competition and selection; the right to be heard, ensuring consumer concerns are addressed; and the right to redress, offering solutions for defective products or services.
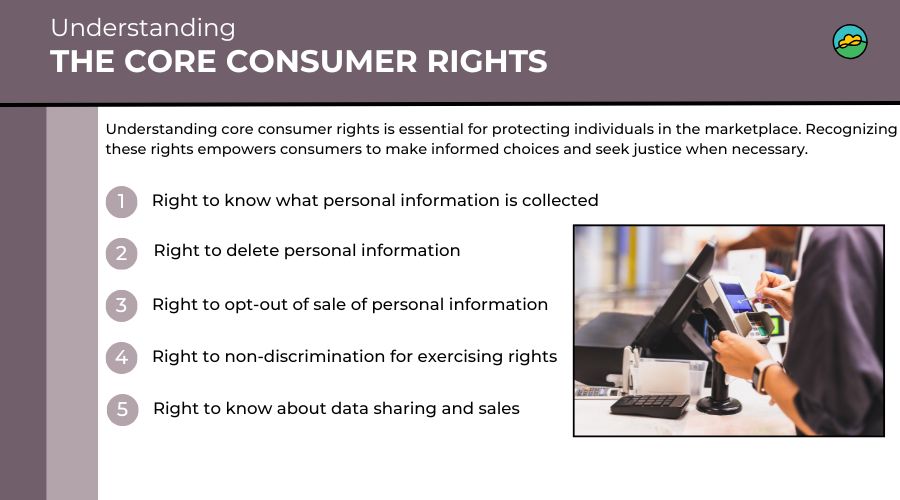
Recognizing these rights empowers consumers to make informed choices and seek justice when necessary.
- Right to know what personal information is collected
The CCPA grants consumers the right to request information about the categories and specific pieces of personal information that a business has collected about them.- Businesses should maintain detailed records of the types of personal information collected.
- Establish clear procedures for responding to consumer requests for information.
- Right to delete personal information
Consumers have the right to request the deletion of their personal information held by businesses, with certain exceptions.- Develop a process for verifying and responding to deletion requests promptly.
- Ensure that third-party service providers are also informed and compliant with deletion requests.
- Right to opt-out of sale of personal information
CCPA gives consumers the right to opt-out of the sale of their personal information. Businesses must provide a clear and accessible “Do Not Sell My Personal Information” link on their websites.- Implement user-friendly mechanisms for opting out of data sales.
- Regularly update opt-out lists and ensure third-party partners are compliant.
- Right to non-discrimination for exercising rights
Consumers have the right not to be discriminated against for exercising their rights under CCPA, including denial of goods or services, charging different prices, or providing a different level of quality.- Establish policies and practices that treat all consumers equally, regardless of their exercise of privacy rights.
- Educate customer-facing staff on non-discrimination policies.
- Right to know about data sharing and sales
Businesses must disclose to consumers the categories of personal information collected, the sources of information, the purposes of collection, and whether the information is sold or disclosed for business purposes.- Regularly update privacy notices to include comprehensive information about data sharing and sales practices.
- Provide accessible and clear information to consumers about data practices.
The role of SLA compliance and consumer rights under CCPA
As data privacy laws like the California Consumer Privacy Act (CCPA) continue to shape how businesses handle consumer data, SLA compliance has become essential, especially when working with third-party vendors. With CCPA giving consumers new rights over their personal data, businesses need to ensure that these rights are upheld, and SLAs play a crucial role in making that happen.
Ensuring vendor responsibility through SLA compliance
SLA compliance is key to holding third-party vendors accountable for their handling of personal data. By incorporating specific CCPA-related clauses into SLAs, businesses can ensure that vendors meet requirements such as providing consumers with access to their data, honoring requests for data deletion, and offering opt-out options for the sale of personal data.
Protecting consumer rights under CCPA
The CCPA gives consumers rights like access to their data, the ability to delete their data, and the option to opt-out of data sharing for marketing purposes. SLA compliance ensures that vendors are not only aware of these rights but are also legally bound to support them. This helps businesses protect consumers and avoid potential fines or legal challenges.
How SLA compliance supports your CCPA efforts
- Clear data protection responsibilities:
SLAs can outline the security measures vendors must follow to protect personal data. - Defined timelines:
SLAs help set timelines for responding to consumer requests, like data access or deletion, which is a key part of CCPA compliance. - Accountability:
By specifying penalties for non-compliance, SLAs ensure that vendors take their data protection responsibilities seriously.
With the growing importance of consumer rights under the CCPA, SLA compliance has become a foundational element in managing third-party relationships. By setting clear expectations and ensuring that vendors are legally bound to protect consumer data, SLAs help businesses uphold the privacy rights that consumers value most.
Read our The Future of SLAs: Are We Measuring What Matters? article to learn more!
Practical implementation of CCPA consumer rights compliance
Practical implementation of CCPA consumer rights compliance involves several key steps to protect consumer data. Businesses must ensure that they provide clear, accessible privacy notices, informing consumers of their rights. They must implement mechanisms to allow consumers to request access to their personal data, delete it, or opt out of its sale.
SLA compliance plays a crucial role in the practical implementation of CCPA consumer rights compliance by ensuring that third-party vendors adhere to the requirements of the law. By outlining clear responsibilities within service level agreements, businesses can hold vendors accountable for actions like providing data access, honoring deletion requests, and facilitating opt-out options.
This ensures that consumer rights are not only protected but also efficiently implemented in real time, helping businesses stay compliant and avoid potential penalties while building trust with their customers.
Additionally, companies should ensure robust data security measures to prevent breaches and train staff on handling consumer requests in compliance with CCPA guidelines. Regular audits and updates to privacy policies help maintain ongoing compliance and protect against potential legal and financial penalties.
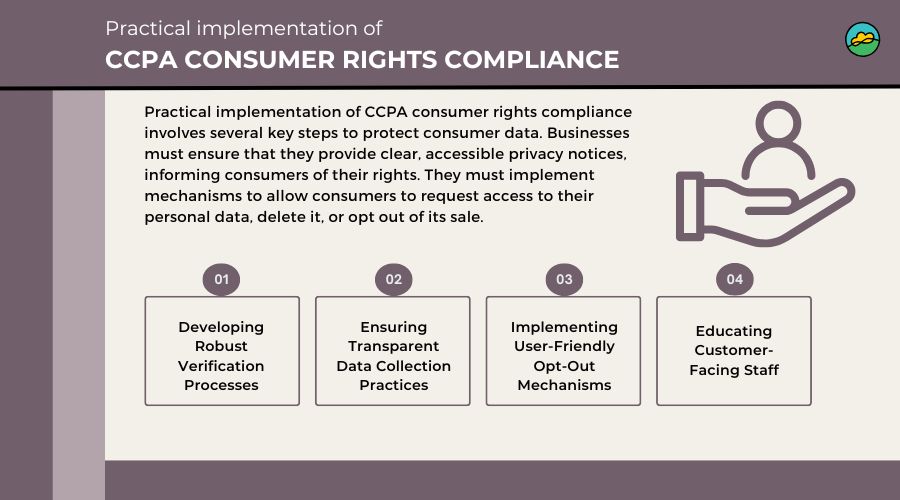
- Developing Robust Verification Processes
- Establish secure methods for verifying the identity of consumers making requests.
- Implement multi-step verification processes to prevent unauthorized access to personal information.
- Ensuring Transparent Data Collection Practices
- Clearly communicate to consumers the types of personal information collected and the purposes for which it is used.
- Update privacy policies to reflect accurate and detailed information about data collection practices.
- Implementing User-Friendly Opt-Out Mechanisms
- Integrate a prominent and easily accessible “Do Not Sell My Personal Information” link on websites.
- Regularly test and optimize the opt-out process to ensure simplicity and effectiveness.
- Educating Customer-Facing Staff
- Provide comprehensive training to customer service representatives on handling consumer rights inquiries.
- Develop a knowledge base for staff to access up-to-date information about consumer rights and compliance procedures.
Prepare to pass your CCPA audit with TrustCloud! Your one stop solution for regulatory compliance assurance by TrustCloud exploring the evolving landscape of security and GRC.
Challenges and future considerations
- Adapting to regulatory changes and CPRA (CCPA 2.0)
- Stay informed about amendments to the CCPA, including the California Privacy Rights Act (CPRA), and adapt compliance measures accordingly.
- Anticipate potential expansions of consumer rights and adjust internal processes accordingly.
- Global privacy standards and cross-border considerations
- Align CCPA compliance efforts with evolving global privacy standards to prepare for potential cross-border implications.
- Develop strategies for handling data transfers and ensuring compliance with international privacy regulations.
- Technological advancements and privacy by design
- Embrace privacy-by-design principles, integrating data protection measures into technological systems from the outset.
- Explore emerging technologies, such as privacy-enhancing tools, to enhance consumer rights protection.
As consumer awareness and expectations regarding data privacy continue to rise, businesses must proactively adapt to the evolving landscape of regulations like CCPA. Understanding and implementing compliance measures related to consumer rights not only ensures legal adherence but also fosters trust and loyalty among consumers. By prioritizing transparency, establishing robust verification processes, and staying abreast of regulatory changes, businesses can navigate the complexities of CCPA and contribute to a privacy-centric digital ecosystem. As the CCPA evolves and potentially sets the stage for future privacy legislation, businesses that prioritize consumer rights protection will be better positioned to thrive in the era of data-conscious consumers.
Prove to customers that you take privacy seriously
Adopt and maintain compliance with GDPR, CCPA, PCI and ISO 27701 so you can show customers and prospects that you’re serious about privacy. TrustCloud helps you achieve and maintain regulatory compliance with confidence as you grow.
Ready to build trust with your customers?
Turning CCPA rights into a trust-building experience
For many teams, CCPA starts as a checklist of obligations, privacy notices, request forms, and opt-out links, but its real power shows up in how you design the experience around those rights. When consumers can easily find out what data you hold, update their preferences, or delete information without jumping through hoops, they feel respected rather than scrutinized.
That means building clear, human language into your interfaces, using plain explanations instead of legal jargon, and giving people real-time feedback on the status of their requests. Treat every access or deletion request as a micro-moment to demonstrate reliability: confirm receipt quickly, set expectations on timelines, and close the loop when the request is complete. Done well, your CCPA workflows become less about avoiding complaints and more about signaling that privacy is part of your brand promise.
You can take this further by turning CCPA touchpoints into proactive education moments, not just transactional interactions. When someone submits a request, provide short, contextual guidance on what each right means, how you secure their data, and what tradeoffs might come with certain choices (for example, fewer personalized recommendations if they limit data use).
Internally, route these events into your GRC tooling so they feed dashboards, audits, and continuous improvement: which rights are exercised most often, where do users get stuck, which business units see the most requests, and how often are deadlines missed? Those patterns highlight where processes need refinement, where additional training is required, or where product changes could reduce friction. Over time, this data-driven loop helps you evolve from “CCPA-compliant” to “privacy-forward,” an organization that treats consumer rights not as a legal minimum but as a strategic lever for loyalty and differentiation.
Elevating CCPA rights into a premium privacy experience
CCPA isn’t just a checklist of consumer rights; it’s a powerful opportunity to design a trust-building experience into every touchpoint you have with your customers. When you translate the law’s abstract rights into clear, guided journeys (“see what we know about you,” “adjust how we use your data,” “clean up my data trail”), you signal respect and maturity in how you handle personal information.
Instead of treating access, deletion, or opt-out requests as operational burdens, you can frame them as value-added experiences that differentiate your brand. Done well, CCPA compliance becomes a core part of your customer experience strategy, not a legal afterthought.
- Design a simple, branded privacy center that centralizes all CCPA rights (access, deletion, opt-out, correction), using step-by-step flows and progress indicators so people always know where they are in the process and what happens next.
- Replace dense privacy text with layered explanations, short, friendly summaries up front and deeper legal details on demand, so customers can understand their rights at a glance yet still drill down when they want specifics.
- Treat identity verification as part of the experience: explain clearly why you’re asking for certain details, how long they’re retained, and how they’re protected, so the verification step feels safe, not intrusive or suspicious.
- Build proactive status updates into your workflows, emails or in-app notifications that confirm a request, explain expected timelines, and summarize the outcome, so customers never feel like their request disappeared into a black hole.
- Use request data (in aggregated, anonymized form) to spot friction: which rights are used most, where users drop off, and what questions continue to recur, then feed those insights back into UX, documentation, and training.
- Train frontline teams, support, sales, and success on how to talk about CCPA rights confidently and empathetically, turning compliance interactions into moments of reassurance rather than awkward, hand-off-heavy conversations.
When you intentionally design the end-to-end journey around CCPA rights, you flip the script from “I’m forced to share this because of a law” to “I want to share this because it proves we take your privacy seriously.” Customers begin to see your organization as a careful steward of their data, not just a collector of it. Over time, these micro-interactions compound into a durable trust advantage that’s hard for competitors to copy, because it’s embedded in how you operate, not just in what your policy pages say.
Summing it up
CCPA gives consumers real leverage over how their personal data is collected, used, and shared, and that power is reshaping what “good” looks like in customer relationships. When you move beyond bare-minimum compliance and design clear, respectful, and responsive experiences around access, deletion, correction, and opt-out, you turn legal rights into a living expression of your brand values. The organizations that will win in this landscape are the ones that treat privacy as a product feature and trust as a measurable outcome. If you can make exercising CCPA rights feel effortless and empowering, you’re not just avoiding penalties; you’re building loyalty.
FAQs
What is the primary purpose of the California Consumer Privacy Act (CCPA)?
The CCPA is a landmark piece of legislation designed to give California residents more control over their personal data. It empowers individuals with the rights to know what personal information is being collected about them, access that information, and control how businesses use and share it.
Essentially, it aims to make data practices more transparent and give consumers greater agency over their own data.
What are the main rights granted to consumers under the CCPA?
The CCPA provides several key rights to consumers. These include: the right to know what personal information a business collects, the right to request deletion of their personal information, the right to opt-out of the sale of their personal information, the right to non-discrimination for exercising their CCPA rights, and the right to know about data sharing and sales practices.
What does the "right to know" entail under the CCPA?
The “right to know” means that consumers can request information about the specific categories and pieces of personal information that a business has collected about them. Businesses must keep detailed records of the personal data they collect, and provide this information to consumers upon request.
What does it mean for a consumer to have the "right to opt-out of the sale of personal information," and how should businesses facilitate this?
The “right to opt-out of the sale of personal information” allows consumers to prevent businesses from selling their data to third parties. Businesses must provide a clear and accessible “Do Not Sell My Personal Information” link on their website. They must also have mechanisms in place to respect consumers’ opt-out choices, updating lists and ensuring third-party partners are also compliant.
How does the CCPA protect consumers from discrimination when they exercise their rights?
The CCPA prohibits businesses from discriminating against consumers who choose to exercise their rights under the act. This means that a business cannot deny goods or services, charge different prices, or provide a different level of quality to consumers who have exercised their CCPA rights. Companies must treat all consumers equally, regardless of whether they request to view their data or opt-out of data sales.
What are some key steps a business should take to ensure compliance with the CCPA?
To comply with CCPA, businesses should first and foremost ensure they have a clear, easily accessible privacy policy. They must implement methods for consumers to request access to or delete their data or opt out of its sale.
Businesses must also train staff on how to handle these requests and implement strong data security to protect against data breaches. Finally, regular audits and updates to privacy policies are necessary to maintain ongoing compliance.