

On this page
ToggleOverview
Organizations across industries are constantly challenged to protect their sensitive information and manage potential risks effectively. CSF certification, short for Cybersecurity Framework certification, has emerged as a significant marker of an organization’s readiness to face cybersecurity challenges while ensuring compliance with industry standards.
In this article, we explain what CSF certification is, examine its origins and benefits, and offer insights into how organizations can achieve and maintain this critical certification.
The concept of a cybersecurity framework is built upon a structured set of guidelines designed to manage cybersecurity risk in an enterprise. These frameworks typically encompass best practices, standards, and guidelines that tailor security practices to the specific needs and operations of an organization.
By tailoring these best practices and ensuring compliance with industry regulations, CSF certification helps companies proactively manage information security risks and respond quickly and efficiently to evolving threats.
The foundation: Cybersecurity Framework (CSF)
Before delving into the certification, it’s essential to understand the Cybersecurity Framework itself. The NIST Cybersecurity Framework was introduced to help organizations, both in the public and private sectors, manage and reduce cybersecurity risk. It provides a structured approach to improving an organization’s cybersecurity posture by focusing on five key functions: identify, protect, detect, respond, and recover. These functions work together to create a comprehensive and adaptive approach to cybersecurity.
What is CSF certification?
CSF certification is a recognition awarded to organizations that have successfully implemented the NIST Cybersecurity Framework. It signifies that an organization has demonstrated a strong commitment to cybersecurity and a comprehensive approach to managing and reducing cybersecurity risk. While the NIST Cybersecurity Framework itself is a voluntary set of guidelines and best practices, CSF certification is a formal acknowledgment of an organization’s adherence to these guidelines.
CSF certification is not a pass-or-fail assessment; instead, it’s a process that evaluates how well an organization has implemented the NIST framework’s functions and categories. Achieving CSF certification requires an in-depth assessment, documentation of cybersecurity policies and practices, and a commitment to continuous improvement.
The origins and evolution of CSF certification
CSF certification did not appear out of nowhere. Instead, it evolved as organizations worldwide recognized that safeguarding digital assets and customer data could no longer be taken lightly. The evolution of CSF certification has roots in various regulatory and industry-specific frameworks.
Many organizations first implemented guidelines provided by bodies such as the National Institute of Standards and Technology (NIST) and the International Organization for Standardization (ISO). As threats evolved, the concept of CSF certification expanded, offering businesses a robust, comprehensive guideline that composers best practices from several leading frameworks into a single, harmonized approach.
Initially, early adopters of these practices were predominantly from the financial and healthcare sectors, given the sensitive nature of their data. Today, however, CSF certification is embraced by a diverse array of companies, including tech firms, manufacturers, government bodies, and service providers. Each organization that adopts the CSF framework customizes it to align with its risk profile, threat landscape, operational complexity, and regulatory obligations.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MoreThe components of CSF certification
In an age where cyber threats loom large and data security is non-negotiable, organizations across various sectors are on a quest to fortify their cybersecurity defenses. CSF is more than a mere guideline; it’s a roadmap to bolster an organization’s resilience against cyber threats.
To navigate this landscape effectively and earn CSF certification, it’s imperative to understand the components that make up this rigorous process. We’ll unravel the key elements, from self-assessment to continuous improvement, and delve into why CSF certification is a linchpin in today’s cybersecurity landscape. Join us on this journey to comprehend the significance of each component and how they collectively contribute to a robust cybersecurity posture, one that shields organizations from the ever-evolving challenges of the digital age.
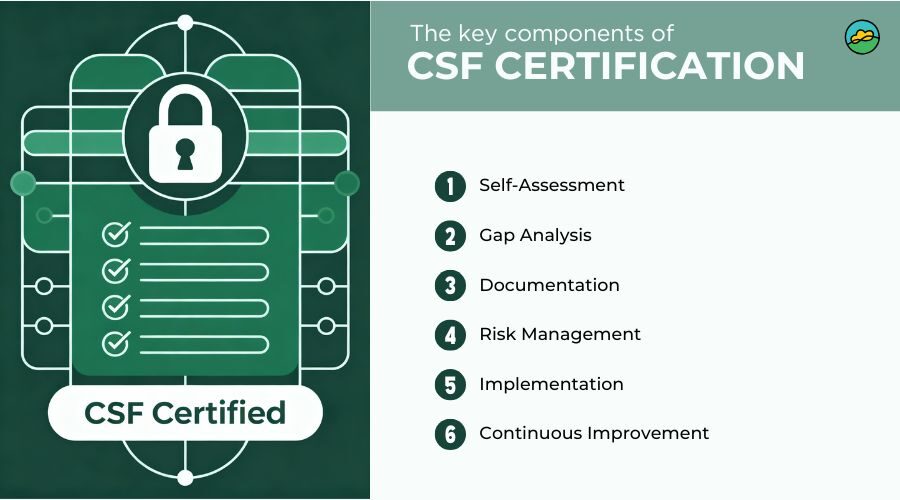
CSF certification involves several key components, each contributing to a thorough evaluation of an organization’s cybersecurity readiness. These components include:
- Self-Assessment
The process typically begins with a self-assessment, where an organization evaluates its cybersecurity practices against the NIST Cybersecurity Framework. This self-assessment provides a baseline understanding of the organization’s current cybersecurity posture. - Gap Analysis
After the self-assessment, a gap analysis is conducted to identify areas where the organization’s current practices may not align with the NIST framework. This analysis highlights the specific areas that need improvement to meet the framework’s guidelines. - Documentation
One of the critical elements of CSF certification is thorough documentation. This includes creating policies, procedures, and records that detail the organization’s cybersecurity practices and how they align with the NIST framework. Documentation is essential for both the certification process and ongoing compliance. - Risk Management
An integral part of CSF certification is risk management. Organizations are required to identify and assess cybersecurity risks, develop risk management plans, and put measures in place to mitigate those risks. This proactive approach to risk management is a fundamental aspect of the NIST framework. - Implementation
CSF certification assesses how well an organization has implemented the NIST framework’s functions and categories. This includes the extent to which cybersecurity measures are integrated into the organization’s operations and processes. - Continuous Improvement
CSF certification is not a one-time achievement but an ongoing commitment. Organizations are expected to continuously monitor and improve their cybersecurity practices based on the NIST framework’s principles. This involves regular evaluations, adjustments, and updates to adapt to changing threats and technologies.
Read our Integrating cybersecurity with GRC: strategies for a unified defense approach to learn more!
The importance of CSF certification in strengthening the NIST CSF framework
The NIST Cybersecurity Framework (NIST CSF) provides a robust structure for organizations to identify, protect, detect, respond to, and recover from cybersecurity threats. Achieving CSF certification validates an organization’s adherence to this framework, enhancing its overall cybersecurity posture. Below are the key ways CSF certification strengthens the NIST CSF implementation in an organization:
- Validates Framework Implementation
CSF certification ensures that the organization has effectively implemented the NIST CSF principles. This validation reassures stakeholders that the organization is committed to a robust cybersecurity approach, covering critical areas like:- Risk assessment and mitigation strategies.
- Controls for protecting sensitive data.
- Enhances Risk Management
It emphasizes a risk-based approach to cybersecurity. This systematic approach bolsters the organization’s ability to address risks proactively. CSF certification strengthens this by:- Providing structured audits to identify vulnerabilities.
- Requiring ongoing risk assessments to adapt to emerging threats.
- Demonstrates Regulatory Compliance
Many industries require compliance with regulations aligned with NIST CSF, such as HIPAA, GDPR, and CCPA. By aligning with regulatory requirements, the certification supports both legal and operational integrity. CSF certification:- Serves as proof of adherence to these standards.
- Reduces the risk of non-compliance penalties.
- Builds Stakeholder Confidence
CSF certification is a trusted indicator of cybersecurity maturity. This confidence is crucial for maintaining market competitiveness.It:- Demonstrates to customers, partners, and investors that the organization prioritizes security.
- Strengthens relationships with stakeholders by building trust in the organization’s cybersecurity capabilities.
- Facilitates Continuous Improvement
The certification process includes periodic assessments and audits. Continuous improvement ensures that the framework remains relevant and effective. This reinforces the NIST CSF by:- Encouraging organizations to regularly update their cybersecurity measures.
- Ensuring alignment with evolving standards and technologies.
- Improves Incident Response and Recovery
The NIST CSF emphasizes the importance of incident response and recovery. This readyness enhances the organization’s ability to recover quickly, minimizing the impact of cyber incidents. Certification ensures:- Well-documented response plans are in place.
- Incident response teams are trained and ready to act.
- Supports Cyber Resilience
Cyber resilience is a key outcome of a strong implementation. This makes the organization more adaptable and robust in the face of threats. CSF certification contributes to this by:- Strengthening the organization’s defenses against cyberattacks.
- Ensuring systems are designed to recover and maintain critical operations during disruptions.
- Promotes Alignment Across Teams
Achieving CSF certification requires cross-functional collaboration, promoting alignment among IT, operations, legal, and executive teams. Collaborative efforts improve the overall implementation and effectiveness of the framework. This alignment ensures:- Consistent application of NIST CSF principles across the organization.
- Streamlined communication and coordination during security initiatives.
- Attracts New Business Opportunities
For industries like healthcare, finance, and government contracting, CSF certification is often a prerequisite. This certification thus enhances business opportunities while reinforcing theframework. Organizations with certification can:- Qualify for high-value contracts.
- Differentiate themselves from competitors.
CSF certification plays a critical role in strengthening an organization’s adherence to the framework. It validates the implementation of cybersecurity best practices, enhances risk management, ensures regulatory compliance, and builds stakeholder trust. By promoting continuous improvement and supporting cyber resilience, CSF certification enables organizations to effectively navigate the evolving threat landscape and maintain secure, reliable operations.
Prove how your security program protects your business and drives growth
Showcase financial liability reduction with IT risk quantification, cut costs while automating 100s of manual security and GRC workflows, and accelerate revenue by earning regulator, auditor and customer trust.
The significance of CSF certification
Pursuing CSF certification represents more than meeting a cybersecurity benchmark; it reflects a strategic commitment to protecting digital ecosystems and building long-term resilience. As cyber risks grow more sophisticated, organizations are under pressure to strengthen their security posture, demonstrate accountability, and protect sensitive data. CSF certification provides a structured way to assess and improve cybersecurity maturity while aligning security priorities with business goals. It acts as a differentiator in the market, signaling reliability and preparedness.
For organizations working with sensitive data, distributed systems, or regulated industries, CSF certification becomes a vital tool for maintaining trust, operational continuity, and compliance.
- Enhanced cybersecurity
CSF certification reinforces strong cybersecurity fundamentals by aligning practices with an established framework. It helps organizations improve controls across identity management, system protection, detection, and response. This structured approach reduces vulnerabilities, strengthens defenses, and ensures cybersecurity is consistently embedded into everyday operations and not treated as a one-time exercise. - Risk mitigation
A certified approach ensures risks are not only identified but also assessed, prioritized, and monitored. By understanding threats before they escalate, organizations reduce exposure to cyberattacks, operational disruption, and loss of sensitive data. This proactive stance leads to better preparedness and fewer incidents, supporting long-term business stability. - Regulatory compliance
CSF certification supports compliance with major regulations by aligning cybersecurity programs with industry expectations. Many regulators recognize the NIST CSF as a reputable framework, making certification beneficial for organizations handling personal data, protected health information, or financial assets. This alignment simplifies audits and supports continuous regulatory readiness. - Competitive advantage
When cybersecurity is a decision-making factor, CSF certification becomes a differentiator. It provides assurance to clients and partners that security controls are proven, evaluated, and maintained. This verification can strengthen vendor trust, accelerate contract approvals, and help organizations win business in competitive or highly regulated markets. - Improved incident response
CSF certification strengthens detection, response, and recovery processes by encouraging defined playbooks, monitoring tools, and escalation paths. With these capabilities in place, organizations can react quickly when suspicious activity or incidents occur. Faster containment reduces impact, limits downtime, and supports smooth recovery. - Enhanced reputation
Certification serves as evidence of a responsible cybersecurity posture. It demonstrates that protecting customer data and organizational assets is a top priority. This commitment builds confidence with stakeholders and reinforces brand credibility, especially in markets where security transparency influences purchasing and partnership decisions.
A CSF certification is more than a badge; it represents disciplined cybersecurity governance and a proactive security mindset. By adopting the framework and continually improving practices, organizations build a resilient foundation for growth, trust, and long-term digital safety.
Read the “Secure your digital assets successfully: Ultimate guide to cybersecurity controls” article to learn more!
Why opt for CSF certification?
Opting for CSF (Certified Scrum Foundation) certification can be highly beneficial for professionals in the field of project management and Agile development. This certification provides individuals with a comprehensive understanding of the Scrum framework and its principles, enabling them to effectively implement Agile methodologies in their projects. CSF certification validates the knowledge and skills required to successfully lead Agile teams and deliver high-quality products.
Moreover, it enhances career prospects by adding credibility and increasing the chances of securing better job opportunities. CSF certification also demonstrates a commitment to continuous learning and professional growth, which is highly valued in today’s competitive job market. Overall, opting for CSF certification is a strategic decision that can significantly boost an individual’s career in project management and Agile development.
While there is no specific certification labeled as “CSF certification,” organizations can opt to adopt and implement the NIST Cybersecurity Framework (CSF) and communicate their adherence to its principles. Here are five reasons why organizations may choose to adopt the NIST CSF:
- Comprehensive Risk Management
The NIST CSF provides a structured and comprehensive approach to managing cybersecurity risks. It helps organizations identify, assess, and prioritize cybersecurity risks based on their potential impact on business operations. This enables organizations to allocate resources effectively to address the most critical threats. - Adaptability to Business Needs
The CSF is designed to be adaptable to various organizational structures, sizes, and sectors. It allows organizations to customize their cybersecurity practices based on their specific business needs, risk tolerances, and regulatory requirements. This flexibility makes it a suitable framework for a wide range of industries. - Alignment with Industry Standards
The NIST CSF is widely recognized and respected in the cybersecurity community. It aligns with and complements other cybersecurity standards and frameworks, making it a valuable tool for organizations aiming to adhere to industry best practices. It can help organizations meet regulatory requirements and demonstrate compliance. - Enhanced Communication and Collaboration
The CSF provides a common language for discussing and managing cybersecurity risks within an organization. It facilitates improved communication and collaboration among different stakeholders, including IT professionals, management, and external partners. This shared understanding can contribute to more effective cybersecurity decision-making. - Continuous Improvement and Maturity
The CSF encourages a culture of continuous improvement in cybersecurity practices. Organizations adopting the CSF regularly assess and refine their cybersecurity processes, allowing them to adapt to emerging threats and technological changes. This focus on continuous improvement helps organizations mature their cybersecurity capabilities over time.
CSF certification is a valuable recognition that signifies an organization’s commitment to cybersecurity and its dedication to managing and reducing cybersecurity risks. It offers a structured approach to aligning an organization’s cybersecurity practices with industry best practices and regulatory requirements. As cyber threats continue to evolve, this certification can help organizations adapt, strengthen their security measures, and protect their sensitive information from potential breaches. It’s not just a certification; it’s a commitment to excellence in cybersecurity.
NIST CSF Overview and Guides
This guide explains the framework’s components, implementation steps, best practices, common challenges, and maturity model.
Implementing the NIST CSF in your organization
Implementing the NIST Cybersecurity Framework (CSF) in your organization is a strategic move to enhance cybersecurity resilience and manage risks effectively. The NIST CSF provides a flexible, scalable framework that organizations of all sizes and industries can tailor to their unique needs. The implementation process begins with understanding the framework\u2019s five core functions: Identify, Protect, Detect, Respond, and Recover. These functions guide organizations in assessing their current cybersecurity posture, identifying gaps, and setting clear goals for improvement.
Key steps include engaging stakeholders, mapping current processes to the framework, and prioritizing actions based on risk and business objectives. By using the NIST CSF, organizations can create a structured approach to cybersecurity, align with industry best practices, and enhance communication between technical teams and leadership. Ultimately, adopting the NIST CSF not only strengthens security but also builds trust with customers and partners by demonstrating a commitment to safeguarding sensitive information.
Implementing the NIST CSF in your organization requires a structured and comprehensive approach. Here are the key steps to consider:
- Establish a Cybersecurity Governance Structure
Appoint a dedicated team or individual responsible for overseeing your organization’s cybersecurity efforts, including the implementation of the NIST CSF. - Conduct a Gap Analysis
Assess your current cybersecurity practices and identify areas where your organization may fall short of the NIST CSF requirements. - Develop a Roadmap for Implementation
Create a detailed plan outlining the specific actions, timelines, and resources required to align your organization with the NIST CSF. - Deploy Cybersecurity Controls
Implement the necessary technical, administrative, and physical controls to protect your critical assets, in accordance with the NIST CSF guidelines. - Establish Continuous Monitoring and Improvement
Implement processes to regularly review and update your cybersecurity measures, addressing any emerging threats or vulnerabilities. - Train and Educate Your Employees
Ensure that your staff is well-versed in cybersecurity best practices and their roles in maintaining the organization’s overall security posture.
NIST CSF Certification vs other cybersecurity frameworks
While the NIST CSF is a widely recognized and respected cybersecurity framework, it is not the only option available to businesses. Other prominent frameworks, such as ISO 27001, COBIT, and HITRUST, also offer comprehensive approaches to managing cyber risks. The choice of framework may depend on your industry, regulatory requirements, and the specific needs of your organization.
One key distinction between the NIST CSF and other frameworks is its focus on risk management and its adaptability to various sectors and organization sizes. The NIST CSF is designed to be flexible and scalable, making it a suitable option for businesses of all sizes, from small enterprises to large corporations.
ISO 42001, NIST AI RMF
Develop, deploy, and manage your AI systems with ISO 42001 and NIST AI RMF to show your customers and prospects that as your technology advances, your GRC keeps pace.
Common challenges in achieving and maintaining CSF certification
Achieving CSF certification is a rewarding accomplishment, but the journey requires persistence, planning, and continuous improvement. Organizations often begin with enthusiasm, only to discover that aligning technology, processes, and culture with a cybersecurity framework takes time. Certification is not a one-time milestone; it requires sustained effort, measurement, and refinement. From modernizing outdated technology to shifting organizational attitudes toward security responsibility, each step introduces learning opportunities.
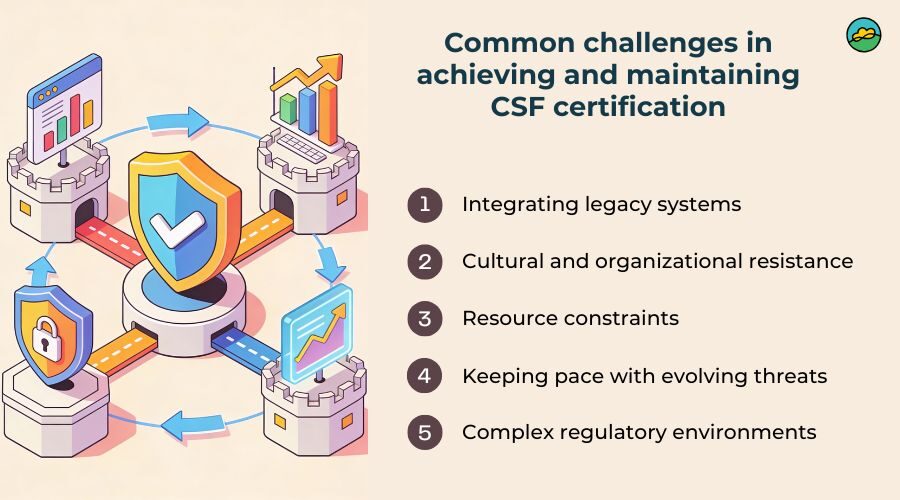
These challenges can feel overwhelming at first, but they ultimately strengthen the organization’s cybersecurity posture. By anticipating roadblocks early, businesses can build a more realistic roadmap and better position themselves for long-term success and CSF maintenance.
- Integrating legacy systems
Older systems often lack modern safeguards, making alignment with CSF requirements difficult. Replacing or reengineering outdated infrastructure without interrupting operations requires careful planning and phased implementation. Some organizations opt for hybrid environments or compensating controls during the transition period, ensuring security improvements can progress without jeopardizing ongoing business functions. - Cultural and organizational resistance
Shifting toward stronger cybersecurity practices requires more than policies; it requires mindset change. Employees may resist new workflows or tools, and leaders may hesitate to invest without visible short-term value. Ongoing communication, training, and executive sponsorship can help teams embrace security responsibilities and integrate them naturally into daily work. - Resource constraints
For smaller or growing organizations, dedicating the required time, staff, and funding to framework adoption can be challenging. The certification process often demands new tools, additional training, and formalized processes. Strategic prioritization and phased implementation allow teams to progress steadily without straining business continuity. - Keeping pace with evolving threats
Cyber threats evolve faster than many organizations can update controls. Maintaining CSF certification requires staying informed about industry trends, emerging risks, and new attack methods. Regular reviews, testing, and updates ensure the framework remains relevant and effective in defending against real-world threats. - Complex regulatory environments
Organizations operating globally must reconcile overlapping and sometimes conflicting regulations. Mapping CSF controls to regional and industry-specific compliance standards requires collaboration across legal, IT, and operational teams. Establishing a unified governance approach helps streamline audits and ensures alignment across multiple regulatory landscapes.
CSF certification may come with challenges, but each obstacle presents an opportunity to strengthen cybersecurity maturity. With preparation, leadership support, and a commitment to continuous improvement, organizations can overcome these hurdles and build a resilient, sustainable cybersecurity foundation that supports long-term trust, compliance, and risk management.
CISOs’ Guide: Automate Security, Privacy, and AI Risk Assessments
Download our latest guide on Automate Security, Privacy, and AI Risk Assessments.
How organizations can prepare for CSF certification
Given its many benefits, organizations interested in CSF certification should start by establishing a clear, realistic plan that accounts for both current capabilities and future growth. Here are some practical steps for those preparing to embark on this journey:
- Gain executive support
Leadership must understand the importance of cybersecurity and be willing to back the necessary investments in time, money, and resources. This support is crucial for overcoming internal resistance and driving change across the organization. - Conduct a thorough risk assessment
Before diving into improvements, organizations should perform a detailed risk assessment to understand which areas require immediate attention. This process should include input from multiple departments to gather an all-encompassing view of vulnerabilities and potential threats. - Invest in training
An informed workforce is often the best defense against cybersecurity incidents. Organizations should provide comprehensive training programs to educate employees on proper practices and highlight the importance of adherence to the CSF framework. - Embrace a continuous improvement mindset
CSF certification is not static. It demands ongoing effort to monitor, review, and update security measures as threats evolve. A culture of continuous improvement will ensure that cybersecurity remains a priority at every level of the organization. - Work with experts
Navigating the detailed requirements of a cybersecurity framework can be complex. Engaging external consultants or training internal compliance teams can greatly simplify the process and ensure that no critical areas are overlooked. - Create a roadmap with clear milestones
A well-documented plan helps track progress and delineates responsibilities. Establish short-term and long-term goals to maintain momentum, ensuring that the organization remains committed to achieving and maintaining certification.
By following these steps, organizations not only prepare for CSF certification but also embed a risk-aware culture within their operational fabric, one that can adjust to new challenges as and when they arise.
Summing it up
CSF certification stands as a robust testament to an organization’s commitment to cybersecurity and its proactive approach to risk management. In an era where data breaches and cyberattacks can have far-reaching consequences, having a recognized and trusted security framework is both a strategic asset and a competitive differentiator. Certification not only provides tangible benefits in terms of regulatory compliance and stakeholder confidence but also strengthens the overall operational resilience.
As discussed throughout this article, the journey to CSF certification involves meticulous planning, a balanced blend of technology and human expertise, and a commitment to continuous improvement. Whether you are a large enterprise or a smaller business, embracing the principles behind CSF certification will ensure that you are well-equipped to tackle the evolving cybersecurity landscape.
FAQs
What is the NIST Cybersecurity Framework (CSF), and what does CSF certification signify?
The NIST Cybersecurity Framework (CSF) is a voluntary set of guidelines developed by the National Institute of Standards and Technology to help organizations manage and reduce cybersecurity risks. It focuses on five core functions: Identify, Protect, Detect, Respond, and Recover.
CSF certification is formal recognition that an organization has successfully implemented the framework’s guidelines and demonstrates a commitment to managing and reducing cybersecurity risks. It’s not a pass/fail test but an evaluation of how well an organization has implemented the CSF’s functions.
What are the key components of the CSF certification process?
The CSF certification process involves several key components: a self-assessment of current practices, a gap analysis to identify areas needing improvement, thorough documentation of cybersecurity policies and procedures, implementation of risk management plans, and a commitment to continuous improvement through regular evaluations and updates.
Why is CSF certification important for organizations?
CSF certification offers numerous benefits, including enhanced cybersecurity practices aligned with industry standards, mitigation of risks leading to fewer data breaches and financial losses, improved compliance with regulatory requirements like HIPAA and GDPR, a competitive advantage by demonstrating commitment to security, enhanced incident response capabilities, and an improved reputation by fostering trust with customers and stakeholders.
How does the NIST CSF help organizations with risk management?
The NIST CSF provides a structured and comprehensive approach to identifying, assessing, and prioritizing cybersecurity risks based on their potential impact on business operations. This allows organizations to allocate resources effectively to address the most critical threats and develop risk management plans to mitigate those risks. The focus on risk management is a core component of the framework and the certification process.
How is the NIST CSF different from other cybersecurity frameworks like ISO 27001?
While the NIST CSF is a widely recognized framework, other options like ISO 27001, COBIT, and HITRUST exist. A key difference is that the NIST CSF emphasizes a risk management approach and is highly adaptable to various organizational structures, sizes, and sectors. It is designed to be flexible and scalable. The choice of framework often depends on industry, regulatory requirements, and specific organizational needs.
What are the steps for implementing the NIST CSF within an organization?
Implementing the NIST CSF involves several steps: establishing a cybersecurity governance structure with a responsible team, conducting a gap analysis to identify shortcomings, developing a roadmap with timelines and resource allocation, deploying cybersecurity controls, establishing continuous monitoring and improvement processes, and providing staff with cybersecurity training. The process is structured to ensure a comprehensive and effective implementation of the framework.