
Developing a strategic segregation of duties matrix
On this page
ToggleOverview
This article provides a comprehensive guide to developing and implementing a segregation of duties (SoD) matrix. It explains the purpose, components, and benefits of an SoD matrix, offering a step-by-step process for creation and highlighting best practices. The document also addresses common challenges and mistakes, providing examples and checklists to aid implementation. Developing a segregation of duties matrix emerges as a strategic imperative as organizations strive for operational excellence and financial integrity.
What is a segregation of duties matrix?
A segregation of duties matrix is a structured tool used in organizations to prevent conflicts of interest, fraud, and errors by delineating the responsibilities and access rights of various job roles. This matrix serves as a critical component of internal controls and governance, risk management, and compliance (GRC) efforts. In a typical SoD matrix, job roles and specific tasks or access rights are systematically cross-referenced, enabling organizations to identify potential conflicts where one individual or role has access to multiple duties that should ideally be separated.
The primary goal is to maintain transparency, integrity, and accountability within an organization by ensuring that no single person has unchecked control over a critical business process or system. Effective SoD matrices are dynamic documents that are regularly reviewed and updated to adapt to evolving organizational structures, processes, and regulatory requirements.

Here are five key points about what a segregation of duties matrix is:
- Definition and Purpose
A segregation of duties matrix is a visual tool that outlines and ensures the separation of responsibilities among different individuals or teams within an organization. Its primary purpose is to prevent conflicts of interest, reduce the risk of errors and fraud, and ensure that no single person has excessive control over critical processes. - Components and Structure
The matrix typically includes rows representing key tasks or processes (such as authorization, execution, and review) and columns representing different roles or individuals within the organization. Each cell in the matrix indicates which role is responsible for which task, highlighting areas where duties are appropriately separated or where potential conflicts may exist. - Implementation and Use
To implement an SoD matrix, an organization first identifies its key processes and the associated tasks. Then, it assigns these tasks to different roles or individuals to ensure appropriate separation. The matrix is regularly reviewed and updated to reflect changes in roles, processes, or organizational structure, helping maintain effective internal controls. - Benefits
The primary benefits of using an SoD matrix include enhanced internal controls, reduced risk of fraud and errors, improved compliance with regulatory requirements, and increased operational efficiency. By clearly defining and separating duties, the matrix helps ensure that tasks are completed accurately and independently, enhancing the overall integrity of business processes. - Examples of Applications
An SoD matrix can be applied in various areas of an organization, such as financial processes (e.g., separating invoice approval and payment processing), IT functions (e.g., separating system development and testing), and procurement processes (e.g., separating vendor selection and purchase order approval). It is particularly useful in industries with stringent regulatory requirements, such as finance, healthcare, and manufacturing.
A segregation of duties matrix is a crucial tool for enhancing internal controls, ensuring the separation of responsibilities, and mitigating risks within an organization.
Creating and maintaining a segregation of duties matrix requires a thorough understanding of an organization’s operations, regulatory standards, and best practices. It also necessitates collaboration between departments, from finance and human resources to IT and compliance teams. By systematically mapping out job roles and their associated tasks and access rights, organizations can not only prevent conflicts and fraud but also enhance operational efficiency and compliance with regulatory standards. SoD matrices play a crucial role in both risk management and good governance, ensuring that an organization operates with transparency, accountability, and minimized risk.

Looking for automated, always-on IT control assurance?
TrustCloud keeps your compliance audit-ready so you never miss a beat.
Learn MoreHow do I develop it?
Developing a SoD matrix is a meticulous and essential process for organizations seeking to enhance their internal controls and prevent conflicts of interest, fraud, and errors. It entails the systematic identification of job roles, responsibilities, and access rights within an organization and cross-referencing these elements to pinpoint potential conflicts. Regulatory requirements, compliance standards, and best practices guide the creation of SoD rules that dictate which combinations of duties and access should be separated.
The resulting matrix provides a clear visual representation of the organization’s internal control landscape, allowing for the identification of conflicts and the formulation of mitigation strategies. By continuously updating and maintaining this matrix, organizations can minimize risks, bolster transparency, and demonstrate their commitment to sound governance and risk management practices.
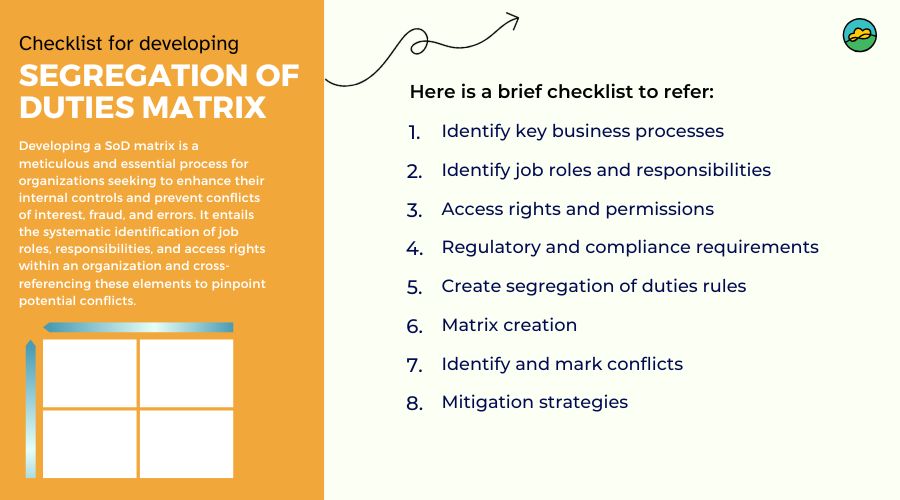
Here is a brief checklist to refer to while developing a SoD matrix:
- Identify key business processes
Begin by identifying the critical business processes within your organization. This may include financial processes, procurement, human resources, and IT operations. - Identify job roles and responsibilities
Document the various job roles and responsibilities within your organization. Be specific and comprehensive, covering all relevant departments and functions. - Access rights and permissions
Identify the access rights and permissions required for each job role to perform their tasks effectively. This includes access to systems, applications, data, and physical resources. - Regulatory and compliance requirements
Familiarize yourself with the regulatory and compliance standards relevant to your industry and organization. Understand the specific SoD requirements outlined in these standards. - Create SoD rules
Develop a set of SoD rules and policies based on regulatory requirements and best practices. These rules should specify which combinations of duties and access rights should be segregated. - Matrix creation
Develop a matrix that cross-references job roles with specific duties and access rights. Create columns to represent job roles and rows for duties or access rights. - Identify and mark conflicts
In the matrix, identify and mark the intersections where conflicts exist based on your SoD rules. Conflicts occur when a single individual or role has access to multiple duties or permissions that should be segregated. - Mitigation strategies
For each identified conflict, develop mitigation strategies. These strategies could involve process redesign, role redefinition, or additional controls to ensure proper segregation. Prioritize conflicts based on risk and impact.
Refer to this checklist to regularly review and update the segregation of duties matrix to stay aligned with changes in your organization, processes, or regulatory requirements. Maintain clear documentation of your SoD efforts, as this information is essential for audits, compliance, and demonstrating your commitment to proper internal controls. Effective SoD matrices are instrumental in preventing conflicts, fraud, and errors, ensuring a strong foundation for governance and risk management within your organization.
Read the “Acceptable use policy: balancing employee freedom with organizational security” article to learn more!
An example
A segregation of duties matrix typically includes a grid that cross-references job roles or positions within an organization with specific tasks or access rights that should be segregated to prevent conflicts of interest or fraud. Here’s a simplified example of what a SoD matrix might look like:

The green boxes in the above segregation of duties matrix tasks indicate that there is no SOD conflict. For example, Employee 1 is authorized to verify and enter invoices into the payment or accounting system. The red boxes indicate tasks where a SOD conflict exists. For example, Employee 2 is authorized to approve payments, so they should not be verifying and entering invoices, issuing payments, or updating accounting records.
Credit : Google Search
Best practices when developing segregation of duties matrix
Developing a Segregation of Duties (SoD) matrix is crucial for minimizing the risk of fraud and errors by ensuring that no single individual has control over all aspects of any critical business function. Here are some best practices to consider:
- Clearly define roles and responsibilities
Clear role definitions help ensure that employees understand their duties and the boundaries of their authority. Document detailed job descriptions and responsibilities for each role. Ensure that these are communicated effectively to all employees. By having well-defined roles, you can more easily identify potential conflicts and assign tasks in a way that minimizes risk. - Identify and map critical tasks
Understanding which tasks are critical helps focus on areas where segregation of duties is most needed. Create a comprehensive list of critical tasks within each process, particularly those related to authorization, asset custody, transaction recording, and reconciliation. Use this list to map out who performs each task, ensuring that no single individual has control over incompatible duties. - Use a visual matrix format
A visual matrix makes it easier to spot overlaps and potential conflicts at a glance. Develop a segregation of duties matrix that lists roles on one axis and tasks across the other. Fill in the matrix to show which roles are responsible for which tasks. This visual representation helps quickly identify any areas where segregation of duties is not properly enforced. - Implement access controls and automation
Automation and access controls help enforce segregation of duties and reduce the chance of human error. Use role-based access control (RBAC) systems to enforce the SoD matrix. Implement automated workflows and checks to ensure that tasks requiring segregation cannot be performed by the same individual without appropriate oversight. - Regular review and update
Business processes and personnel change over time, and the SoD matrix needs to be current to remain effective. Schedule regular reviews of the segregation of duties matrix, especially after organizational changes such as new hires, role changes, or process updates. Ensure that any changes in responsibilities or processes are reflected in the matrix. Conduct periodic audits to test compliance with the SoD matrix and adjust as necessary.
By adhering to these best practices, organizations can create a robust segregation of duties matrix that helps mitigate risks, enhance internal controls, and ensure compliance with regulatory requirements.
The success of a segregation of duties matrix hinges on its implementation. Best practices include securing top management support, fostering a culture of compliance, providing adequate training to employees, and leveraging technology to streamline the process. Clear communication and periodic reviews are also essential to ensure that the matrix is effectively integrated into the organization’s operations.
Benefits of developing segregation of duties matrix
The benefits of implementing a segregation of duties matrix are manifold. It not only enhances the reliability and integrity of financial reporting but also strengthens the organization’s internal controls, reduces the risk of fraud, and promotes operational efficiency. Moreover, it contributes to a culture of transparency and accountability within the organization.
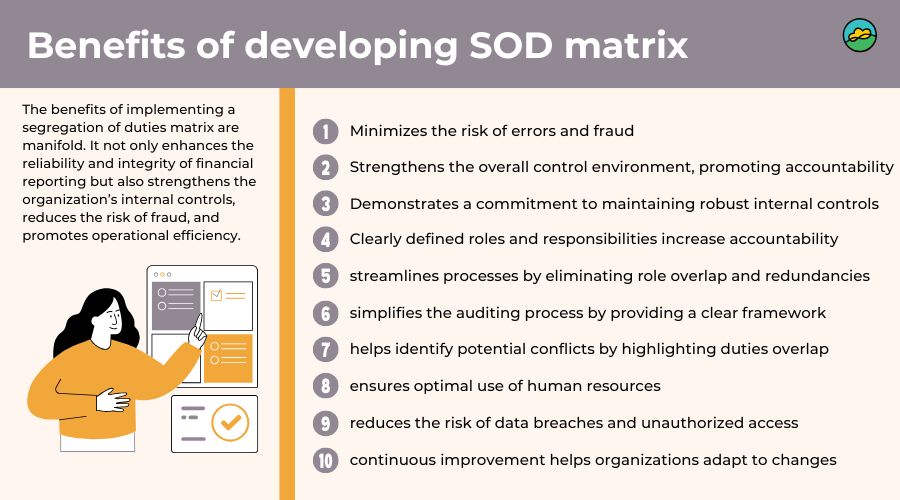
Here are some key advantages:
- Risk Reduction
By clearly defining and separating critical tasks, an SoD matrix minimizes the risk of errors and fraud. It ensures that no single individual has control over all aspects of any critical process, reducing opportunities for misconduct. - Improved Internal Controls
The matrix provides a structured approach to internal controls, helping to identify and address potential weaknesses. This strengthens the overall control environment, promoting accountability and transparency. - Regulatory Compliance
An SoD matrix helps organizations comply with regulatory requirements and industry standards, such as Sarbanes-Oxley (SOX). It demonstrates a commitment to maintaining robust internal controls, which can be crucial during audits and assessments. - Enhanced Accountability
Clearly defined roles and responsibilities increase accountability. Employees understand their specific duties and the boundaries of their authority, which helps prevent unauthorized actions and ensures tasks are completed correctly. - Efficiency and Clarity
The matrix streamlines processes by eliminating role overlap and redundancies. This clarity improves workflow efficiency, as employees are aware of their responsibilities and can focus on their specific tasks without confusion. - Audit Facilitation
An SoD matrix simplifies the auditing process by providing a clear framework of responsibilities and control points. Auditors can easily assess compliance with internal controls and identify any deviations or weaknesses. - Conflict Identification
The matrix helps identify potential conflicts of interest by highlighting where duties overlap. This allows organizations to proactively address and mitigate these conflicts before they lead to issues. - Better Resource Allocation
By clearly delineating duties, the matrix ensures optimal use of human resources. It helps align employees’ skills and roles, leading to better task performance and resource management. - Enhanced Security
Segregating duties reduces the risk of data breaches and unauthorized access to sensitive information. It ensures that no single employee has excessive control over critical systems or data. - Continuous Improvement
Regularly updating the SoD matrix as part of a continuous improvement process helps organizations adapt to changes in their operational environment, technology, and regulatory landscape. This keeps internal controls effective and relevant.
Overall, developing a segregation of duties matrix fosters a culture of integrity, efficiency, and compliance, thereby strengthening an organization’s operational framework and safeguarding its assets.
Read the “Boost security with smart employee workstation monitoring” article to learn more!
Challenges and common mistakes
Implementing a segregation of duties (SoD) matrix is crucial for ensuring proper internal controls and preventing fraud, errors, and conflicts of interest within an organization. However, several challenges and common mistakes can arise during the implementation process:
- Lack of understanding
One of the most common challenges is a lack of understanding of the principles and importance of segregation of duties. Without clear awareness of SoD concepts and their significance, organizations may struggle to develop an effective matrix. - Complexity of organizational structure
Organizations with complex structures, multiple business units, or decentralized operations may find it challenging to define clear roles and responsibilities and map them to specific activities. This complexity can lead to confusion and inconsistencies in the SoD matrix. - Limited resources and expertise
Small or resource-constrained organizations may lack the necessary resources, expertise, or dedicated personnel to develop and implement a segregation of duties matrix effectively. As a result, they may overlook critical risks or fail to address SoD requirements adequately. - Over-reliance on manual processes
Relying on manual processes to identify and manage segregation of duties can be time-consuming, error-prone, and inefficient. Organizations may struggle to keep the segregation of duties matrix up-to-date or may overlook subtle conflicts or violations. - Resistance to change
Resistance from employees or stakeholders who are accustomed to existing roles and responsibilities can hinder the implementation of a segregation of duties matrix. Resistance may arise due to concerns about increased scrutiny, changes to workflows, or perceived loss of autonomy. - Insufficient communication and training
Failure to communicate the purpose, objectives, and requirements of the segregation of duties matrix to employees can lead to misunderstanding and resistance. Insufficient training on SoD principles and procedures may result in inadequate compliance and adherence to the matrix. - Incomplete or inaccurate mapping
Inaccuracies or omissions in mapping roles to activities within the SoD matrix can result in gaps or overlaps in responsibilities. Failure to identify all relevant processes or roles can leave critical areas unaddressed, compromising the effectiveness of internal controls. - Inadequate monitoring and review
Establishing segregation of duties is not a one-time effort but requires ongoing monitoring, review, and adjustment to remain effective. Failure to regularly review and update the SoD matrix can result in outdated controls and missed opportunities for improvement.
To address these challenges and avoid common mistakes, organizations should prioritize education and awareness, allocate sufficient resources and expertise, streamline processes using automation and technology, foster open communication and collaboration, and establish a culture of continuous improvement and accountability. Regular audits and assessments can help identify issues and ensure that the segregation of duties matrix remains effective in mitigating risks and promoting sound internal controls.
Read the “Empower employees to handle IS issues with smart guidance” article to learn more!
Operationalizing your SoD matrix with automation and continuous monitoring
Designing a segregation of duties matrix is only the first step; the real value appears when you operationalize it with automation and continuous monitoring across your applications and infrastructure. A modern approach starts by integrating your SoD rules into identity and access management (IAM) and governance tools, so conflicting role combinations are automatically flagged, or blocked, at the point of provisioning.
When a manager requests new access for a team member, the system should check the SoD matrix in real time and either deny the request, route it for compensating control approval, or suggest alternative roles that avoid conflicts. This not only reduces manual review effort but also shrinks the window of exposure from weeks to minutes. By wiring the matrix directly into your joiner–mover–leaver processes, you ensure that promotions, lateral moves, and project-based access grants do not quietly erode carefully designed internal controls over time.
Continuous monitoring closes the loop by validating that your SoD design still matches reality as your environment and workforce evolve. Connect your ERP, HRIS, ticketing, and key SaaS systems to an SoD-aware monitoring layer that regularly compares actual user entitlements against your matrix, highlighting violations, unreviewed compensating controls, and “privilege creep” where access has accumulated beyond what the role requires. Dashboards can rank conflicts by financial impact or regulatory relevance, helping GRC and internal audit teams focus on the riskiest gaps instead of combing through thousands of low-priority exceptions. When issues are detected, workflows can automatically open remediation tickets, notify control owners, and capture evidence of resolution for future audits.
This transforms the SoD matrix from a static spreadsheet into a living control system, one that continuously enforces policy, documents oversight, and provides a defensible story to regulators, customers, and your board about how you prevent fraud and safeguard critical processes.
Summing it up
The objective of the segregation of duties matrix is to identify conflicts or situations where one individual or role has access to multiple tasks or access rights that should ideally be separated. In this example, you can see that both the Finance Manager and the Accounts Payable Clerk have access to Task A and Task B, which might be a potential conflict. Similarly, the HR Manager has access to both Task C and Task D, which should ideally be separated to maintain proper internal controls.
The segregation of duties matrix can be significantly more complex, with numerous tasks, roles, and access rights, and the identification and mitigation of conflicts require careful analysis and planning. The goal is to ensure that no one person or role has unchecked control over a process or system that could lead to financial irregularities, fraud, or other risks.
FAQs
What is a Segregation of Duties (SoD) matrix?
An SoD matrix is a structured tool that maps out key business activities and the roles responsible for each step. It helps ensure no single person has control over multiple phases of a critical process (e.g., initiation, approval, reconciliation). By visualizing role overlaps and conflict areas, organizations can quickly spot and address segregation gaps—reducing opportunities for fraud, errors, or compliance breaches.
Why is a strategic SoD matrix important?
A strategic SoD matrix does more than just list tasks and roles—it aligns with risk management priorities and business objectives. It highlights high-risk areas, guides resource allocation for control testing, and supports audit readiness. By focusing on strategic areas—such as financial transactions or sensitive data access—a well-designed matrix strengthens the control environment and reinforces governance across the organization.
How do you build an effective SoD matrix?
Building an SoD matrix involves several steps:
- Identify core processes (e.g., procure-to-pay, payroll, IT access).
- Define tasks within each process (e.g., create invoice, approve payment).
- List roles/functions responsible for each task.
- Map role-task assignments in a matrix structure.
- Flag conflicts where one role handles multiple critical steps.
- Remediate by splitting duties, adding oversight, or using compensating controls.
- Review and update the matrix routinely to adapt to organizational changes and emerging risks.
How often should the SoD matrix be reviewed?
An SoD matrix should be treated as a living document and reviewed at least annually—or more frequently if there are significant changes in processes, personnel, systems, or regulations. Regular reviews help catch newly introduced segregation conflicts, ensure remediation remains effective, and demonstrate audit readiness. Periodic refreshes also reinforce organizational awareness around internal controls and risk prevention.